

1.Configuring Remote Connections via SSH
SSH is a service for remotely connecting to servers, and it typically runs immediately after OS installation. However, the default configuration has some security vulnerabilities.
Here, we will modify the default settings to enhance the security of SSH connections
1.1 Modifying the SSH Service Configuration File
Modify the configuration file to change the SSH service settings.
The path for the SSH service configuration file has been changed from the previous "/etc/ssh/sshd_config" to "/usr/etc/ssh/sshd_config".
# vi /usr/etc/ssh/sshd_config

Line 20: Uncomment and change to any port number other than the default port.
Port 2244

Line 22: Uncomment
ListenAddress 0.0.0.0

Line 39: Uncomment(Password login not possible for root user)
PermitRootLogin prohibit-password
Restarting SSH
# systemctl enable sshd.service
# systemctl restart sshd.service
If you leave it as is, you won't be able to connect remotely via SSH after the next reboot. Please open SSH port 2244 in the following firewall settings.
2.How to configure the firewall (firewalld)
On openSUSE, firewalld is set as the default firewall and is enabled during OS installation
2.1 How to Use the "firewall-cmd" Command to Control "firewalld"
①firewalld operational status check
# firewall-cmd --state
If "firewalld" is running, it will display "running"; if it is stopped, it will display "not running".
➁About the "--permanent" Option
To prevent settings from being lost when restarting the server or the "firewalld" service,
you must configure settings using the "--permanent" option. When configuring with the "--permanent" option, the settings will not be reflected in "firewalld" immediately; you must use "firewall-cmd --reload" to apply the changes.
For example, to ensure an HTTP service remains available permanently without being reset upon system restart,
# firewall-cmd --add-service=http --permanent
# firewall-cmd --reload
➂Startup and Shutdown Procedures
firewalld is controlled by systemd, so use the systemctl command to start and stop it.
Starting firewalld
# systemctl start firewalld
Stopping firewalld
# systemctl stop firewalld
2.2 Release the modified SSH port 2244
# firewall-cmd --add-port=2244/tcp --permanent
# firewall-cmd --reload
3.Remote connection from Windows
Windows Settings
Begin configuring remote connections from Windows. Use the terminal emulator "Tera Term".
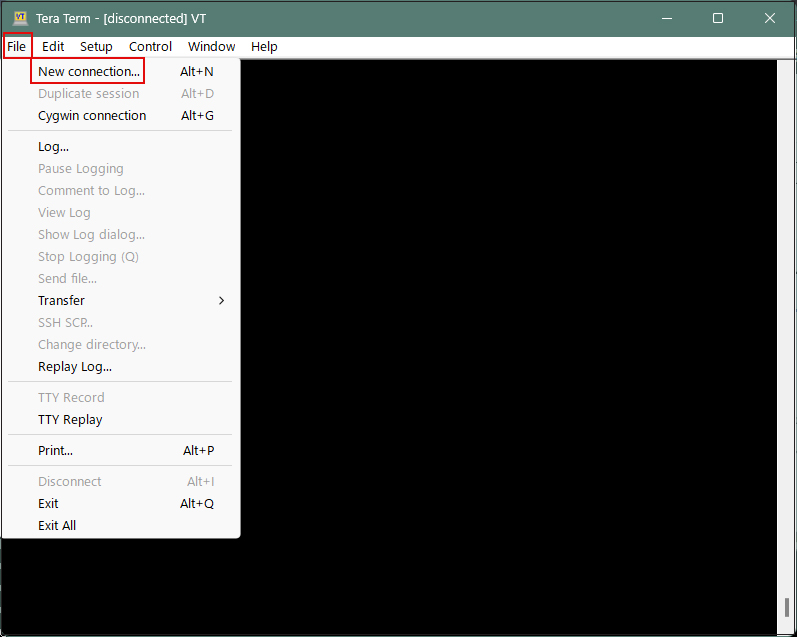
Launch Tera Term, cancel the startup screen, then select "New Connection" from the "File" menu in Tera Term.
The next screen will appear, so enter the following:
Host: The server's IP address
TCP port: The SSH port number you changed above
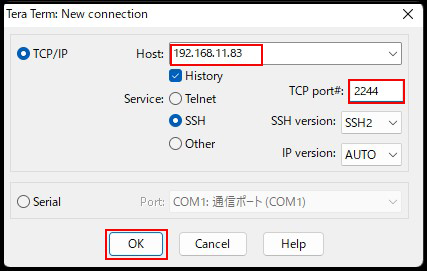
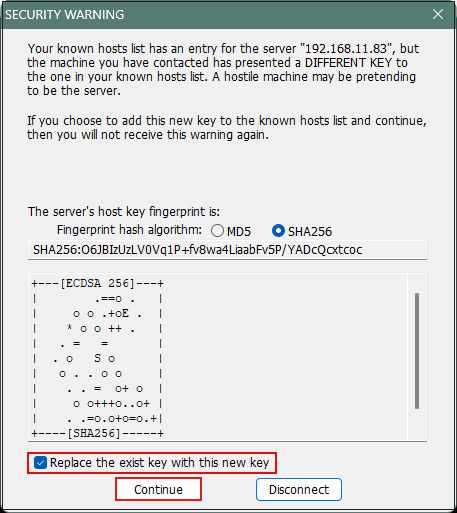
Click "OK" to proceed to the security confirmation screen. Check the box next to "Replace the exit key with this new key" and click "Continue".
The next screen will appear
User name: General login username
Passphrase: Password for the above user
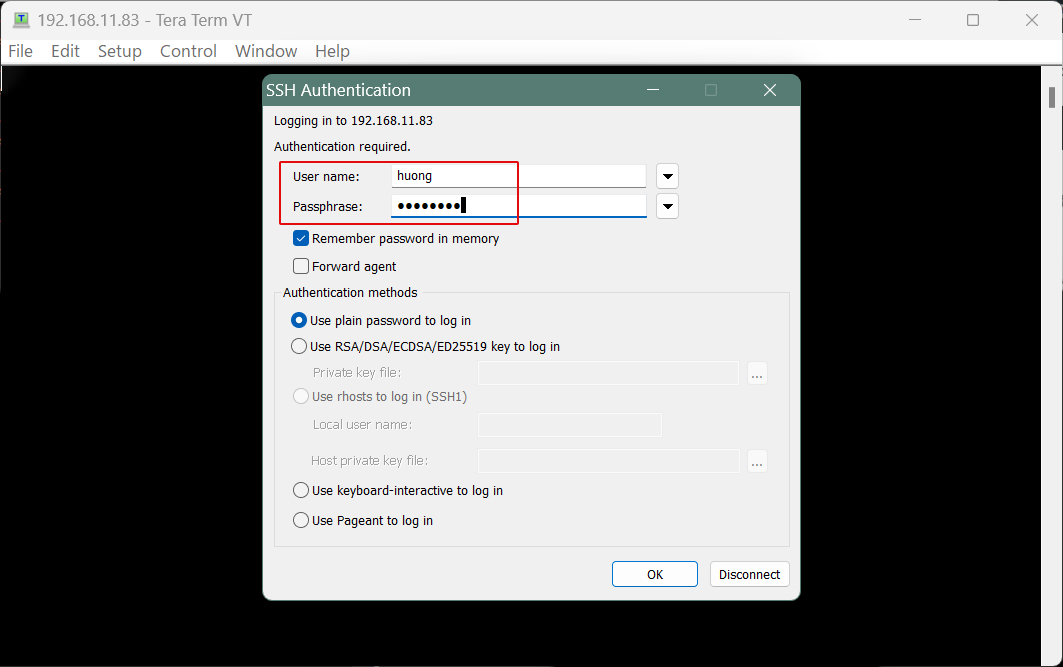
If the information is correct, you should be able to log in normally.
4. NTP Server Configuration
Install Chrony to set up an NTP server for time synchronization. Note that NTP uses port 123/UDP.
① Chrony Installation
# zypper -n install chrony
➁ Chrony Configuration
# vi /usr/etc/chrony.conf

# Line 8:Comment it out and add the following below it.
#! pool pool.ntp.org iburst
pool ntp.nict.jp iburst

# Per Line 29: Added the permitted range for time synchronization.
allow 192.168.11.0/24
# systemctl start chronyd
# systemctl enable chronyd
➂ Opening the NTP port
If Firewalld is enabled, you must allow the NTP service. Note that NTP uses port 123/UDP.
# firewall-cmd --add-service=ntp --permanent
success
# firewall-cmd --reload
success
④ Functionality Verification
# chronyc sources

MS Name/IP address         Stratum Poll Reach LastRx Last sample
===============================================================================
^- 208.88.66.8                   2   7   377    26   -919us[ -955us] +/-   32ms
^- vmi3026968.contaboserver>     2   7   337    90  +1144us[+1107us] +/-   90ms
^* 152.70.97.72                  2   7   377    25   +164us[ +129us] +/- 8687us
^+ 44.30.62.53                   2   7   377    24   -125us[ -125us] +/-   10ms