1. vsftpd( FTP Server )
1.1 Install
# zypper -n install vsftpd
1.2 Editing Configuration Files
I'll back up the unedited vsftpd.conf.
# cp /etc/vsftpd.conf /home/huong/vsftpd.conf.org
# vi /etc/vsftpd.conf

Line 19: Change
write_enable=YES

Line 36: Uncomment (Enable bulk transfer of entire directories)
ls_recurse_enable=YES

Line 57: Uncomment
local_umask=022

Lines 62, 63: Uncomment (chroot enabled)
chroot_local_user=YES
chroot_list_enable=YES

Line 65: Uncomment (chroot list file specification)
chroot_list_file=/etc/vsftpd.chroot_list

Line 80: Anonymous login prohibited
anonymous_enable=NO

Line 150: Comment it out and add it below.
#connect_from_port_20=YES
listen_port=21

Around line 173: Uncomment (Allow ASCII mode transfer)
ascii_download_enable=YES

Around line 185: Modify as needed (if listening only for IPv4)
listen=YES

Around line 190: Modify as needed (if listening only for IPv4)
# If YES, listen on both IPv4 and IPv6
listen_ipv6=NO

Around line 218: Uncomment (disable seccomp filter)
seccomp_sandbox=NO

Add to the last line
# Use local time
use_localtime=YES
Add users who are permitted to access the upper-level directory
# echo "huong" >> /etc/vsftpd.chroot_list
In my case, I wrote huong.
Enable vsftpd to start automatically and start it.
# systemctl enable vsftpd
# systemctl start vsftpd
1.3 firewall設定
Open FTP Port (FTP uses port 21)
# firewall-cmd --add-service=ftp --permanent
# firewall-cmd --reload
From the Windows side, I'll verify whether I can connect using FileZilla.
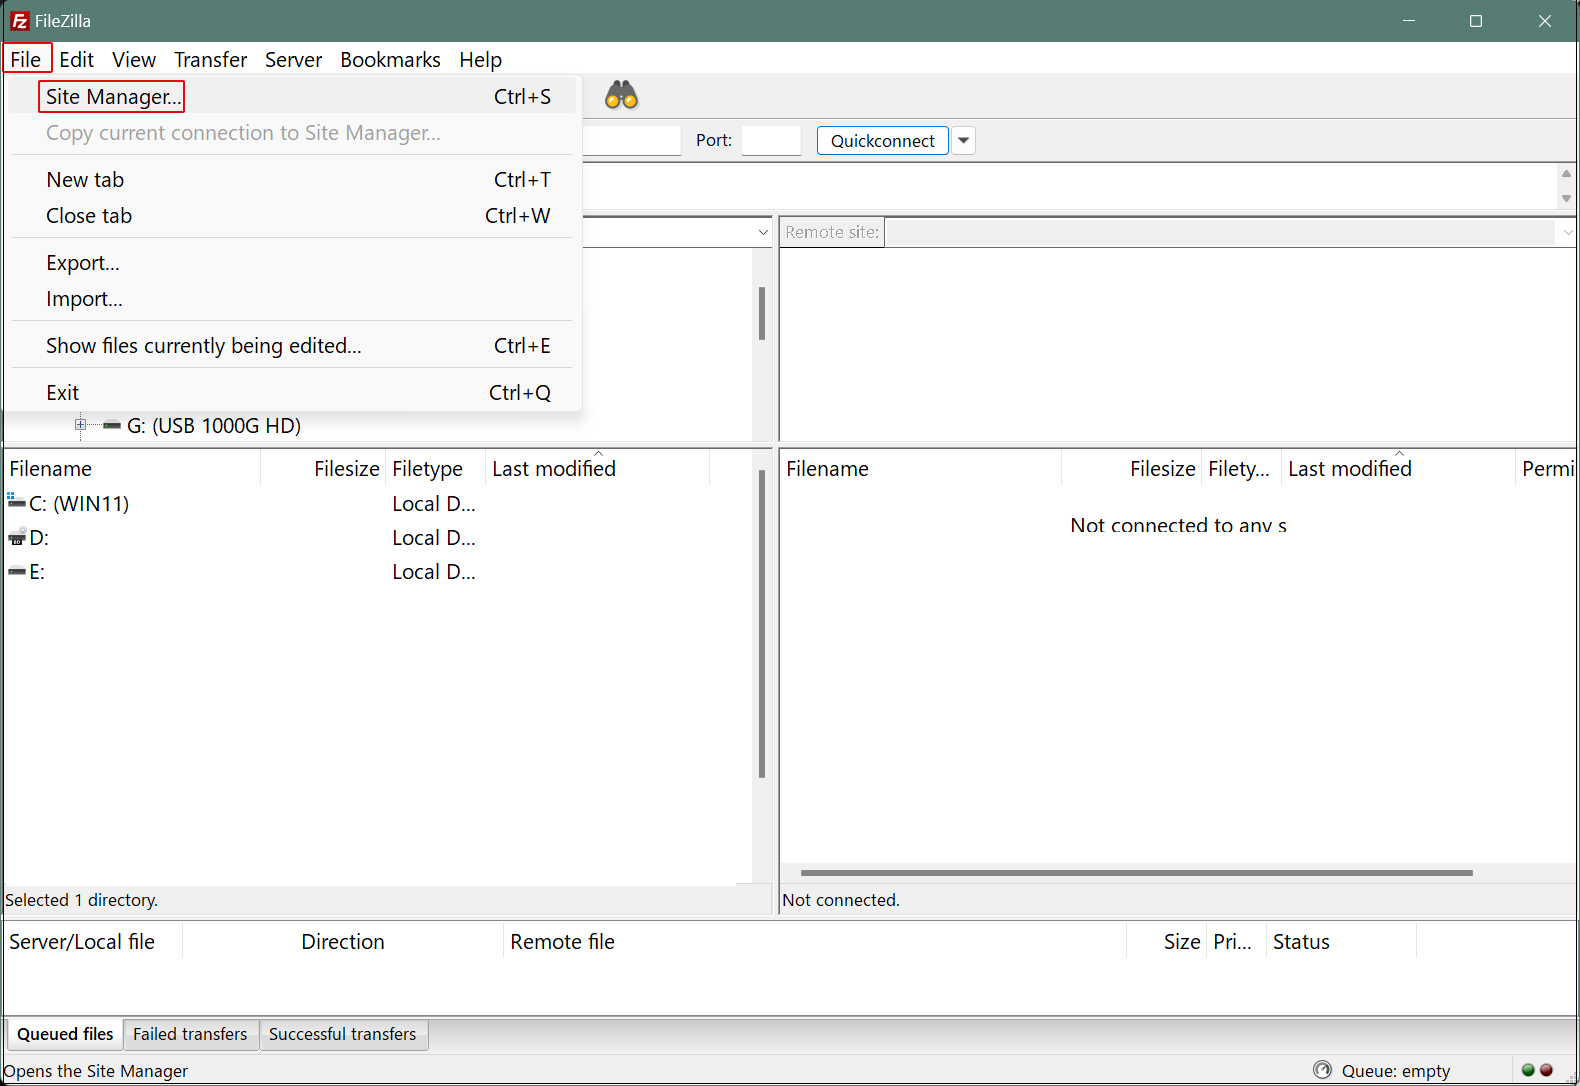
Launch FileZilla and select "Site Manager" from the "File" menu.
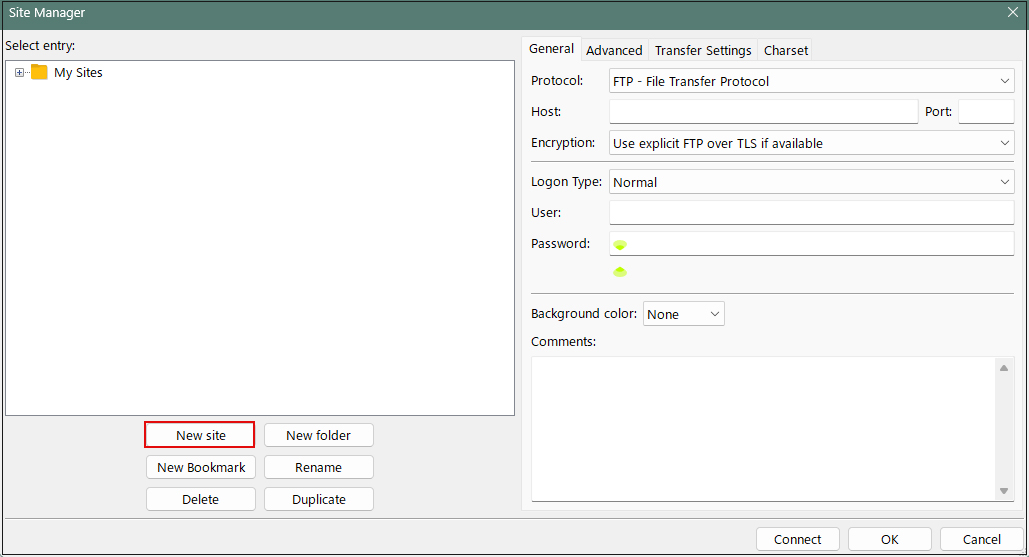
Click "New site"
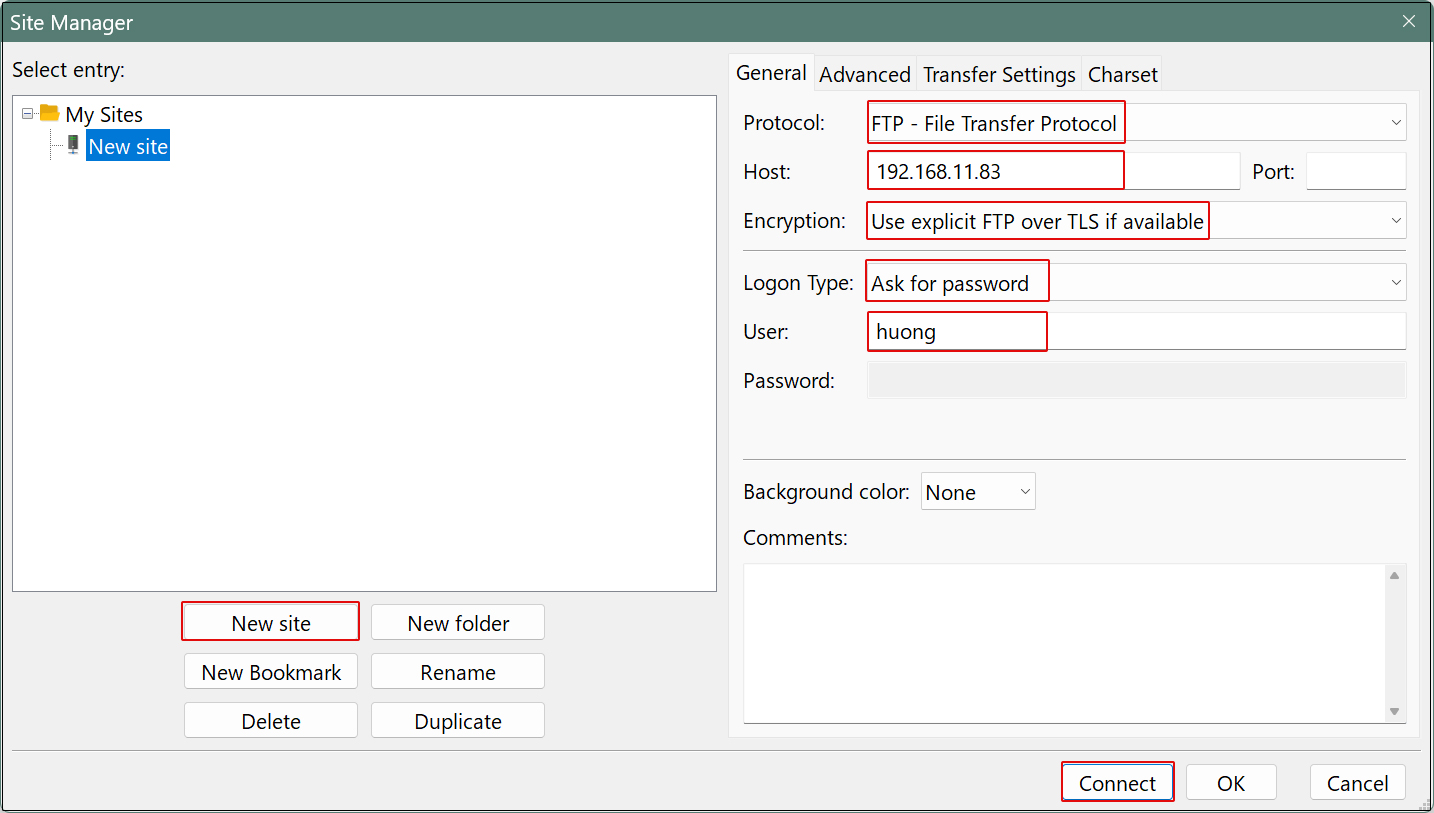
Enter the settings for each item as follows, then click "Connect":
Protocol: FTP - File Transfer Protocol
Host: Server IP address
Port: (Leave blank)
Encryption: Use explicit FTP over TLS if available
Logon Type: Ask for password
User: Server login user
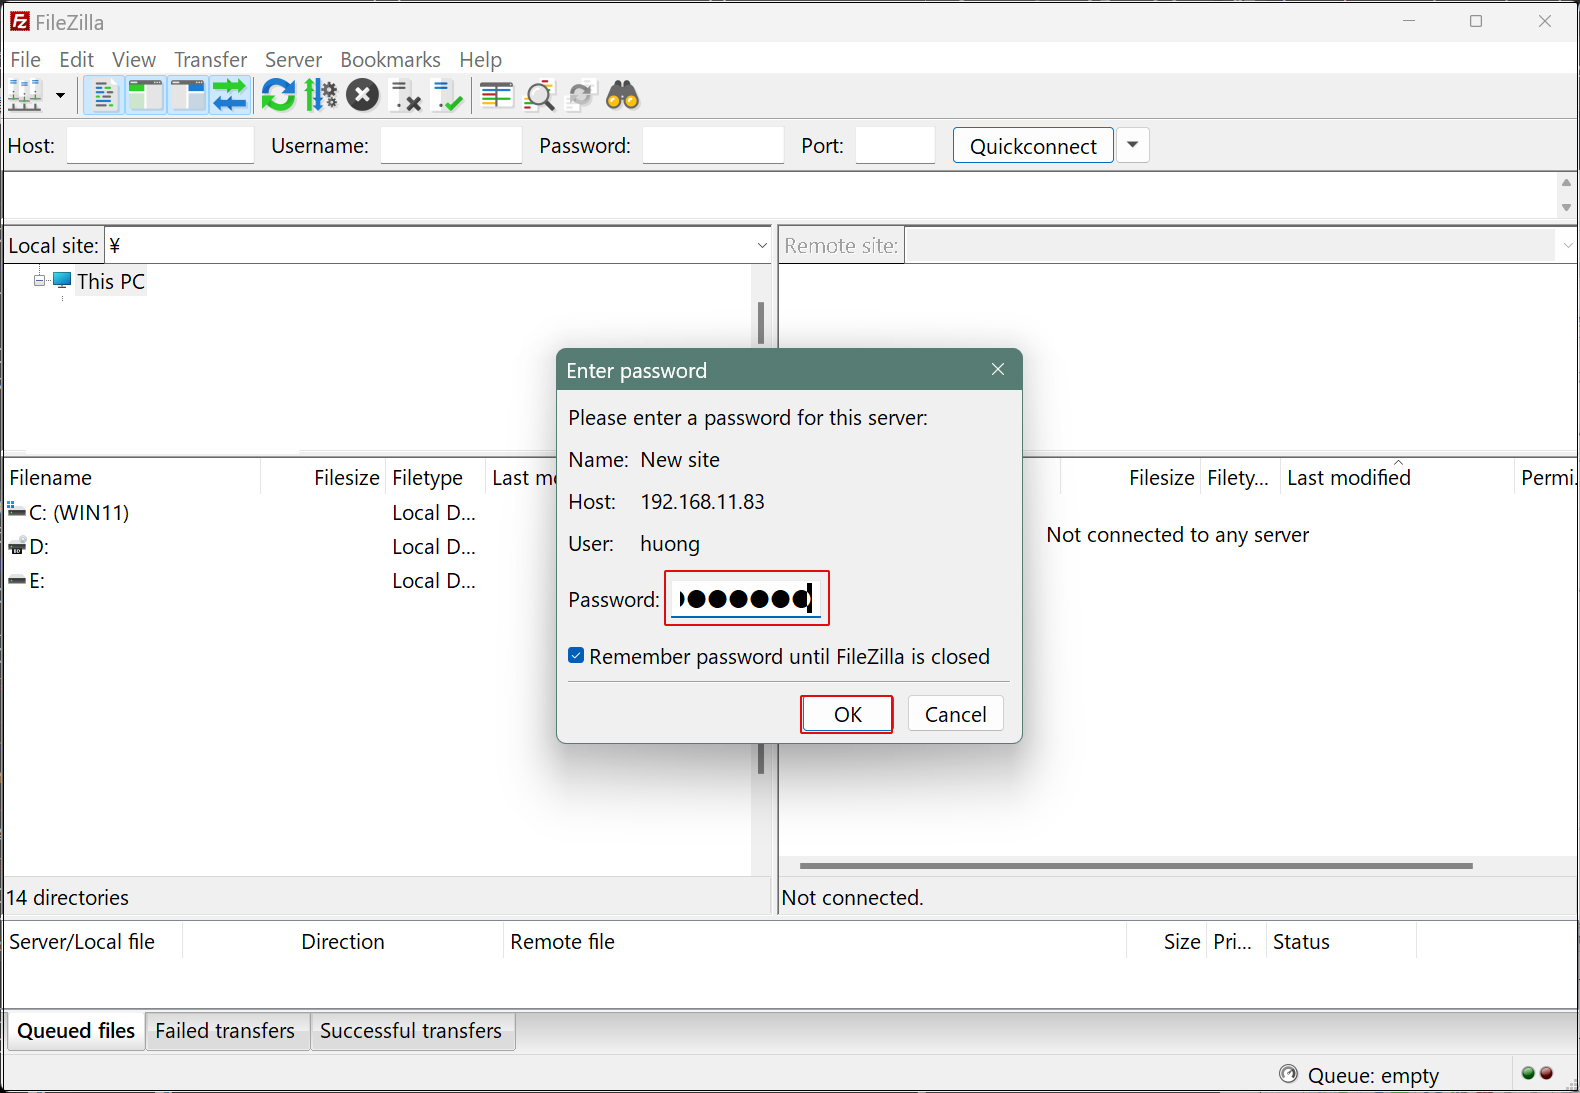
Set the login user's password in "Password" and click "OK".
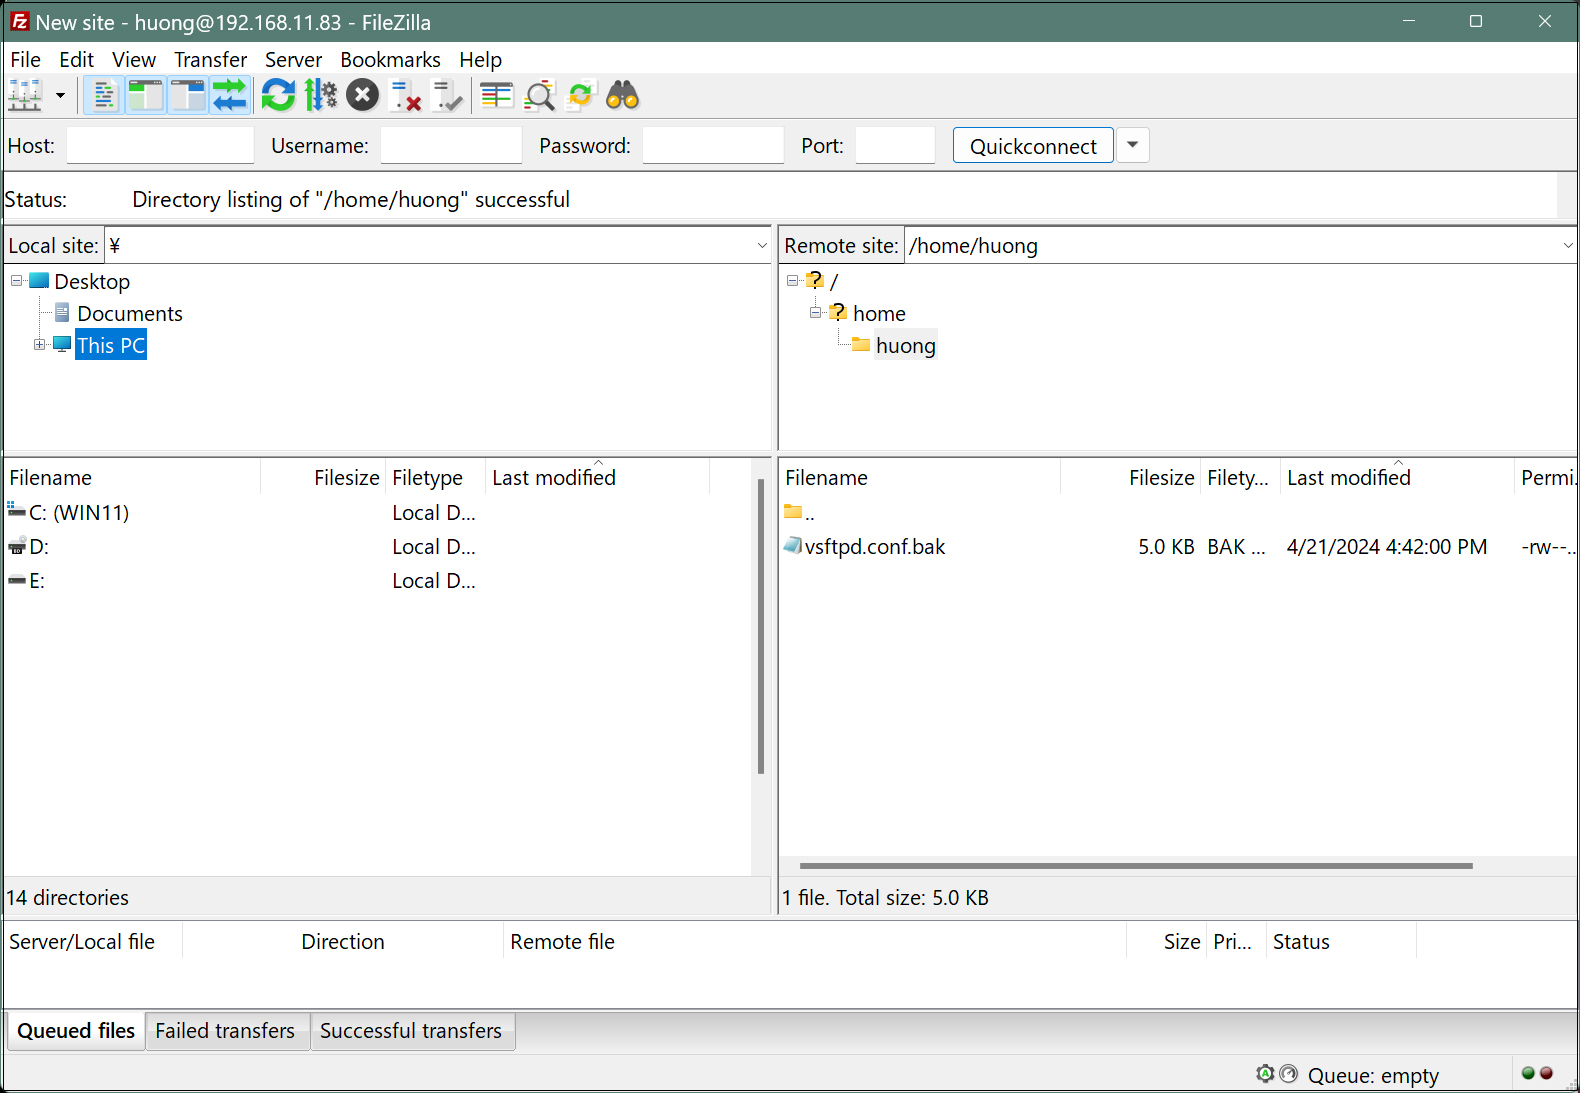
Upon successful connection, the server directory will appear on the right side and the Windows directory on the left side.
2. vsftpd SSL/TLS
Configure vsftpd to enable SSL/TLS
2.1 Create a self-signed certificate
This step is unnecessary when using trusted, legitimate certificates such as Let's Encrypt.
# cd /etc/ssl/private
/etc/ssl/private # openssl req -x509 -nodes -newkey rsa:2048 -keyout vsftpd.pem -out vsftpd.pem -days 365

-----
You are about to be asked to enter information that will be incorporated
into your certificate request.
What you are about to enter is what is called a Distinguished Name or a DN.
There are quite a few fields but you can leave some blank
For some fields there will be a default value,
If you enter '.', the field will be left blank.
-----
Country Name (2 letter code) [AU]:JP  Country code
State or Province Name (full name) [Some-State]:Osaka   Region (Prefecture)
Locality Name (eg, city) []:Sakai  city
Organization Name (eg, company) [Internet Widgits Pty Ltd]:private  Organization Name
Organizational Unit Name (eg, section) []:Admin  Department name within the organization
Common Name (e.g. server FQDN or YOUR name) []:Lepard  Hostname
Email Address []:hoge@hoge.com  Administrator Address
# chmod 600 vsftpd.pem
2.2 Editing the configuration file
# vi /etc/vsftpd.conf

Line 195: Change
ssl_enable=YES

Add to the last line
rsa_cert_file=/etc/ssl/private/vsftpd.pem
rsa_private_key_file=/etc/ssl/private/vsftpd.pem
ssl_ciphers=HIGH
force_local_data_ssl=YES
force_local_logins_ssl=YES

When using a passive port
Line 177
pasv_enable=YES
# systemctl restart vsftpd
2.3 Opening passive ports
# firewall-cmd --add-port=30000-30100/tcp --permanent
success
# firewall-cmd --reload
success
2.4 Connect with FileZilla
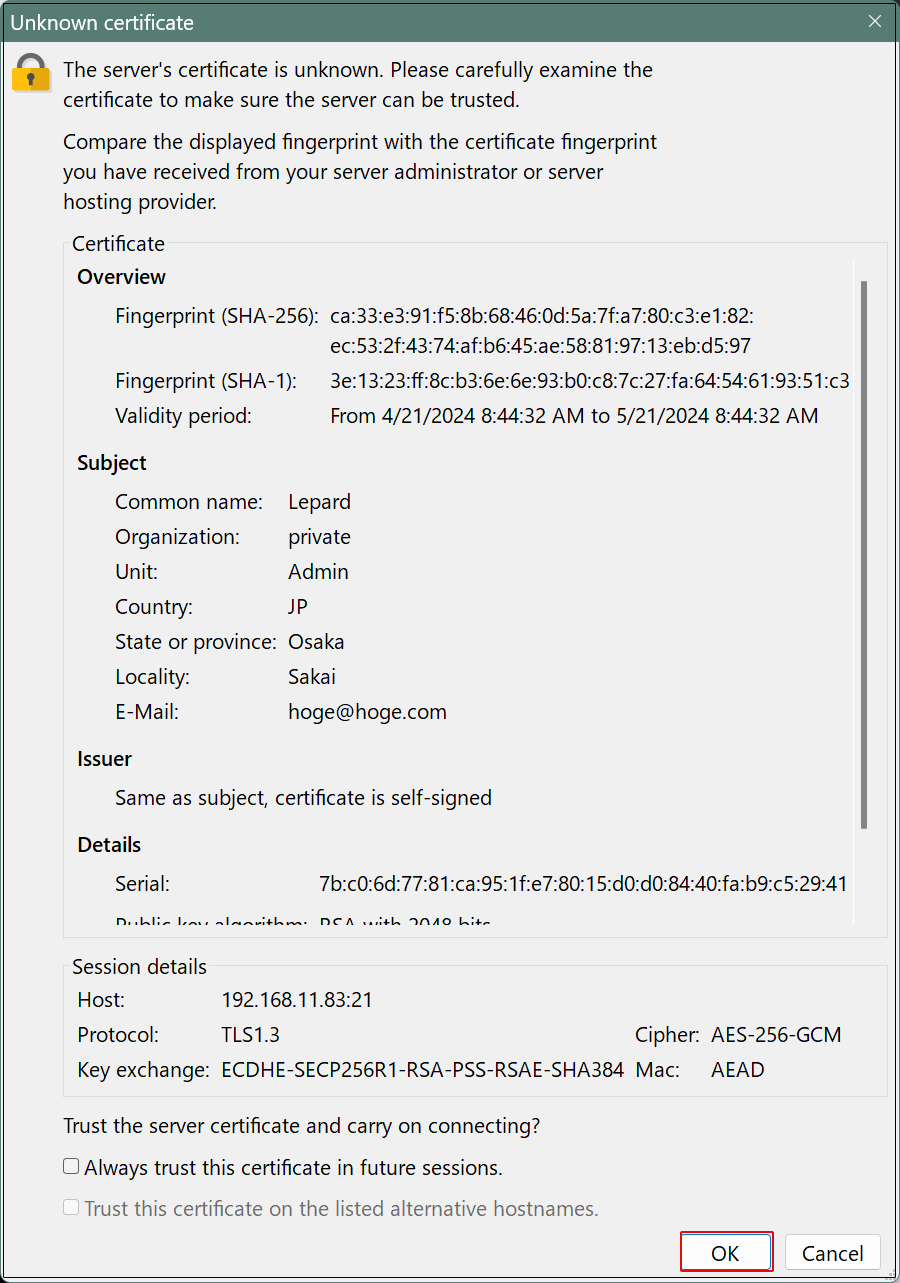
As mentioned earlier, when you connect to FileZilla, the following screen will appear. Check the box labeled "Always trust this certificate in future sessions" and click "OK." The connection will then be established as described earlier.