1.Apache2 installation and virtual host configuration
1.1 Apache2 Install
①httpd Install
# dnf -y install httpd

Check Version
# httpd -v
Server version: Apache/2.4.69 (Fedora Linux)
Server built:   Oct  1 2026 00:00:00
1.2 Apache Configuration
①Edit httpd.conf file
# cp /etc/httpd/conf/httpd.conf /etc/httpd/conf/httpd.conf_bak
# vi /etc/httpd/conf/httpd.conf
Line 91 : Specify administrator address
ServerAdmin [Email Address]

Per line 101: Change ServerName
#ServerName www.example.com:80
ServerName [Domain name]

Line 149 : Change (Indexes are deleted)
Options FollowSymLinks

Line 156 : Change
AllowOverride All

Line 169 : File names accessible by directory name only
Add "index.php index.cgi index.htm"

Add to the last line
ServerTokens Prod
②If Firewalld is enabled, HTTP service permission is required; use [80/TCP] for HTTP
# firewall-cmd --add-service=http --permanent
# firewall-cmd --reload
③Apache Auto-Start Configuration
# systemctl start httpd
# systemctl enable httpd
# systemctl status httpd
● httpd.service - The Apache HTTP Server
     Loaded: loaded (/usr/lib/systemd/system/httpd.service; enabled; preset: disabled)
    Drop-In: /usr/lib/systemd/system/service.d
             └─10-timeout-abort.conf
     Active: active (running) since Sun 2026-11-08 11:15:09 JST; 13s ago
 Invocation: 7a2137bd0e8b44f9994b013b20186b2d
       Docs: man:httpd.service(8)
   Main PID: 2035 (httpd)
     Status: "Total requests: 0; Idle/Busy workers 100/0;Requests/sec: 0; Bytes served/sec:   0 B/sec"
      Tasks: 177 (limit: 4564)
     Memory: 14.3M (peak: 14.4M)
        CPU: 99ms
     CGroup: /system.slice/httpd.service
             ├─2035 /usr/sbin/httpd -DFOREGROUND
             ├─2037 /usr/sbin/httpd -DFOREGROUND
             ├─2038 /usr/sbin/httpd -DFOREGROUND
             ├─2039 /usr/sbin/httpd -DFOREGROUND
             └─2040 /usr/sbin/httpd -DFOREGROUND

Nov 08 11:15:09 Lepard systemd[1]: Starting httpd.service - The Apache HTTP Server...
Nov 08 11:15:09 Lepard (httpd)[2035]: httpd.service: Referenced but unset environment variable evaluates to an emp>
Nov 08 11:15:09 Lepard httpd[2035]: Server configured, listening on: port 80
Nov 08 11:15:09 Lepard systemd[1]: Started httpd.service - The Apache HTTP Server.
④operation check
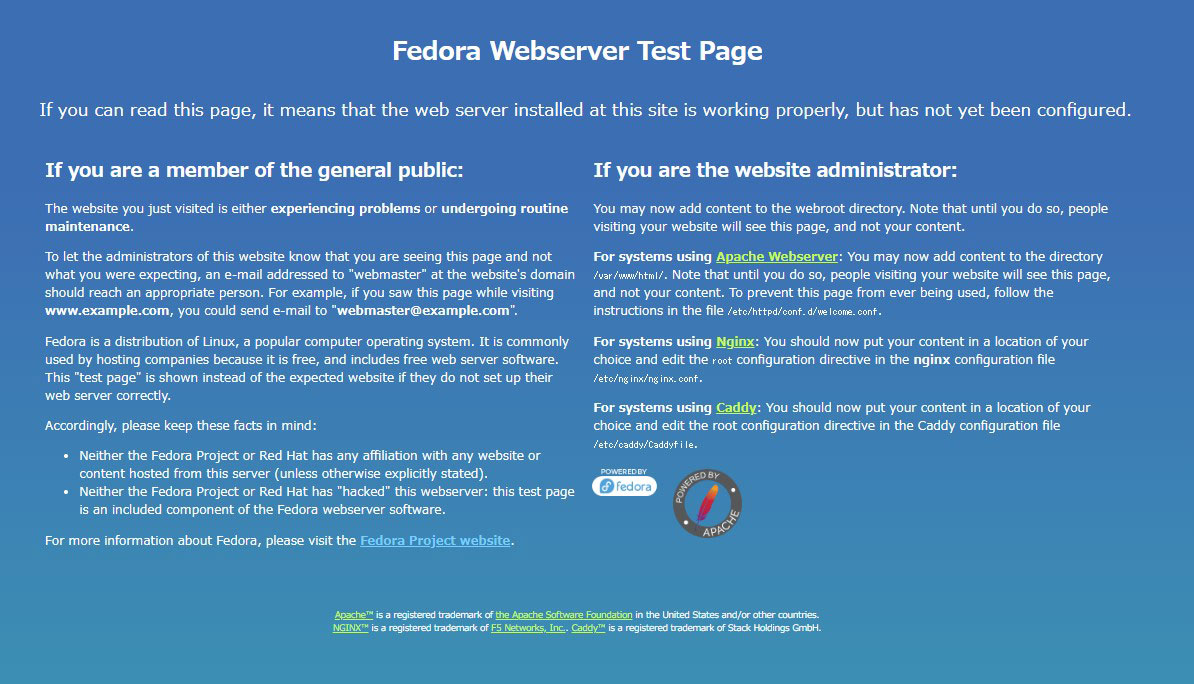
If you access http://[server IP address] and the Fedora Webserver Test Page is displayed as shown below, it is OK.
⑤Hide the Welcome page, create a new index.html file as a Test Page, and check apache operation
Rename the welcome page
# mv /etc/httpd/conf.d/welcome.conf /etc/httpd/conf.d/welcome.conf.org
Create an HTML test page and verify it.
# vi /var/www/html/index.html
<html>
<body>
<div style="width: 100%; font-size: 40px; font-weight: bold; text-align: center;">
Apache Test Page
</div>
</body>
</html>
If you access "http://[server IP address]" and the Test Page is displayed as shown below, it is OK.
1.3 Virtual Host Settings
Assign and configure the [FQDN] to be operated on the virtual host in the document root [/var/www/html/FQDN] directory
# vi /etc/httpd/conf.d/vhost.conf

#Configuring Virtual Host Domains
<VirtualHost *:80>
DocumentRoot /var/www/html/[FQDN]
ServerName [FQDN]
ServerAdmin [Email Address]  #Administrator email address
ErrorLog logs/[FQDN].error_log
CustomLog logs/[FQDN].access_log combined
</VirtualHost>

<Directory "/var/www/html/[FQDN]">
Options FollowSymLinks
AllowOverride All
</Directory>
Creating a Document Directory
# mkdir /var/www/html/[FQDN]
Apache restart
# systemctl restart httpd
Create test pages and check operation
# vi /var/www/html/[FQDN]/index.html

Fill in the following
<html>
<body>
<div style="width: 100%; font-size: 40px; font-weight: bold; text-align: center;">
Virtual Host Test Page
</div>
</body>
</html>
If you access http://[FQDN]/index.html with a browser, the following screen should appear.
2. Ensure CGI Script Usage
①Confirmation of CGI availability
# grep -n "^ *ScriptAlias" /etc/httpd/conf/httpd.conf
254:    ScriptAlias /cgi-bin/ "/var/www/cgi-bin/"
The above is displayed and available under "/var/www/cgi-bin/".
②Create test scripts and check operation
# vi /var/www/cgi-bin/index.cgi
Fill in the following
#!/usr/bin/python3
print("Content-type: text/html\n")
print("CGI Script Test Page")
# chmod 755 /var/www/cgi-bin/index.cgi
# curl localhost/cgi-bin/index.cgi
CGI Script Test Page
3. PHP installation and configuration
3.1.PHP Install
①Install
# dnf -y install php
②Version Check
# php -v
PHP 8.5.12 (cli) (built: Oct 19 2026 17:02:46) (NTS gcc x86_64)
Copyright (c) The PHP Group
Built by Fedora Project
Zend Engine v4.5.12, Copyright (c) Zend Technologies
    with Zend OPcache v8.5.12, Copyright (c), by Zend Technologies
Configure php-fpm
# systemctl enable php-fpm
Created symlink '/etc/systemd/system/multi-user.target.wants/php-fpm.service' → '/usr/lib/systemd/system/php-fpm.service'.
# systemctl start php-fpm
③Apache restatrt
After PHP installation, restarting Apache will invoke PHP-FPM (FPM : FastCGI Process Manager) by default, and php-fpm service will be started in conjunction with httpd startup.
# systemctl restart httpd
# systemctl status php-fpm
● php-fpm.service - The PHP FastCGI Process Manager
     Loaded: loaded (/usr/lib/systemd/system/php-fpm.service; enabled; preset: disabled)
    Drop-In: /usr/lib/systemd/system/service.d
             └─10-timeout-abort.conf
     Active: active (running) since Sun 2026-11-08 11:35:42 JST; 1min 9s ago
 Invocation: 9904c7f4fa4444e3aa6885bb66ce425c
   Main PID: 3242 (php-fpm)
     Status: "Processes active: 0, idle: 5, Requests: 0, slow: 0, Traffic: 0.00req/sec"
      Tasks: 6 (limit: 4564)
     Memory: 11.2M (peak: 11.6M)
        CPU: 75ms
     CGroup: /system.slice/php-fpm.service
             ├─3242 "php-fpm: master process (/etc/php-fpm.conf)"
             ├─3244 "php-fpm: pool www"
             ├─3245 "php-fpm: pool www"
             ├─3246 "php-fpm: pool www"
             ├─3247 "php-fpm: pool www"
             └─3248 "php-fpm: pool www"

Nov 08 11:35:41 Lepard systemd[1]: Starting php-fpm.service - The PHP FastCGI Process Manager...
Nov 08 11:35:42 Lepard systemd[1]: Started php-fpm.service - The PHP FastCGI Process Manager.
④Confirmation of PHP operation
Create the following file
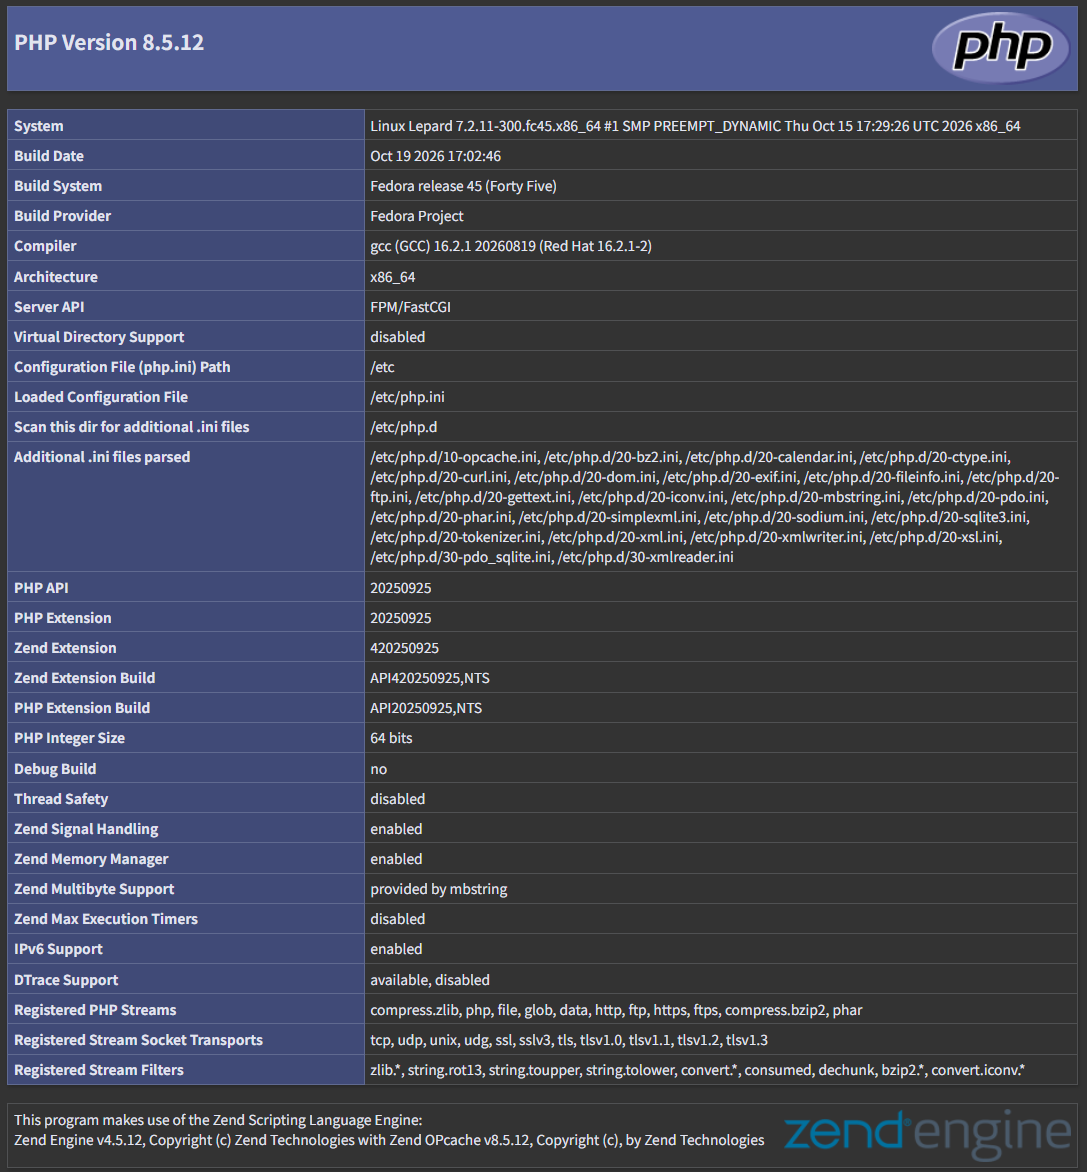
# vi /var/www/html/[FQDN]/test.php
<?php phpinfo(); ?>
Access http://[FQDN]/test.php and if the following screen appears, OK
4. Digest authentication in Apache2
Since Basic Authentication, a well-known authentication authentication method for http, transmits authentication information in plain text, there is a risk of ID and password leakage if the packet is intercepted.
On the other hand, Digest Authentication encrypts the authentication information and sends it in encrypted form, so there is almost no risk of information leakage
4.1 Create password file for Digest authentication
Specify an authenticated area called realm. This realm allows the same directory to be accessed as authenticated.
As an example, we will create a user named "secretuser" and a password file ".digestauth" with "DigestAuth" as the realm. Execute the following command and enter the password for "secretuser" when prompted
# /usr/bin/htdigest -c /etc/httpd/.digestauth "DigestAuth" secretuser
Confirmation
# cat /etc/httpd/.digestauth
secretuser:DigestAuth:xxxxxxxxxxxxxxxxxxxxxxxxxxxxxx
As above, secretuser and encrypted password are created
4.2 Edit Apache configuration file
Specify the directory to which Digest authentication will be applied. (In this case, specify the secret directory.)
# vi /etc/httpd/conf/httpd.conf
The following has been added to the end
<Directory "/var/www/html/[FQDN]/secret">
AuthType Digest
AuthName "DigestAuth"
AuthDigestDomain /[FQDN]/secret/
AuthUserFile "/etc/httpd/.digestauth"
Require valid-user
</Directory>
Create a directory for Digest authentication
# mkdir /var/www/html/[FQDN]/secret
Enable Digest authentication and reboot
# systemctl restart httpd.service
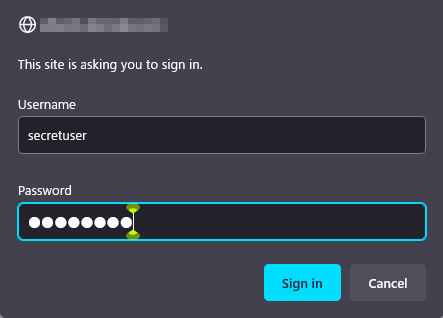
When accessing http://[FQDN]/secret with a browser, a screen appears asking for "user name" and "password".