Prerequisite
We will install Suricata IDS and Elastic on the following servers
・1st server Suricata IDS & Filebeat : Debian13.7 IP(192.168.11.83)
・2nd server Elasticsearch & kibana : Debian13.5 IP(192.168.11.85)
1st server Suricata Install
SURICATA IDS/IPS is an open source IDS that monitors communications on the network and detects suspicious traffic. Its basic mechanism is signature-based, so it can detect predefined unauthorized communications. Suricata is also characterized by its ability to provide protection as well as detection.
1.Suricata
①Install required packages
# apt -y install wget curl dirmngr apt-transport-https gnupg2 ca-certificates lsb-release debian-archive-keyring unzip
➁Suricata install
# apt update
# apt -y install suricata
Check Version
# suricata -V
This is Suricata version 7.0.10 RELEASE
Enable suricata.service to run on system reboot
# systemctl enable suricata.service
Synchronizing state of suricata.service with SysV service script with /usr/lib/systemd/systemd-sysv-install.
Executing: /usr/lib/systemd/systemd-sysv-install enable suricata
Stop the Suricata service as it needs to be configured first.
# systemctl stop suricata.service
2.Configure Suricata
①Determine interface and IP address where Suricata will inspect network packets
# ip --brief add
lo               UNKNOWN        127.0.0.1/8 ::1/128
ens33            UP             192.168.11.83/24 fe80::20c:29ff:fe8b:5daa/64
➁Edit /etc/suricata/suricata.yaml file
# vi /etc/suricata/suricata.yaml

Line 18 : Change (own network)
HOME_NET: "[192.168.11.0/24]"

Per Line136 : change
community-id: false → community-id: true

Per Line 622 : change
af-packet:
  - interface: eth0
↓
af-packet:
  - interface: ens33 ←Change to your own interface name
➁Add rule set
Suricata has a tool called suricata-update that allows you to retrieve rulesets from external providers. You can download the latest rulesets for your suricata server by running
# suricata-update -o /var/lib/suricata/rules

-------------------------------------------------------------
17/9/2026 -- 12:19:44 - <Info> -- Ignoring file f625293e2432dbf07497d06349de6f0b/rules/emerging-deleted.rules
17/9/2026 -- 12:19:45 - <Info> -- Loaded 68724 rules.
17/9/2026 -- 12:19:46 - <Info> -- Disabled 15 rules.
17/9/2026 -- 12:19:46 - <Info> -- Enabled 0 rules.
17/9/2026 -- 12:19:46 - <Info> -- Modified 0 rules.
17/9/2026 -- 12:19:46 - <Info> -- Dropped 0 rules.
17/9/2026 -- 12:19:46 - <Info> -- Enabled 136 rules for flowbit dependencies.
17/9/2026 -- 12:19:46 - <Info> -- Backing up current rules.
17/9/2026 -- 12:19:46 - <Info> -- Writing rules to /var/lib/suricata/rules/suricata.rules: total: 68724; enabled: 52770; added: 68724; removed 0; modified: 0
17/9/2026 -- 12:19:46 - <Info> -- Writing /var/lib/suricata/rules/classification.config
17/9/2026 -- 12:19:46 - <Info> -- Testing with suricata -T.
17/9/2026 -- 12:20:15 - <Info> -- Done.
It shows that suricata-update has retrieved the free Emerging Threats ET Open Rules and saved them in Suricata's /etc/suricata/rules/suricata.rules file. It also shows the number of rules processed, in this example 68724 were added, of which 52770 were activated.
④Adding Rule Set Providers
List Default Providers
# suricata-update list-sources

Name: abuse.ch/feodotracker
  Vendor: Abuse.ch
  Summary: Abuse.ch Feodo Tracker Botnet C2 IP ruleset
  License: CC0-1.0
Name: abuse.ch/sslbl-blacklist
  Vendor: Abuse.ch
  Summary: Abuse.ch SSL Blacklist
  License: CC0-1.0
  Replaces: sslbl/ssl-fp-blacklist
Name: abuse.ch/sslbl-c2
  Vendor: Abuse.ch
  Summary: Abuse.ch Suricata Botnet C2 IP Ruleset
  License: CC0-1.0
Name: abuse.ch/sslbl-ja3
  Vendor: Abuse.ch
  Summary: Abuse.ch Suricata JA3 Fingerprint Ruleset
  License: CC0-1.0
  Replaces: sslbl/ja3-fingerprints
Name: abuse.ch/urlhaus
  Vendor: abuse.ch
  Summary: Abuse.ch URLhaus Suricata Rules
  License: CC0-1.0
Name: aleksibovellan/nmap
  Vendor: aleksibovellan
  Summary: Suricata IDS/IPS Detection Rules Against NMAP Scans
  License: MIT
Name: et/open
  Vendor: Proofpoint
  Summary: Emerging Threats Open Ruleset
  License: MIT
Name: et/pro
  Vendor: Proofpoint
  Summary: Emerging Threats Pro Ruleset
  License: Commercial
  Replaces: et/open
  Parameters: secret-code
  Subscription: https://www.proofpoint.com/us/threat-insight/et-pro-ruleset
Name: etnetera/aggressive
  Vendor: Etnetera a.s.
  Summary: Etnetera aggressive IP blacklist
  License: MIT
Name: oisf/trafficid
  Vendor: OISF
  Summary: Suricata Traffic ID ruleset
  License: MIT
Name: pawpatrules
  Vendor: pawpatrules
  Summary: PAW Patrules is a collection of rules for IDPS / NSM Suricata engine
  License: CC-BY-SA-4.0
Name: ptrules/open
  Vendor: Positive Technologies
  Summary: Positive Technologies Open Ruleset
  License: Custom
Name: scwx/enhanced
  Vendor: Secureworks
  Summary: Secureworks suricata-enhanced ruleset
  License: Commercial
  Parameters: secret-code
  Subscription: https://www.secureworks.com/contact/ (Please reference CTU Countermeasures)
Name: scwx/malware
  Vendor: Secureworks
  Summary: Secureworks suricata-malware ruleset
  License: Commercial
  Parameters: secret-code
  Subscription: https://www.secureworks.com/contact/ (Please reference CTU Countermeasures)
Name: scwx/security
  Vendor: Secureworks
  Summary: Secureworks suricata-security ruleset
  License: Commercial
  Parameters: secret-code
  Subscription: https://www.secureworks.com/contact/ (Please reference CTU Countermeasures)
Name: stamus/lateral
  Vendor: Stamus Networks
  Summary: Lateral movement rules
  License: GPL-3.0-only
Name: stamus/nrd-14-open
  Vendor: Stamus Networks
  Summary: Newly Registered Domains Open only - 14 day list, complete
  License: Commercial
  Parameters: secret-code
  Subscription: https://www.stamus-networks.com/stamus-labs/subscribe-to-threat-intel-feed
Name: stamus/nrd-30-open
  Vendor: Stamus Networks
  Summary: Newly Registered Domains Open only - 30 day list, complete
  License: Commercial
  Parameters: secret-code
  Subscription: https://www.stamus-networks.com/stamus-labs/subscribe-to-threat-intel-feed
Name: stamus/nrd-entropy-14-open
  Vendor: Stamus Networks
  Summary: Newly Registered Domains Open only - 14 day list, high entropy
  License: Commercial
  Parameters: secret-code
  Subscription: https://www.stamus-networks.com/stamus-labs/subscribe-to-threat-intel-feed
Name: stamus/nrd-entropy-30-open
  Vendor: Stamus Networks
  Summary: Newly Registered Domains Open only - 30 day list, high entropy
  License: Commercial
  Parameters: secret-code
  Subscription: https://www.stamus-networks.com/stamus-labs/subscribe-to-threat-intel-feed
Name: stamus/nrd-phishing-14-open
  Vendor: Stamus Networks
  Summary: Newly Registered Domains Open only - 14 day list, phishing
  License: Commercial
  Parameters: secret-code
  Subscription: https://www.stamus-networks.com/stamus-labs/subscribe-to-threat-intel-feed
Name: stamus/nrd-phishing-30-open
  Vendor: Stamus Networks
  Summary: Newly Registered Domains Open only - 30 day list, phishing
  License: Commercial
  Parameters: secret-code
  Subscription: https://www.stamus-networks.com/stamus-labs/subscribe-to-threat-intel-feed
Name: tgreen/hunting
  Vendor: tgreen
  Summary: Threat hunting rules
  License: GPLv3
f you include the tgreen/hunting ruleset as an example
# suricata-update enable-source tgreen/hunting

17/9/2026 -- 12:21:34 - <Info> -- Using data-directory /var/lib/suricata.
17/9/2026 -- 12:21:34 - <Info> -- Using Suricata configuration /etc/suricata/suricata.yaml
17/9/2026 -- 12:21:34 - <Info> -- Using /etc/suricata/rules for Suricata provided rules.
17/9/2026 -- 12:21:34 - <Info> -- Found Suricata version 7.0.10 at /usr/bin/suricata.
17/9/2026 -- 12:21:34 - <Warning> -- Source index does not exist, will use bundled one.
17/9/2026 -- 12:21:34 - <Warning> -- Please run suricata-update update-sources.
17/9/2026 -- 12:21:34 - <Info> -- Creating directory /var/lib/suricata/update/sources
17/9/2026 -- 12:21:34 - <Info> -- Enabling default source et/open
17/9/2026 -- 12:21:34 - <Info> -- Source tgreen/hunting enabled
Perform update
# suricata-update update-sources
3.Suricata Configuration Testing
①Testing the configuration file
# suricata -T -c /etc/suricata/suricata.yaml -v

Notice: suricata: This is Suricata version 7.0.10 RELEASE running in SYSTEM mode
Info: cpu: CPUs/cores online: 2
Info: suricata: Running suricata under test mode
Info: suricata: Setting engine mode to IDS mode by default
Info: exception-policy: master exception-policy set to: auto
Info: logopenfile: fast output device (regular) initialized: fast.log
Info: logopenfile: eve-log output device (regular) initialized: eve.json
Info: logopenfile: stats output device (regular) initialized: stats.log
Info: detect: 1 rule files processed. 52770 rules successfully loaded, 0 rules failed, 0
Info: threshold-config: Threshold config parsed: 0 rule(s) found
Info: detect: 52775 signatures processed. 1228 are IP-only rules, 4534 are inspecting packet payload, 46778 inspect application layer, 109 are decoder event only
Notice: suricata: Configuration provided was successfully loaded. Exiting.
Suricata service start
# systemctl start suricata
Check Status
# systemctl status suricata

● suricata.service - Suricata IDS/IDP daemon
     Loaded: loaded (/usr/lib/systemd/system/suricata.service; enabled; preset: enabled)
     Active: active (running) since Thu 2026-09-17 12:23:24 JST; 7s ago
 Invocation: d9bf19666dd24f7fac9554e6d8962bb1
       Docs: man:suricata(8)
             man:suricatasc(8)
             https://suricata.io/documentation/
    Process: 21345 ExecStart=/usr/bin/suricata -D --af-packet -c /etc/suricata/suricata.yaml --pidfile /run/suricata.pid (code=exited, status=0/SUCCESS)
   Main PID: 21346 (Suricata-Main)
      Tasks: 1 (limit: 4553)
     Memory: 194.7M (peak: 194.7M)
        CPU: 7.820s
     CGroup: /system.slice/suricata.service
             └─21346 /usr/bin/suricata -D --af-packet -c /etc/suricata/suricata.yaml --pidfile /run/suricata.pid

Sep 17 12:23:24 Lepard systemd[1]: Starting suricata.service - Suricata IDS/IDP daemon...
Sep 17 12:23:24 Lepard suricata[21345]: i: suricata: This is Suricata version 7.0.10 RELEASE running in SYSTEM mode
Sep 17 12:23:24 Lepard systemd[1]: Started suricata.service - Suricata IDS/IDP daemon.
Check log files
# tail -f /var/log/suricata/suricata.log

[21345 - Suricata-Main] 2026-09-17 12:23:24 Notice: suricata: This is Suricata version 7.0.10 RELEASE running in SYSTEM mode
[21345 - Suricata-Main] 2026-09-17 12:23:24 Info: cpu: CPUs/cores online: 2
[21345 - Suricata-Main] 2026-09-17 12:23:24 Info: suricata: Setting engine mode to IDS mode by default
[21345 - Suricata-Main] 2026-09-17 12:23:24 Info: exception-policy: master exception-policy set to: auto
[21346 - Suricata-Main] 2026-09-17 12:23:24 Info: logopenfile: fast output device (regular) initialized: fast.log
[21346 - Suricata-Main] 2026-09-17 12:23:24 Info: logopenfile: eve-log output device (regular) initialized: eve.json
[21346 - Suricata-Main] 2026-09-17 12:23:24 Info: logopenfile: stats output device (regular) initialized: stats.log
[21346 - Suricata-Main] 2026-09-17 12:23:41 Info: detect: 1 rule files processed. 52770 rules successfully loaded, 0 rules failed, 0
[21346 - Suricata-Main] 2026-09-17 12:23:41 Info: threshold-config: Threshold config parsed: 0 rule(s) found
[21346 - Suricata-Main] 2026-09-17 12:23:41 Info: detect: 52775 signatures processed. 1228 are IP-only rules, 4534 are inspecting packet payload, 46778 inspect application layer, 109 are decoder event only
[21346 - Suricata-Main] 2026-09-17 12:23:53 Warning: af-packet: ens33: AF_PACKET tpacket-v3 is recommended for non-inline operation
[21346 - Suricata-Main] 2026-09-17 12:23:53 Info: runmodes: ens33: creating 2 threads
[21346 - Suricata-Main] 2026-09-17 12:23:53 Info: unix-manager: unix socket '/var/run/suricata-command.socket'
[21346 - Suricata-Main] 2026-09-17 12:23:53 Notice: threads: Threads created -> W: 2 FM: 1 FR: 1   Engine started.
4.Testing the Suricata Rule
①Create a file containing customer rules
# vi /var/lib/suricata/rules/local.rules
Please include the following information
alert icmp any any -> any any (msg:"ICMP Ping"; sid:100000; rev:1;)
②Edit the configuration file (define the path for a new rule)
# vi /etc/suricata/suricata.yaml

# Add the following around line 2200
default-rule-path: /var/lib/suricata/rules

rule-files:
  - suricata.rules
  - local.rules
③Testing the Configuration File
# suricata -T -c /etc/suricata/suricata.yaml -v

Info: cpu: CPUs/cores online: 2
Info: suricata: Running suricata under test mode
Info: suricata: Setting engine mode to IDS mode by default
Info: exception-policy: master exception-policy set to: auto
Info: logopenfile: fast output device (regular) initialized: fast.log
Info: logopenfile: eve-log output device (regular) initialized: eve.json
Info: logopenfile: stats output device (regular) initialized: stats.log
Info: detect: 2 rule files processed. 53026 rules successfully loaded, 0 rules failed, 0
Info: threshold-config: Threshold config parsed: 0 rule(s) found
Info: detect: 53031 signatures processed. 1229 are IP-only rules, 4651 are inspecting packet payload, 46916 inspect application layer, 109 are decoder event only
Notice: suricata: Configuration provided was successfully loaded. Exiting.
Suricat service restart
# systemctl restart suricata
④Testing the Application of Custom Rules
Run a ping on another device on the same local network to see if it was logged.
# cat /var/log/suricata/fast.log
09/18/2026-09:00:22.524168  [**] [1:100000:1] ICMP Ping [**] [Classification: (null)] [Priority: 3] {ICMP} 192.168.11.14:8 -> 192.168.11.83:0
09/18/2026-08:34:33.328174  [**] [1:100000:1] ICMP Ping [**] [Classification: (null)] [Priority: 3] {ICMP} 192.168.11.83:0 -> 192.168.11.14:0
To retrieve logs in JSON format, install jq on the system.
# apt -y install jq
Run the following command to ping another device on the same local network
# tail -f /var/log/suricata/eve.json | jq 'select(.event_type=="alert")'
When you run "ping," the following is displayed on the console:
{
  "timestamp": "2026-09-18T09:00:22.524168+0900",
  "flow_id": 1969812594701091,
  "in_iface": "ens33",
  "event_type": "alert",
  "src_ip": "192.168.11.14",
  "dest_ip": "192.168.11.83",
  "proto": "ICMP",
  "icmp_type": 8,
  "icmp_code": 0,
  "pkt_src": "wire/pcap",
  "community_id": "1:K09ijpWpwrp7sSrxOGACqhHkilo=",
  "alert": {
    "action": "allowed",
    "gid": 1,
    "signature_id": 100000,
    "rev": 1,
    "signature": "ICMP Ping",
    "category": "",
    "severity": 3
  },
5.Reset SURICATA and restart it in IPS mode.
SURICATA operates in IDS mode by default and does not actively block network traffic. To switch to IPS mode, you must modify SURICATA's default settings.
5.1 Enabling nfqueue mode
# vi /usr/lib/systemd/system/suricata.service

Make the following changes:
[Service]
#ExecStart=/usr/bin/suricata -D --af-packet -c /etc/suricata/suricata.yaml - -pidfile /run/suricata.pid
ExecStart=/usr/bin/suricata -D -q 0 -c /etc/suricata/suricata.yaml --pidfile /run/suricata.pid
Reload the configuration and restart Suricata.
# systemctl daemon-reload
# systemctl restart suricata.service
5.2 Configuring UFW to Send Traffic to Suricata
# vi /etc/ufw/before.rules

Add the following to line 19
# Don't delete these required lines, otherwise there will be errors
*filter
:ufw-before-input - [0:0]
:ufw-before-output - [0:0]
:ufw-before-forward - [0:0]
:ufw-not-local - [0:0]
# End required lines

## Start Suricata NFQUEUE rules
-I INPUT 1 -p tcp --dport 2244 -j NFQUEUE --queue-bypass
-I OUTPUT 1 -p tcp --sport 2244 -j NFQUEUE --queue-bypass
-I FORWARD -j NFQUEUE
-I INPUT 2 -j NFQUEUE
-I OUTPUT 2 -j NFQUEUE
## End Suricata NFQUEUE rules
For IPv6, edit the following file in the same way
# vi /etc/ufw/before6.rules
Restart the UFW service
# systemctl restart ufw.service
Elastic stack 9.x installation
Install & configure Elastic Stack to visualize & search SURICATA logs
This section is basically done on a second Debian13.5 server
①Install Elastic stack 9.x repository signing key
# apt update
# apt -y install gnupg2
# wget -qO - https://artifacts.elastic.co/GPG-KEY-elasticsearch | \
gpg --dearmor -o /etc/apt/trusted.gpg.d/elastic.gpg
➁Install Elastic Stack 9.x repository
# echo "deb https://artifacts.elastic.co/packages/9.x/apt stable main" > /etc/apt/sources.list.d/elastic-9.x.list
update
# apt update
➂Installing Elasticsearch 9.x
# apt install elasticsearch -y
During installation, security features are enabled by default;
--------------------------- Security autoconfiguration information ------------------------------

Authentication and authorization are enabled.
TLS for the transport and HTTP layers is enabled and configured.

The generated password for the elastic built-in superuser is : PLk-8MIiPy1VmyoSDLfh

If this node should join an existing cluster, you can reconfigure this with
'/usr/share/elasticsearch/bin/elasticsearch-reconfigure-node --enrollment-token <token-here>'
after creating an enrollment token on your existing cluster.

You can complete the following actions at any time:

Reset the password of the elastic built-in superuser with
'/usr/share/elasticsearch/bin/elasticsearch-reset-password -u elastic'.

Generate an enrollment token for Kibana instances with
 '/usr/share/elasticsearch/bin/elasticsearch-create-enrollment-token -s kibana'.

Generate an enrollment token for Elasticsearch nodes with
'/usr/share/elasticsearch/bin/elasticsearch-create-enrollment-token -s node'.

-------------------------------------------------------------------------------------------------
Certifications and authorizations are in effect.
TLS at the transport and HTTP layers is enabled and configured.
An Elastic super user account (elastic) and its password will be created.
④Configuring Elasticsearch 9.x
Since this is a basic single-node cluster, we will use the default settings.
Check the Elasticsearch configuration file /etc/elasticsearch/elasticsearch.yml and you will see that the security settings are enabled
# cat /etc/elasticsearch/elasticsearch.yml

#----------------------- BEGIN SECURITY AUTO CONFIGURATION -----------------------
#
# The following settings, TLS certificates, and keys have been automatically
# generated to configure Elasticsearch security features on 17-09-2026 06:55:53
#
# --------------------------------------------------------------------------------

# Enable security features
xpack.security.enabled: true

xpack.security.enrollment.enabled: true

# Enable encryption for HTTP API client connections, such as Kibana, Logstash, and Agents
xpack.security.http.ssl:
  enabled: true
  keystore.path: certs/http.p12

# Enable encryption and mutual authentication between cluster nodes
xpack.security.transport.ssl:
  enabled: true
  verification_mode: certificate
  keystore.path: certs/transport.p12
  truststore.path: certs/transport.p12
# Create a new cluster with the current node only
# Additional nodes can still join the cluster later
cluster.initial_master_nodes: ["Lion"]

# Allow HTTP API connections from anywhere
# Connections are encrypted and require user authentication
http.host: 0.0.0.0

# Allow other nodes to join the cluster from anywhere
# Connections are encrypted and mutually authenticated
#transport.host: 0.0.0.0

#----------------------- END SECURITY AUTO CONFIGURATION -------------------------
⑤Start Elasticsearch
Start Elasticsearch and allow it to run at system startup
# systemctl daemon-reload
# systemctl enable --now elasticsearch
# systemctl start elasticsearch
Check Status
# systemctl status elasticsearch

● elasticsearch.service - Elasticsearch
     Loaded: loaded (/usr/lib/systemd/system/elasticsearch.service; enabled; preset: enabled)
     Active: active (running) since Thu 2026-09-17 15:59:14 JST; 12s ago
 Invocation: 42f83b21e59f44b69f3bfa965766a021
       Docs: https://www.elastic.co
   Main PID: 1922 (server-launcher)
      Tasks: 100 (limit: 3421)
     Memory: 1.9G (peak: 1.9G)
        CPU: 49.755s
     CGroup: /system.slice/elasticsearch.service
             tq1922 /usr/share/elasticsearch/lib/tools/server-launcher/server-launcher -p /run/elasticsearch/elasticsearch.pid --quiet
             tq1972 /usr/share/elasticsearch/jdk/bin/java -Des.networkaddress.cache.ttl=60 -Des.networkaddress.cache.negative.ttl=10 -XX:+AlwaysPreTouch -Xss1m -Djava.awt.headless=true -Dfile.e>
             mq1995 /usr/share/elasticsearch/modules/x-pack-ml/platform/linux-x86_64/bin/controller

Sep 17 15:58:37 Lion systemd[1]: Starting elasticsearch.service - Elasticsearch...
Sep 17 15:58:40 Lion systemd-entrypoint[1922]: WARNING: Unknown module: org.apache.arrow.memory.core specified to --add-opens
Sep 17 15:59:06 Lion systemd-entrypoint[1922]: WARNING: A terminally deprecated method in sun.misc.Unsafe has been called
Sep 17 15:59:06 Lion systemd-entrypoint[1922]: WARNING: sun.misc.Unsafe::arrayBaseOffset has been called by com.google.protobuf.UnsafeUtil$MemoryAccessor (file:/usr/share/elasticsearch/modules/>
Sep 17 15:59:06 Lion systemd-entrypoint[1922]: WARNING: Please consider reporting this to the maintainers of class com.google.protobuf.UnsafeUtil$MemoryAccessor
Sep 17 15:59:06 Lion systemd-entrypoint[1922]: WARNING: sun.misc.Unsafe::arrayBaseOffset will be removed in a future release
Sep 17 15:59:14 Lion systemd[1]: Started elasticsearch.service - Elasticsearch.
You can also check the status of the ES using the curl command; replace IP as appropriate
# curl https://192.168.11.85:9200 --cacert /etc/elasticsearch/certs/http_ca.crt -u elastic
When prompted, enter the Elasticsearch password generated during the Elasticsearch installation
The output will look like this
Enter host password for user 'elastic':  ←Password
{
  "name" : "Lion",
  "cluster_name" : "elasticsearch",
  "cluster_uuid" : "56bp6AXRRpC0AqJGw6Ov-g",
  "version" : {
    "number" : "9.5.4",
    "build_flavor" : "default",
    "build_type" : "deb",
    "build_hash" : "9170df19cae1adb107b7b489b4d82dec66d7a337",
    "build_date" : "2026-09-09T22:42:53.976833287Z",
    "build_snapshot" : false,
    "lucene_version" : "10.5.1",
    "minimum_wire_compatibility_version" : "8.19.0",
    "minimum_index_compatibility_version" : "8.0.0"
  },
  "tagline" : "You Know, for Search"
}
Also, make sure that both the HTTP and transport ports are open;
# ss -altnp | grep -E "9200|9300"

LISTEN 0      4096                    *:9200            *:*    users:(("java",pid=19343,fd=838))
LISTEN 0      4096   [::ffff:127.0.0.1]:9300            *:*    users:(("java",pid=19343,fd=836))
LISTEN 0      4096                [::1]:9300         [::]:*    users:(("java",pid=19343,fd=835))
⑥Reset Elasticsearch Password
The auto-generated Elastic user password is too complex, reset it using the command /usr/share/elasticsearch/bin/elasticsearch-reset-password
To reset the password, run the command
# /usr/share/elasticsearch/bin/elasticsearch-reset-password -u elastic -i

This tool will reset the password of the [elastic] user.
You will be prompted to enter the password.
Please confirm that you would like to continue [y/N]y


Enter password for [elastic]:
Re-enter password for [elastic]:
Password for the [elastic] user successfully reset.
⑦Elasticsearch Logs
Elasticsearch writes logs to the /var/log/elasticsearch path; the log you need to check if there is a problem with your Elasticsearch instance is /var/log/elasticsearch/CLUSTER_NAME.log The logs you need to check if there is a problem with your Elasticsearch instance are
CLUSTER_NAME is the value of the cluster.name option in the elasticsearch.yaml file. If this value is not changed, the default is elasticsearch and the log file is /var/log/elasticsearch/elasticsearch.log.
# tail -f /var/log/elasticsearch/elasticsearch.log

[2026-09-17T15:59:19,654][INFO ][o.e.x.i.IndexLifecycleTransition] [Lion] moving index [.ds-.logs-elasticsearch.deprecation-default-2026.09.17-000001] from [{"phase":"hot","action":"unfollow","name":"branch-check-unfollow-prerequisites"}] to [{"phase":"hot","action":"rollover","name":"check-rollover-ready"}] in policy [.deprecation-indexing-ilm-policy]
[2026-09-17T15:59:19,681][INFO ][o.e.c.m.MetadataMappingService] [Lion] [.ds-.logs-elasticsearch.deprecation-default-2026.09.17-000001/qVV3sQcqTT6syGQg-lzv7w] update_mapping [_doc]
[2026-09-17T15:59:24,591][INFO ][o.e.c.m.MetadataCreateIndexService] [Lion] creating index [.ds-ilm-history-7-2026.09.17-000001] in project [default], cause [initialize_data_stream], templates [provided in request], shards [1]/[1]
[2026-09-17T15:59:24,593][INFO ][o.e.c.m.MetadataCreateDataStreamService] [Lion] adding data stream [ilm-history-7] with write index [.ds-ilm-history-7-2026.09.17-000001], backing indices [], and aliases []
[2026-09-17T15:59:24,594][INFO ][o.e.c.r.a.AllocationService] [Lion] in project [default] updating number_of_replicas to [0] for indices [.ds-ilm-history-7-2026.09.17-000001]
[2026-09-17T15:59:24,682][INFO ][o.e.c.r.a.AllocationService] [Lion] current.health="GREEN" message="Cluster health status changed from [YELLOW] to [GREEN] (reason: [shards started [[.ds-ilm-history-7-2026.09.17-000001][0]]])." previous.health="YELLOW" reason="shards started [[.ds-ilm-history-7-2026.09.17-000001][0]]"
[2026-09-17T16:01:46,283][INFO ][o.e.x.s.a.f.FileUserPasswdStore] [Lion] users file [/etc/elasticsearch/users] changed. updating users...
[2026-09-17T16:01:46,288][INFO ][o.e.x.s.a.f.FileUserRolesStore] [Lion] users roles file [/etc/elasticsearch/users_roles] changed. updating users roles...
[2026-09-17T16:02:06,299][INFO ][o.e.x.s.a.f.FileUserPasswdStore] [Lion] users file [/etc/elasticsearch/users] changed. updating users...
[2026-09-17T16:02:06,302][INFO ][o.e.x.s.a.f.FileUserRolesStore] [Lion] users roles file [/etc/elasticsearch/users_roles] changed. updating users roles...
Kibana 9.x installation
We will also perform this section on the second Debian 13.5 server.
①Install
# apt -y install kibana

Installing:
  kibana

Summary:
  Upgrading: 0, Installing: 1, Removing: 0, Not Upgrading: 0
  Download size: 482 MB
  Space needed: 1,579 MB / 28.1 GB available

Get:1 https://artifacts.elastic.co/packages/9.x/apt stable/main amd64 kibana amd64 9.5.4 [482 MB]
Fetched 482 MB in 14s (34.2 MB/s)
Selecting previously unselected package kibana.
(Reading database ... 37543 files and directories currently installed.)
Preparing to unpack .../kibana_9.5.4_amd64.deb ...
Unpacking kibana (9.5.4) ...
Setting up kibana (9.5.4) ...
Creating kibana group... OK
Creating kibana user... OK
Created Kibana keystore in /etc/kibana/kibana.keystore
➁Configure Kibana 9
Kibana is configured by default to run on localhost:5601. To allow external access, edit the configuration file and replace the server.host value with the interface IP.
# vi /etc/kibana/kibana.yml

Line 6: Uncomment
server.port: 5601
Add around line 12
# To allow connections from remote users, set this parameter to a non-loopback address.
#server.host: "localhost"
server.host: "192.168.11.85"
➂Generate Kibana-Elasticsearch Enrollment Token
To configure your Kibana instance to communicate with an existing Elasticsearch cluster with security features enabled, you need an Enrollment Token.
# /usr/share/elasticsearch/bin/elasticsearch-create-enrollment-token -s kibana

eyJ2ZXIiOiI4LjE0LjAiLCJhZHIiOlsiMTkyLjE2OC4xMS44NTo5MjAwIl0sImZnciI6ImNjMGFiYmZkM2NjZDIwMjI1OWE5YWVkNGJiZDg3MTliYjAwMjc3ZTU1YzJjYTQxNDliYTg0ZTcxNjA1YjJmYjUiLCJrZXkiOiI3bzk4cnFBQmFqOXRtcXBjQVpfbDpUZWY5andIZG9qUl9uUmgyN0dqQ05nIn0=
④Generate Kibana encryption keys
Kibana uses encryption keys in several areas, from encrypting data for Kibana-related indexes to storing session information. The required keys are as follows
xpack.encryptedSavedObjects.encryptionKey:Used to encrypt stored objects such as dashboards and visualizationsxpack.reporting.encryptionKey: Used to encrypt saved reportsxpack.security.encryptionKey: Used to encrypt session information
These can be generated using the command below
# /usr/share/kibana/bin/kibana-encryption-keys generate

Settings:
xpack.encryptedSavedObjects.encryptionKey: 910c507e0001c103cbc5ef7a90ca20e9c80bb94fad71607ac4730d713e605edd
xpack.reporting.encryptionKey: 8124bef4fa7733abb4a0e1bb889d72c2d667536d6d066866a98985c38d4d9834
xpack.security.encryptionKey: 9599dc2ef402656d062bbdd29285bb5f2a8888bc86aa940b2ec83fdf926b0d70
Insert these lines into Kibana config file, kibana.yml
# echo -e "xpack.encryptedSavedObjects.encryptionKey: 910c507e0001c103cbc5ef7a90ca20e9c80bb94fad71607ac4730d713e605edd
xpack.reporting.encryptionKey: 8124bef4fa7733abb4a0e1bb889d72c2d667536d6d066866a98985c38d4d9834
xpack.security.encryptionKey: 9599dc2ef402656d062bbdd29285bb5f2a8888bc86aa940b2ec83fdf926b0d70" >> /etc/kibana/kibana.yml
⑤Running Kibana
Start Kibana 9 and allow it to run at system startup.
# systemctl enable --now kibana
# systemctl start kibana
Check Status
# systemctl status kibana

● kibana.service - Kibana
     Loaded: loaded (/usr/lib/systemd/system/kibana.service; enabled; preset: enabled)
     Active: active (running) since Thu 2026-09-17 17:31:01 JST; 48s ago
 Invocation: e6c92198e4a844c389700ce9f16d2b43
       Docs: https://www.elastic.co
   Main PID: 19184 (MainThread)
      Tasks: 11 (limit: 3957)
     Memory: 888M (peak: 888.4M)
        CPU: 16.827s
     CGroup: /system.slice/kibana.service
             mq19184 /usr/share/kibana/bin/../node/default/bin/node /usr/share/kibana/bin/../node_modules/@kbn/cli/kibana/dist

Sep 17 17:31:09 Lion kibana[19184]: Native global console methods have been overridden in production environment.
Sep 17 17:31:14 Lion kibana[19184]: [2026-09-17T17:31:14.051+09:00][INFO ][root] Kibana is starting
Sep 17 17:31:14 Lion kibana[19184]: [2026-09-17T17:31:14.273+09:00][INFO ][node] Kibana process configured with roles: [background_tasks, ui]
Sep 17 17:31:30 Lion kibana[19184]: [2026-09-17T17:31:30.903+09:00][INFO ][plugins-service] The following plugins are disabled: "cloudChat,cloudExp>
Sep 17 17:31:30 Lion kibana[19184]: [2026-09-17T17:31:30.991+09:00][INFO ][http.server.Preboot] http server running at http://192.168.11.85:5601
Sep 17 17:31:31 Lion kibana[19184]: [2026-09-17T17:31:31.356+09:00][INFO ][plugins-system.preboot] Setting up [1] plugins: [interactiveSetup]
Sep 17 17:31:31 Lion kibana[19184]: [2026-09-17T17:31:31.405+09:00][INFO ][preboot] "interactiveSetup" plugin is holding setup: Validating Elastics>
Sep 17 17:31:31 Lion kibana[19184]: [2026-09-17T17:31:31.453+09:00][INFO ][root] Holding setup until preboot stage is completed.
Sep 17 17:31:39 Lion kibana[19184]: i Kibana has not been configured.
Sep 17 17:31:39 Lion kibana[19184]: Go to http://192.168.11.85:5601/?code=062853 to get started.
The following appears at the end of the output
Go to http://192.168.11.85:5601/?code=062853
Copy the provided Kibana URL (including code) and use it in your browser to access Kibana and complete the setup.
Similarly, Kibana logs are available in /var/log/kibana/kibana.log and /var/log/syslog.
⑥Accessing the Kibana9 Dashboard
If UFW is running, open Kibana port
# ufw allow 5601/tcp
Rule added
# ufw reload
Firewall reloaded
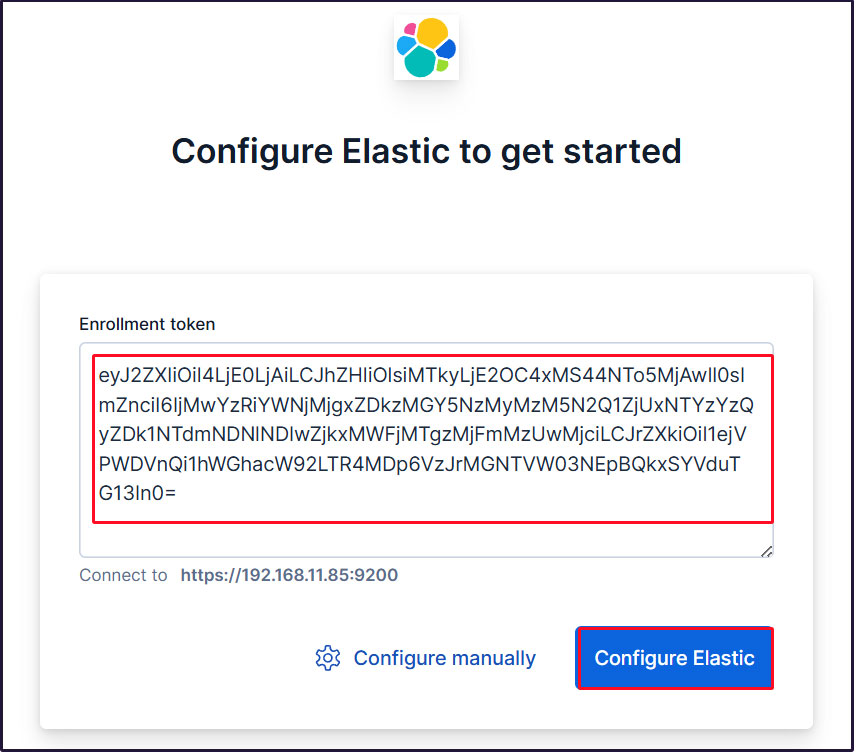
When you go to http://192.168.11.85:5601/?code=062853, the welcome page will prompt you to configure Elastic.
First, enter the generated registration token.
Copy the Kibana token generated using the command /usr/share/elasticsearch/bin/elasticsearch-create-enrollment-token -s kibana, and paste it into the box
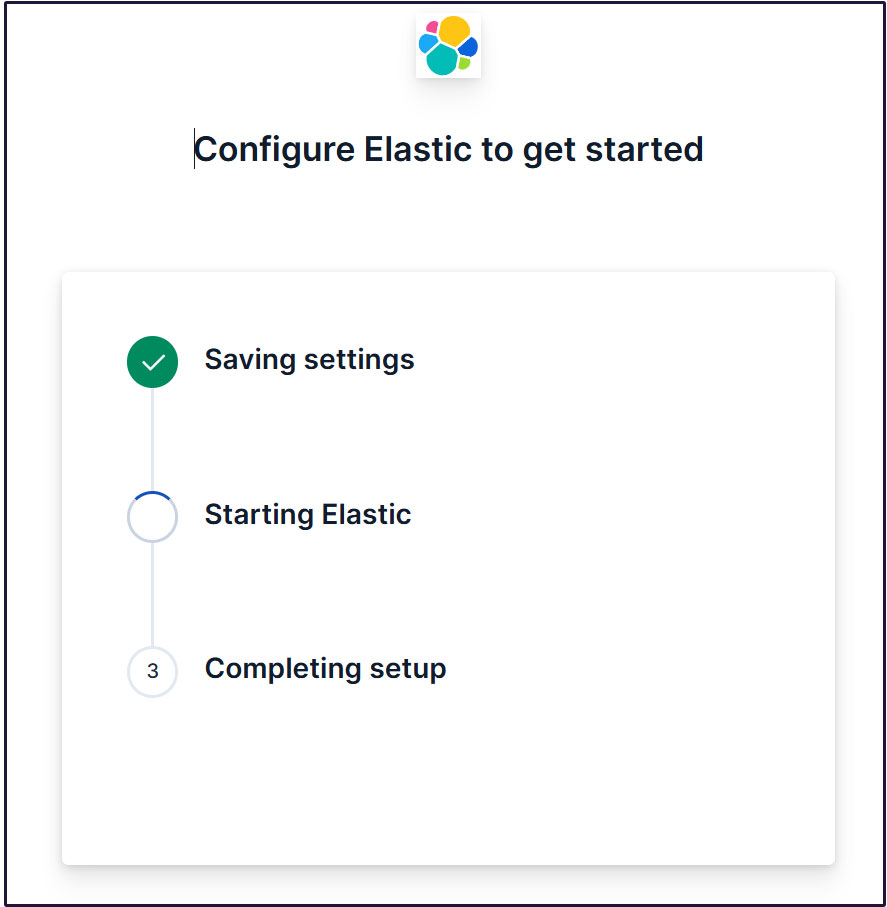
Go to the login page. Log in using the generated Elastic user credentials.
Username : elastic
Password : Easy-to-understand regenerated passwords
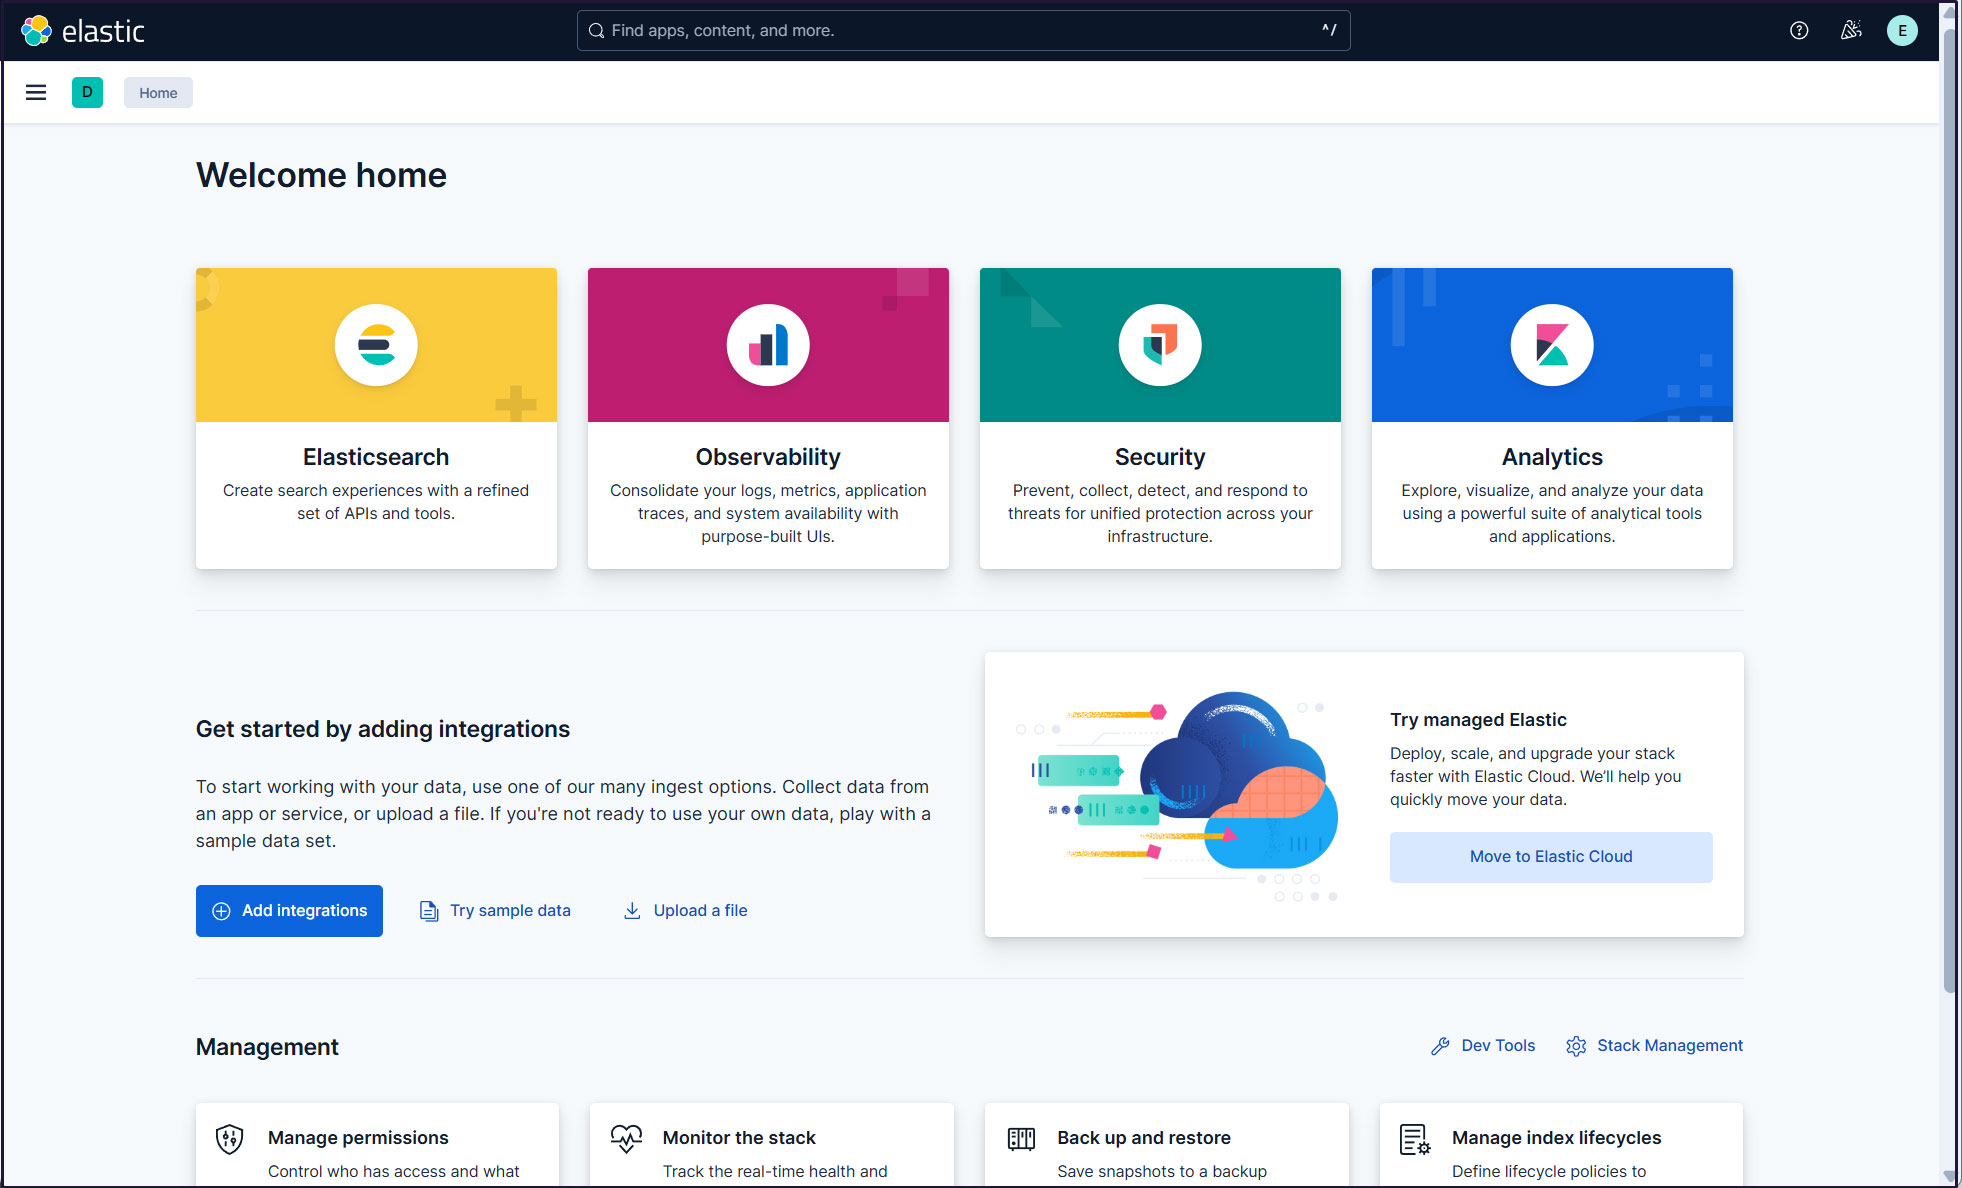
On the welcome page, click "Explore on my own" to proceed to the Kibana 9.x dashboard.。
Installing Filebeat 9
To collect logs and monitor the first-generation server running Debian 13.7, you need to install Filebeat.
This procedure will be performed on the first server, running Debian 13.7 with the IP address 192.168.11.83.
①Install Elastic Repos
To install Filebeat 9, install the Elastic 9.x repository
# wget -qO - https://artifacts.elastic.co/GPG-KEY-elasticsearch | \
gpg --dearmor > /etc/apt/trusted.gpg.d/elk.gpg

# echo "deb https://artifacts.elastic.co/packages/9.x/apt stable main" \
> /etc/apt/sources.list.d/elastic-9.list
update
# apt update
Install Filebeat 9
# apt -y install filebeat
➁Configuring Filebeat Logging
The default filebeat configuration file is /etc/filebeat/filebeat.yml
To make Filebeat write logs to its own log file, enter the following settings in the configuration file
# cat >> /etc/filebeat/filebeat.yml << 'EOL'
logging.level: info
logging.to_files: true
logging.files:
  path: /var/log/filebeat
  name: filebeat
  keepfiles: 7
  permissions: 0640
EOL
➂Connecting Filebeat to the data processing system
Configure Filebeat to connect to a data processing system. In this case, it is Elasticsearch.
To send logs directly to Elasticsearch, edit the Filebeat configuration file and update the Output Settings section.
Connecting to Elasticsearch 9 requires SSL and authentication.
Verify that you can connect to Elasticsearch on port 9200/tcp (make sure to open port 9200 on the second server beforehand)
# telnet 192.168.11.85 9200

Trying 192.168.11.85...
Connected to 192.168.11.85.
Escape character is '^]'.
④Elasticsearch CA certificate creation
Download the Elasticsearch CA certificate and save it in a directory of your choice (this time as /etc/filebeat/elastic-ca.crt)
# openssl s_client -connect 192.168.11.85:9200 \
-showcerts </dev/null 2>/dev/null | \
openssl x509 -outform PEM > /etc/filebeat/elastic-ca.crt
Get the credentials that Filebeat uses to authenticate to Elasticsearch. In this case, we will use the default superadmin and Elastic user credentials.
# vi /etc/filebeat/filebeat.yml

Around line 138, modify the Kibana section as follows:
#host: "localhost:5601"
host: "192.168.11.85:5601"

Change the Elasticsearch Output section around line 164 as follows:
output.elasticsearch:
  # Array of hosts to connect to.
  #hosts: ["localhost:9200"]
  hosts: ["192.168.11.85:9200"]

Uncomment around line 171 and specify the location of the Elasticsearch CA certificate
  # Protocol - either `http` (default) or `https`.
  protocol: "https"
  ssl.certificate_authorities: ["/etc/filebeat/elastic-ca.crt"]

Uncomment the lines around lines 175 and 176 and enter the password
  # Authentication credentials - either API key or username/password.
  #api_key: "id:api_key"
  username: "elastic"
  password: "Password"   ←The Elastic password created on the second server
⑤Configuration File Test
# filebeat test config
Config OK
⑥Test Filebeat output connections
# filebeat test output

elasticsearch: https://192.168.11.85:9200...
  parse url... OK
  connection...
    parse host... OK
    dns lookup... OK
    addresses: 192.168.11.85
    dial up... OK
  TLS...
    security: server's certificate chain verification is enabled
    handshake... OK
    TLS version: TLSv1.3
    dial up... OK
  talk to server... OK
  version: 9.5.4
⑦Enable the Suricata module for Filebeat
When you enable the Suricata module, /etc/filebeat/modules.d/suricata.yml.disabled becomes /etc/filebeat/modules.d/suricata.yml, but the contents remain unchanged, so modify it as follows:
# filebeat modules enable suricata

# vi /etc/filebeat/modules.d/suricata.yml
Change lines 7–8 as follows
- module: suricata
  # All logs
  eve:
    enabled: true
    var.paths: ["/var/log/suricata/eve.json"]
⑧Set up the initial environment
Load the SIEM dashboard and pipeline into Elasticsearch
filebeat setup command
# filebeat setup -e

{"log.level":"info","@timestamp":"2026-09-17T18:36:54.024+0900","log.logger":"modules","log.origin":{"function":"github.com/elastic/beats/v7/filebeat/fileset.LoadPipeline","file.name":"fileset/pipelines.go","file.line":134},"message":"Elasticsearch pipeline loaded.","service.name":"filebeat","pipeline":"filebeat-9.5.4-suricata-eve-pipeline","ecs.version":"1.6.0"}
{"log.level":"info","@timestamp":"2026-09-17T18:36:54.093+0900","log.logger":"modules","log.origin":{"function":"github.com/elastic/beats/v7/filebeat/fileset.LoadPipeline","file.name":"fileset/pipelines.go","file.line":134},"message":"Elasticsearch pipeline loaded.","service.name":"filebeat","pipeline":"filebeat-9.5.4-suricata-eve-dns","ecs.version":"1.6.0"}
{"log.level":"info","@timestamp":"2026-09-17T18:36:54.142+0900","log.logger":"modules","log.origin":{"function":"github.com/elastic/beats/v7/filebeat/fileset.LoadPipeline","file.name":"fileset/pipelines.go","file.line":134},"message":"Elasticsearch pipeline loaded.","service.name":"filebeat","pipeline":"filebeat-9.5.4-suricata-eve-dns-answer-v1","ecs.version":"1.6.0"}
{"log.level":"info","@timestamp":"2026-09-17T18:36:54.209+0900","log.logger":"modules","log.origin":{"function":"github.com/elastic/beats/v7/filebeat/fileset.LoadPipeline","file.name":"fileset/pipelines.go","file.line":134},"message":"Elasticsearch pipeline loaded.","service.name":"filebeat","pipeline":"filebeat-9.5.4-suricata-eve-dns-answer-v2","ecs.version":"1.6.0"}
{"log.level":"info","@timestamp":"2026-09-17T18:36:54.277+0900","log.logger":"modules","log.origin":{"function":"github.com/elastic/beats/v7/filebeat/fileset.LoadPipeline","file.name":"fileset/pipelines.go","file.line":134},"message":"Elasticsearch pipeline loaded.","service.name":"filebeat","pipeline":"filebeat-9.5.4-suricata-eve-tls","ecs.version":"1.6.0"}
{"log.level":"info","@timestamp":"2026-09-17T18:36:54.324+0900","log.logger":"modules","log.origin":{"function":"github.com/elastic/beats/v7/filebeat/fileset.LoadPipeline","file.name":"fileset/pipelines.go","file.line":134},"message":"Elasticsearch pipeline loaded.","service.name":"filebeat","pipeline":"filebeat-9.5.4-suricata-eve-http","ecs.version":"1.6.0"}
⑨Filebeat service launched
# systemctl start filebeat.service
# systemctl enable filebeat.service
⑩Check with Kibana
Log back into Kibana at accsess http://192.168.11.85:5601
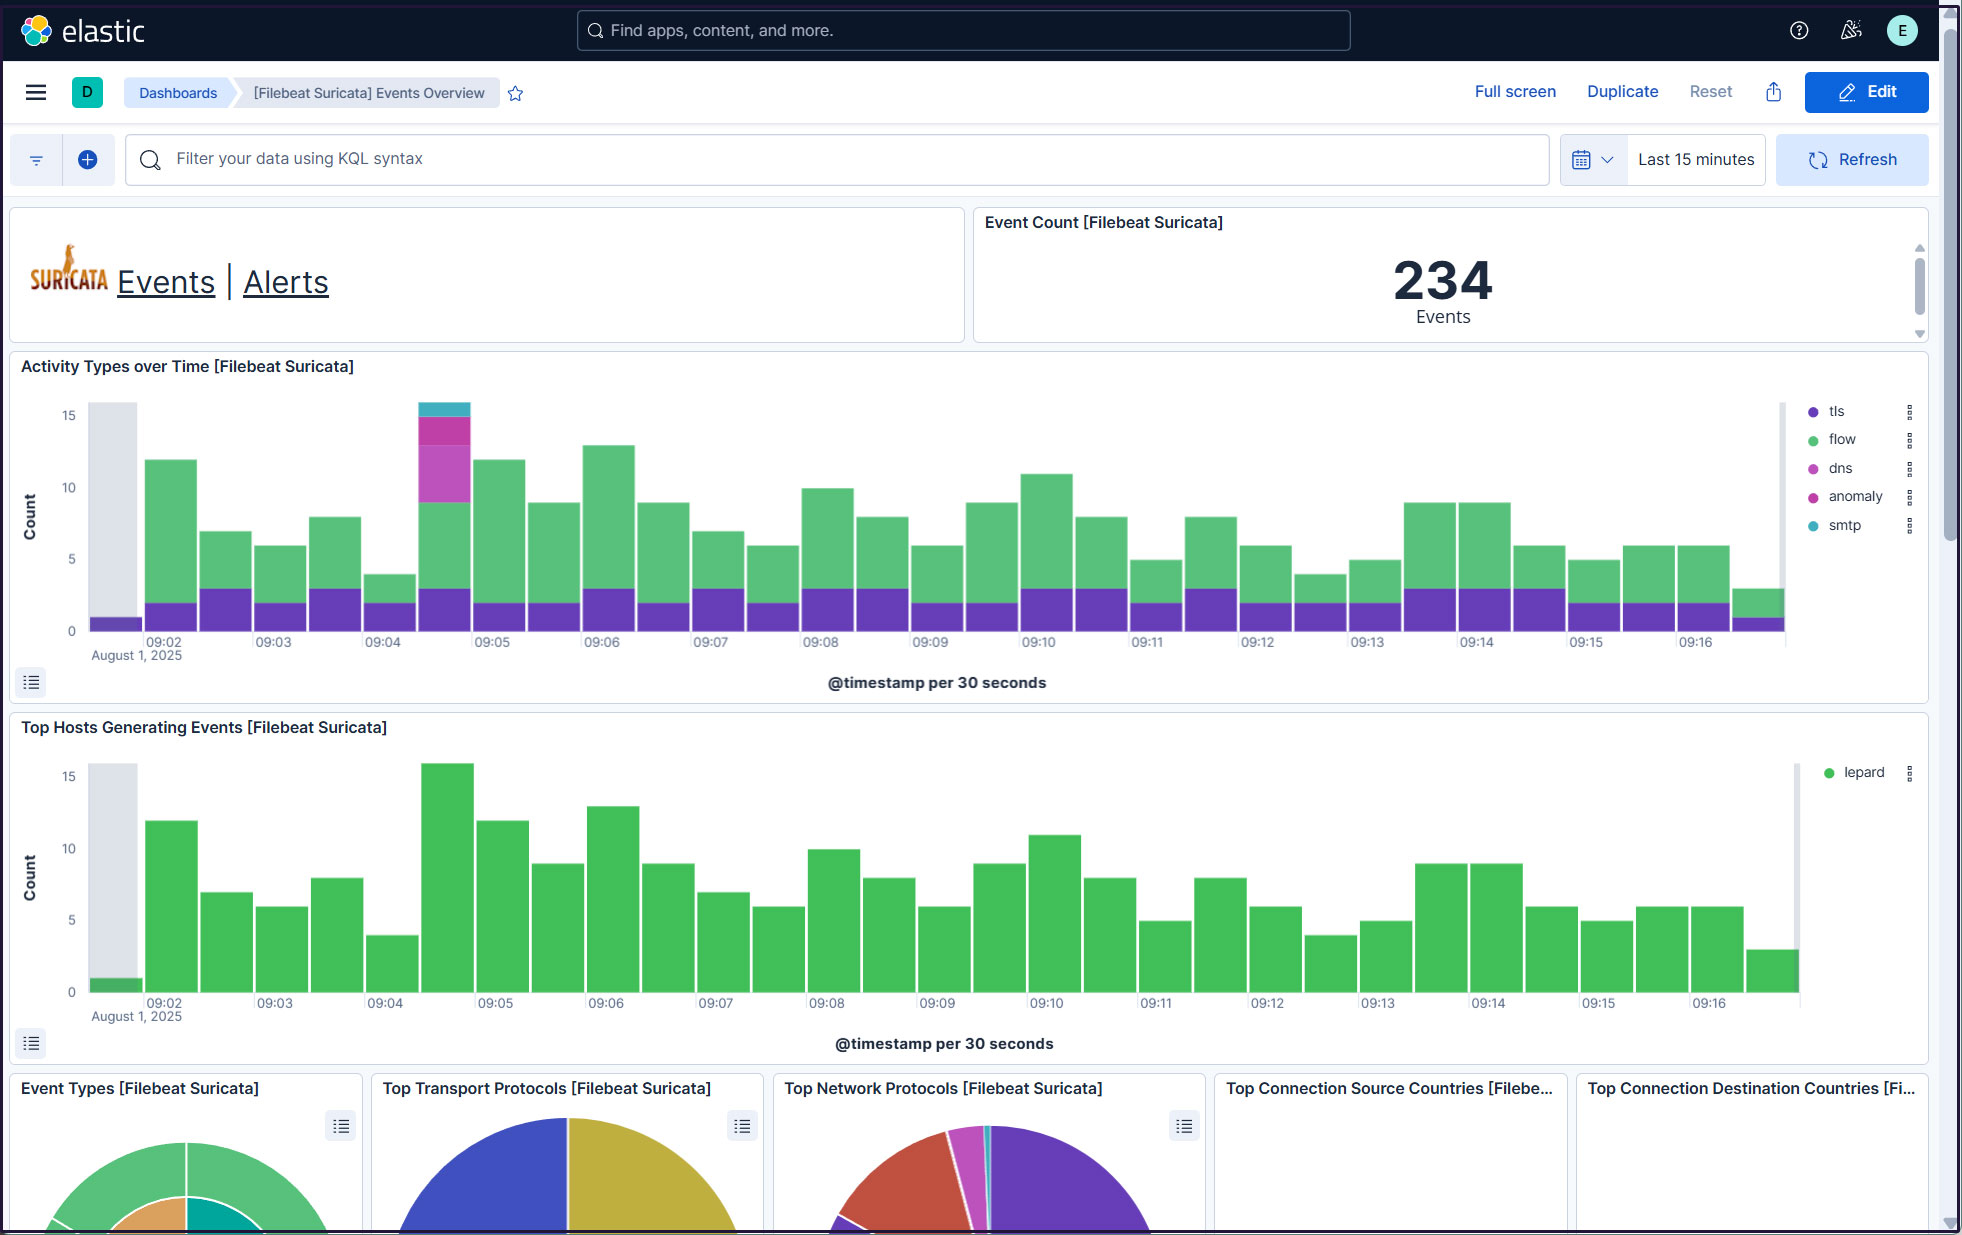
Type "Suricata Events Overview" in the top search field and click [Filebeat Suricata]Events Overview
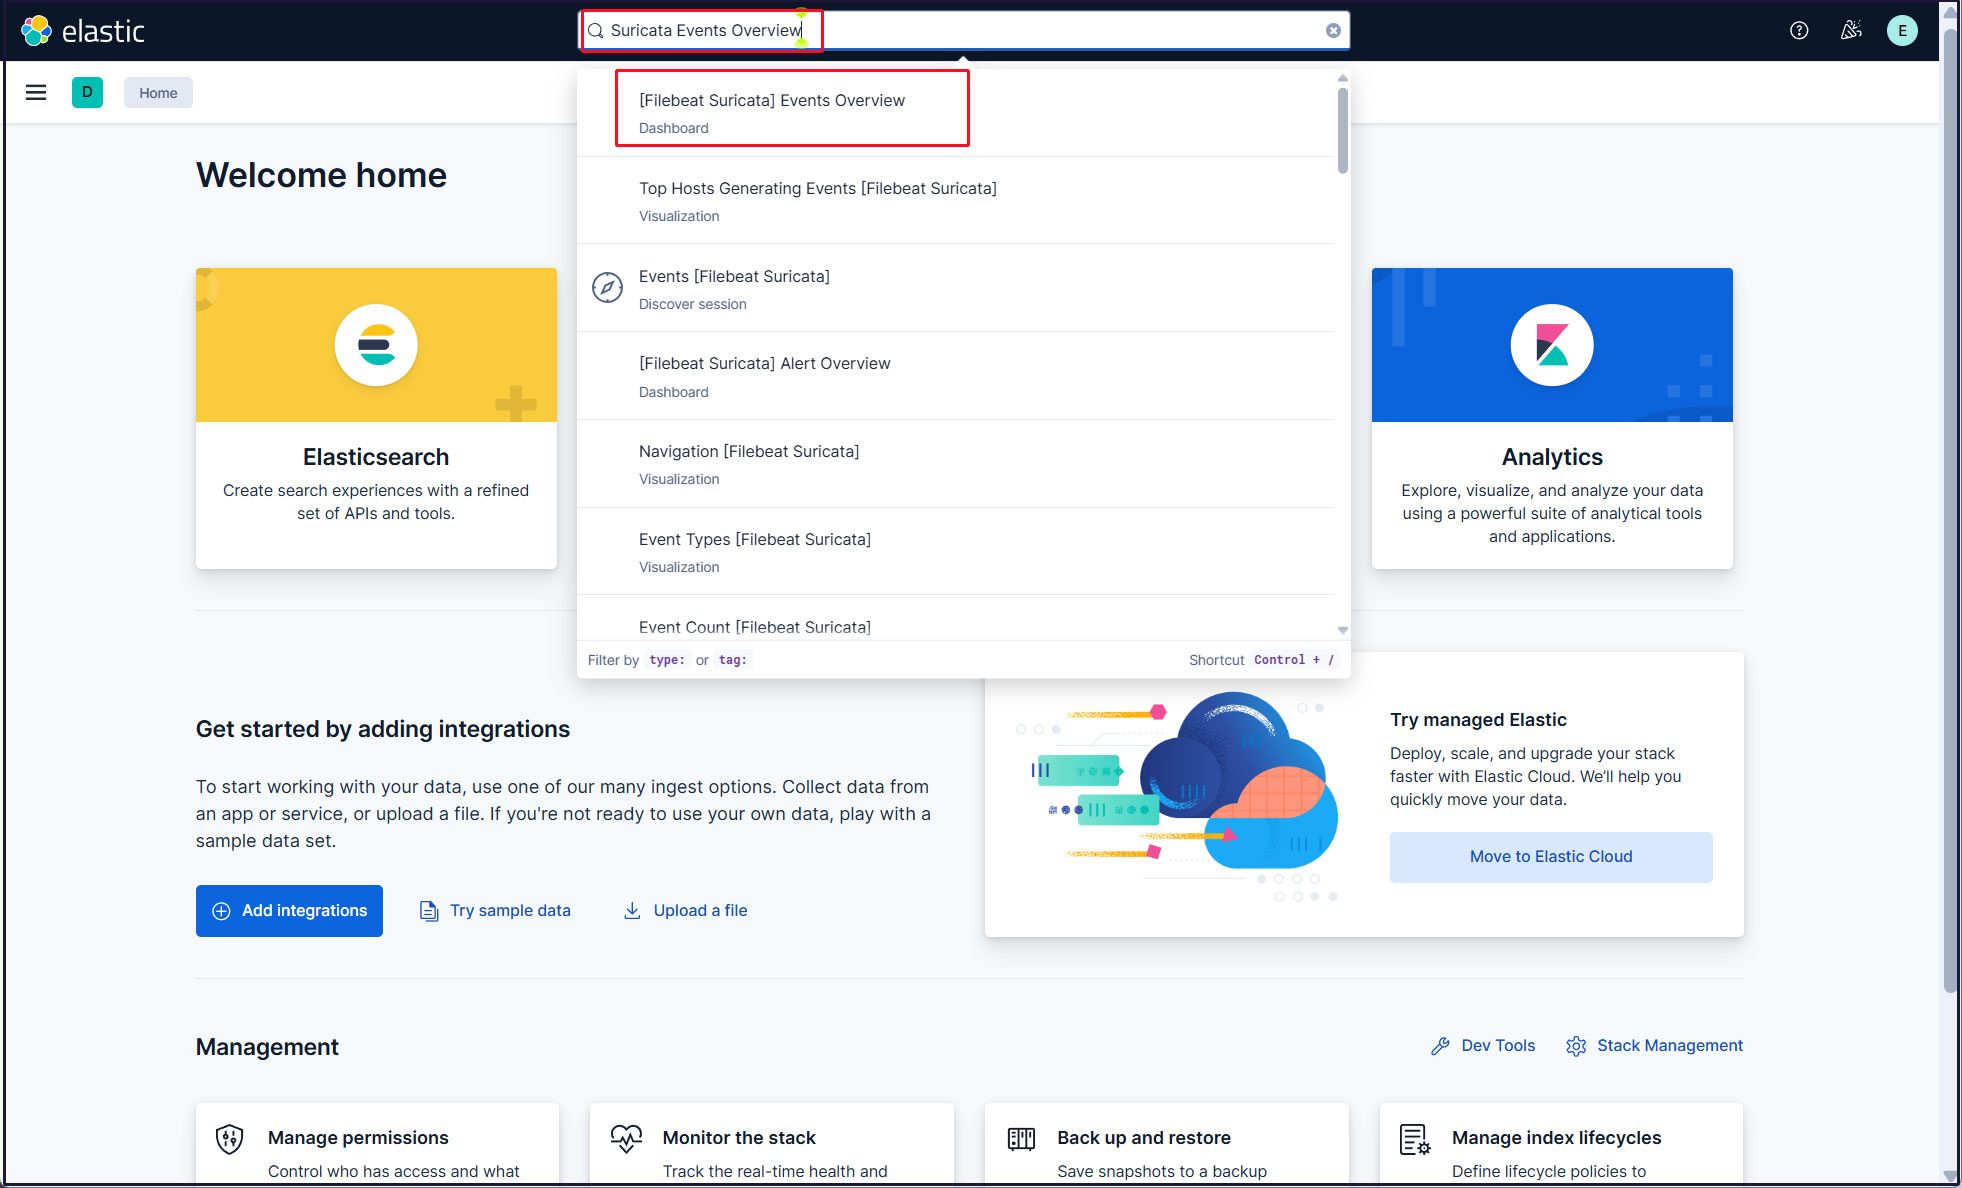
All Suricata events in the last 15 minutes are displayed
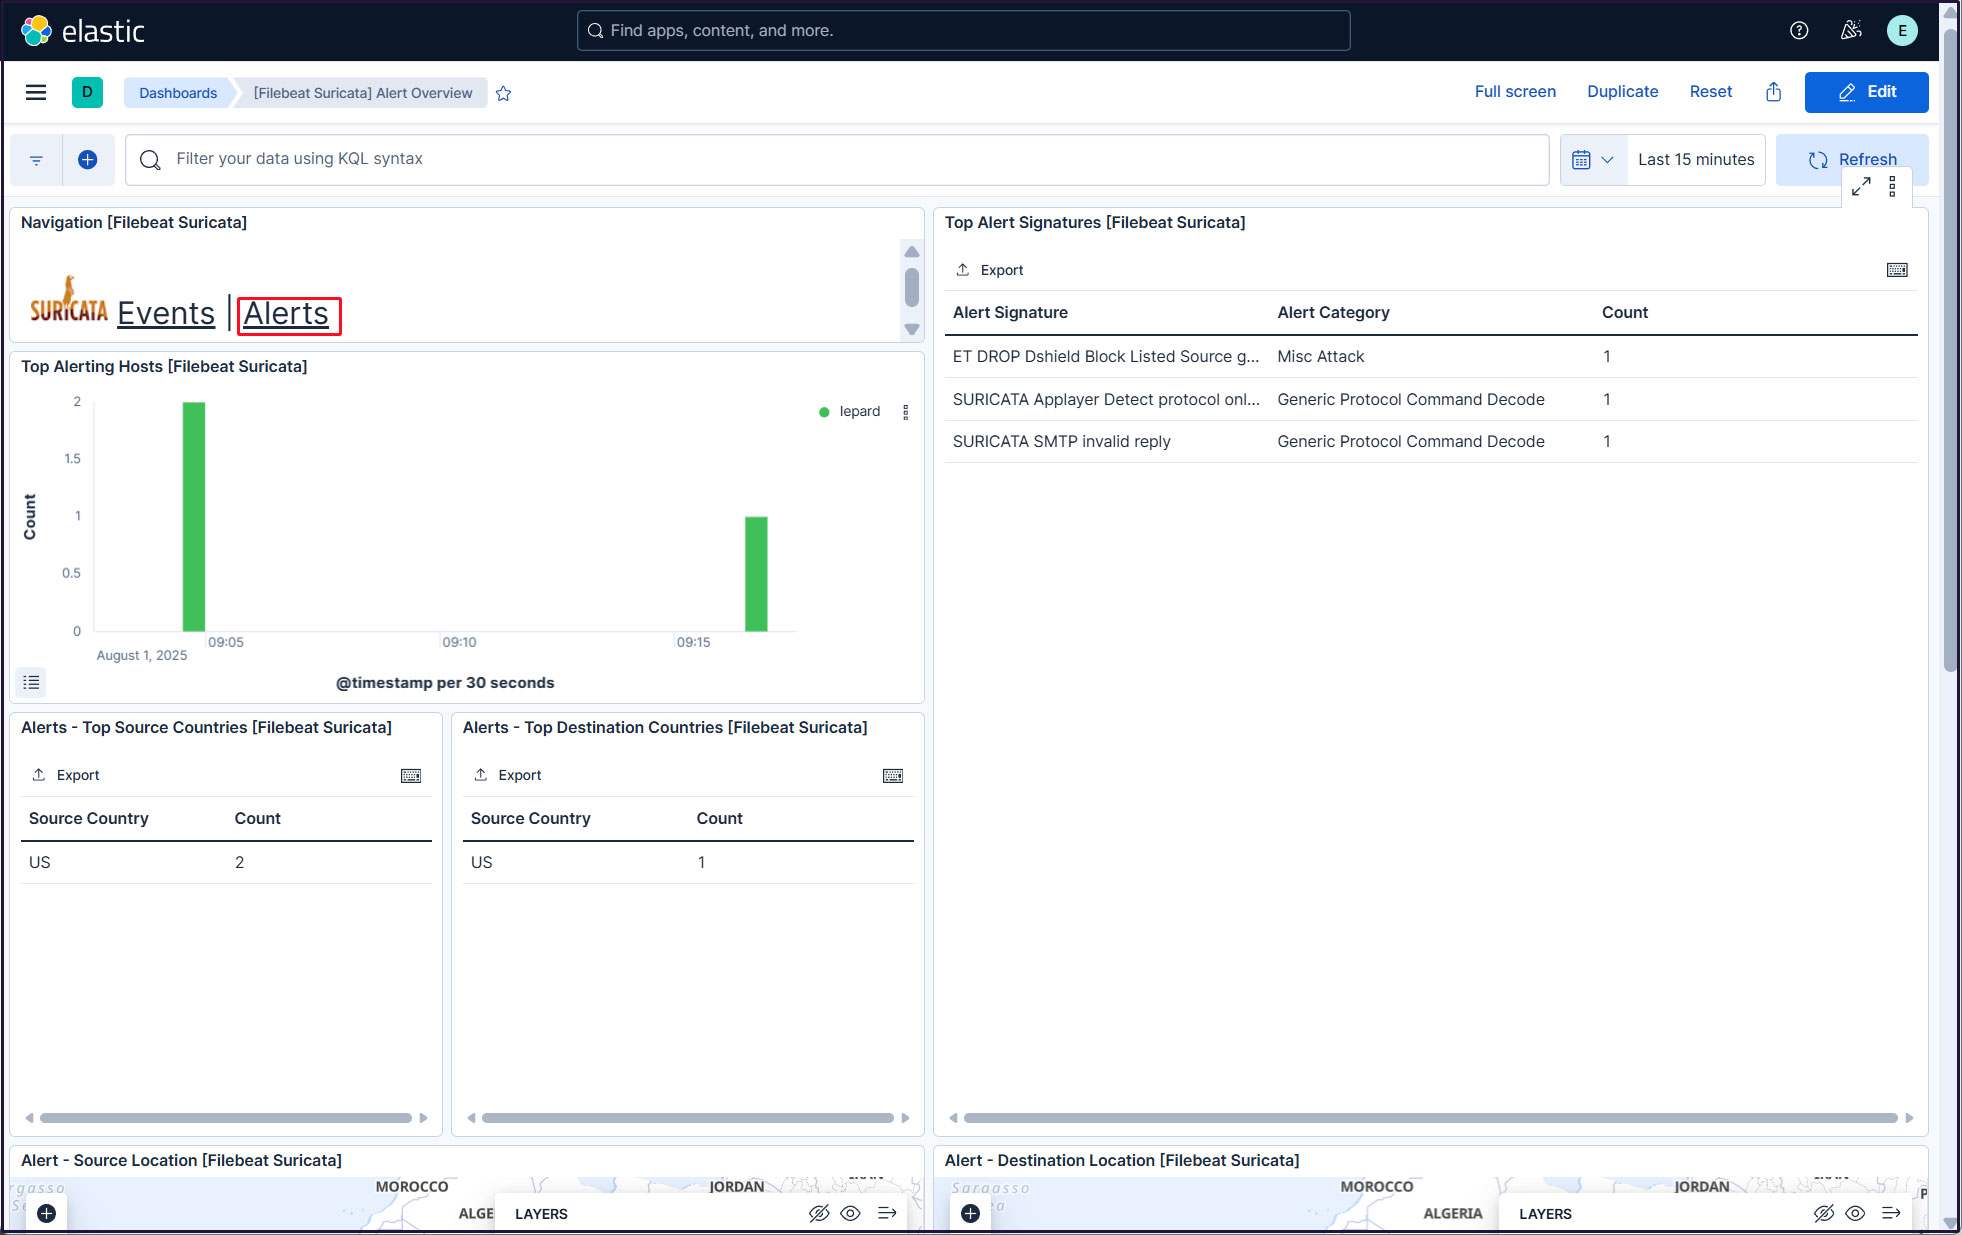
Click on the Alerts text next to the Suricata logo for malicious traffic alerts
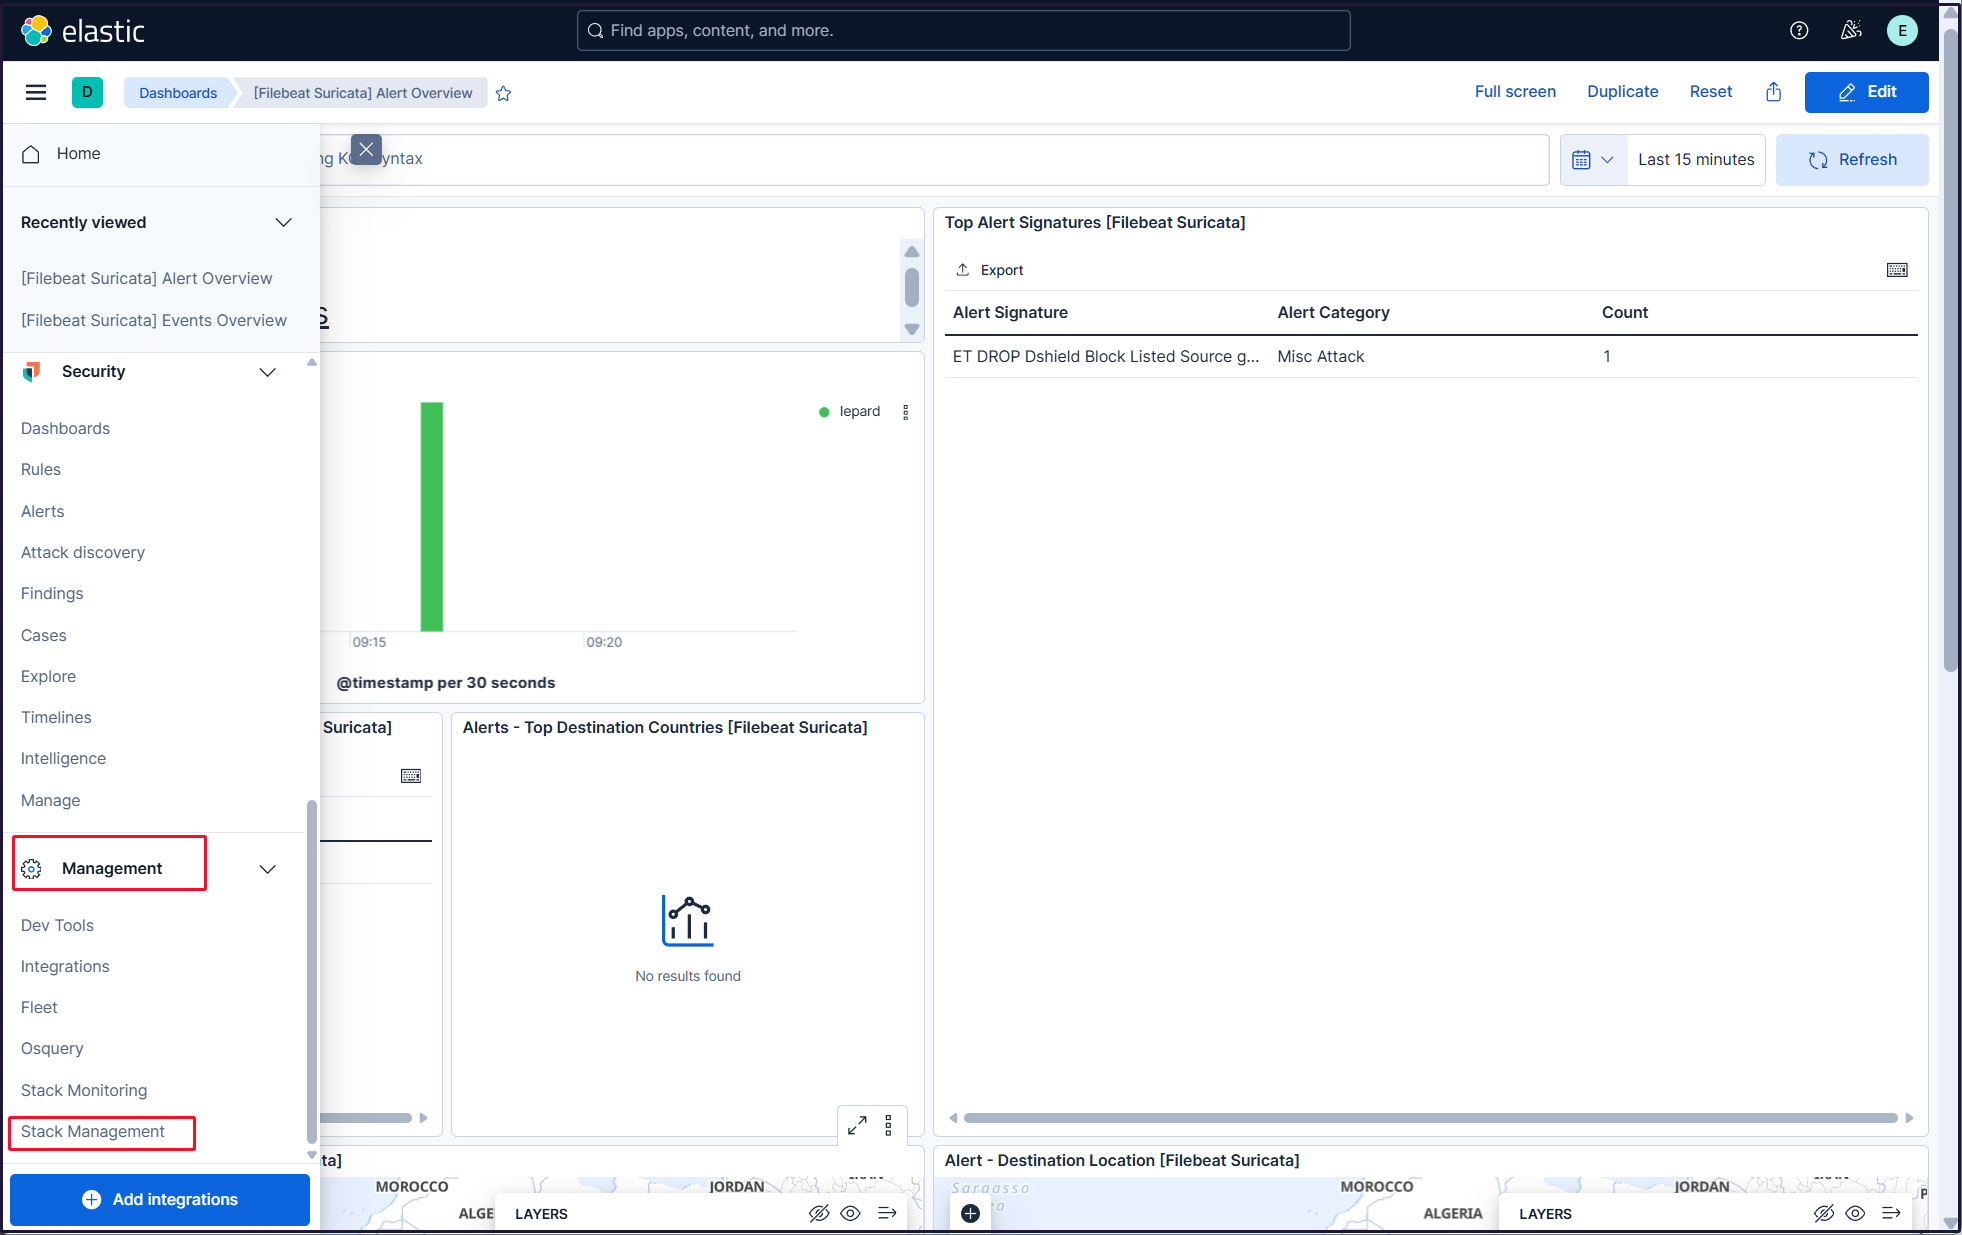
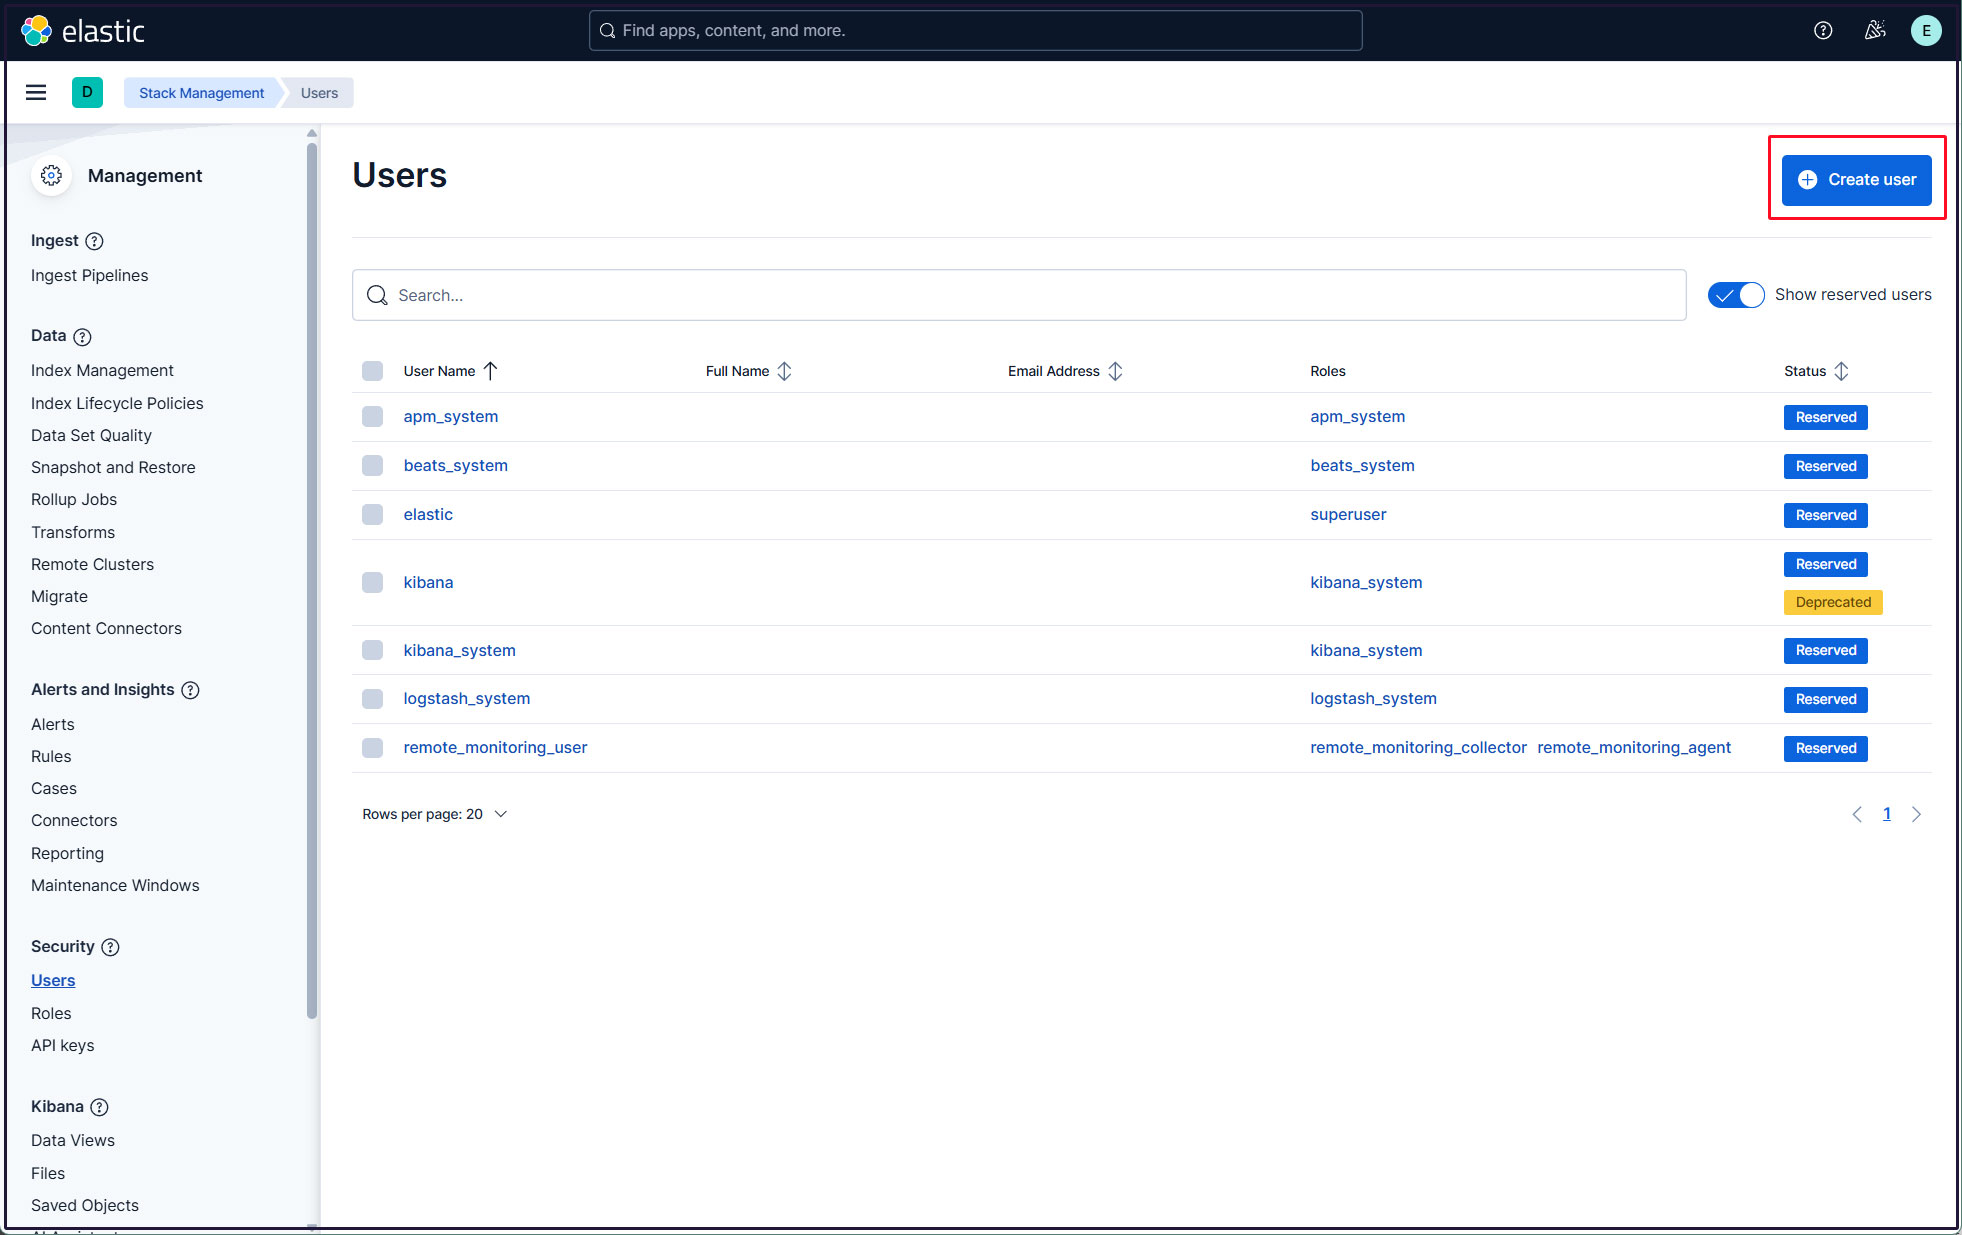
Create a new user account so that you do not have to use the elastic superuser account.
Click on the three-line mark in the upper left corner and select "Stack Management" under "Management"
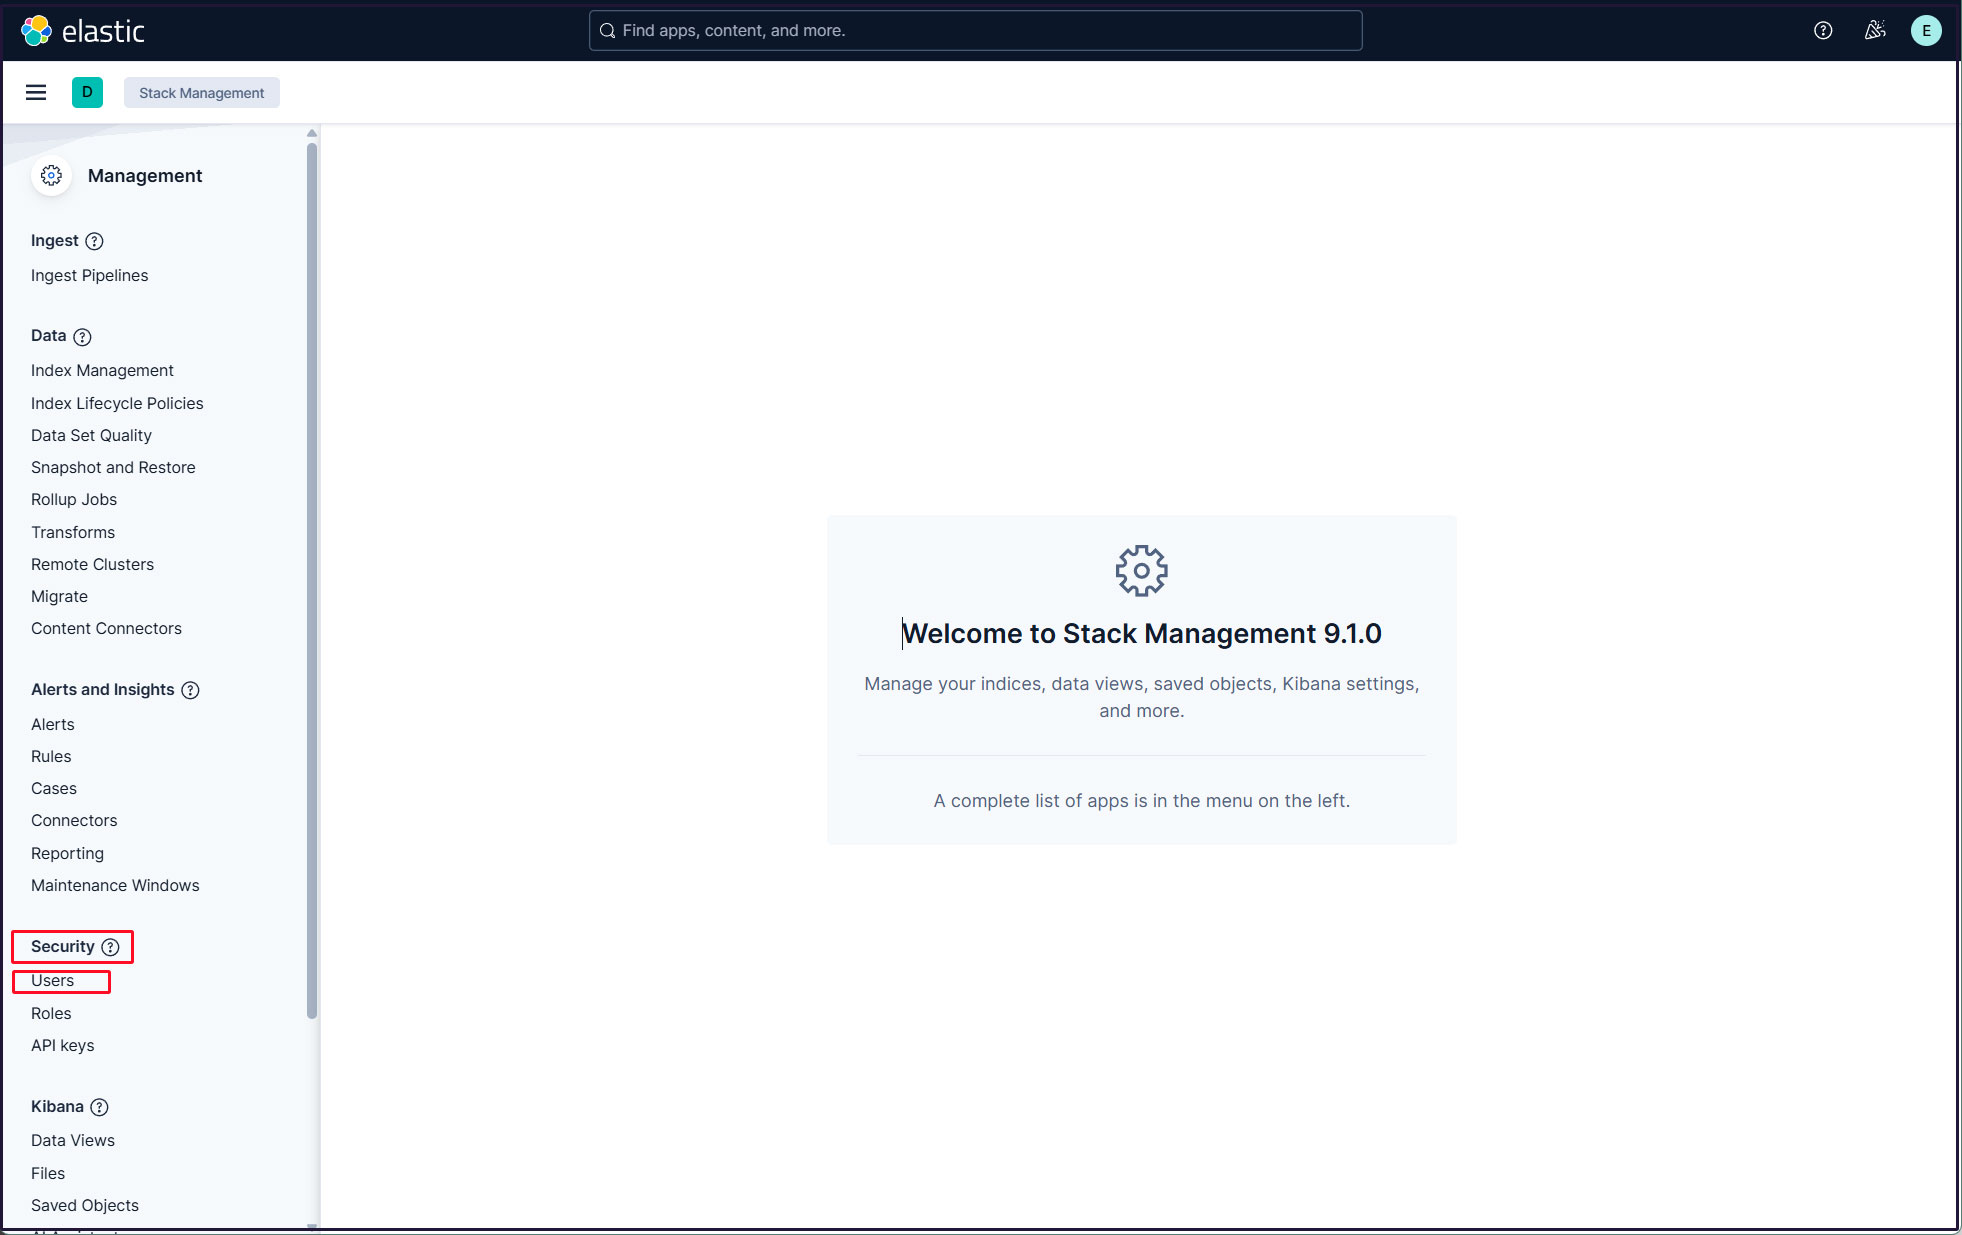
Select "security" and "Users"
Click on the "Create user" button in the upper right corner
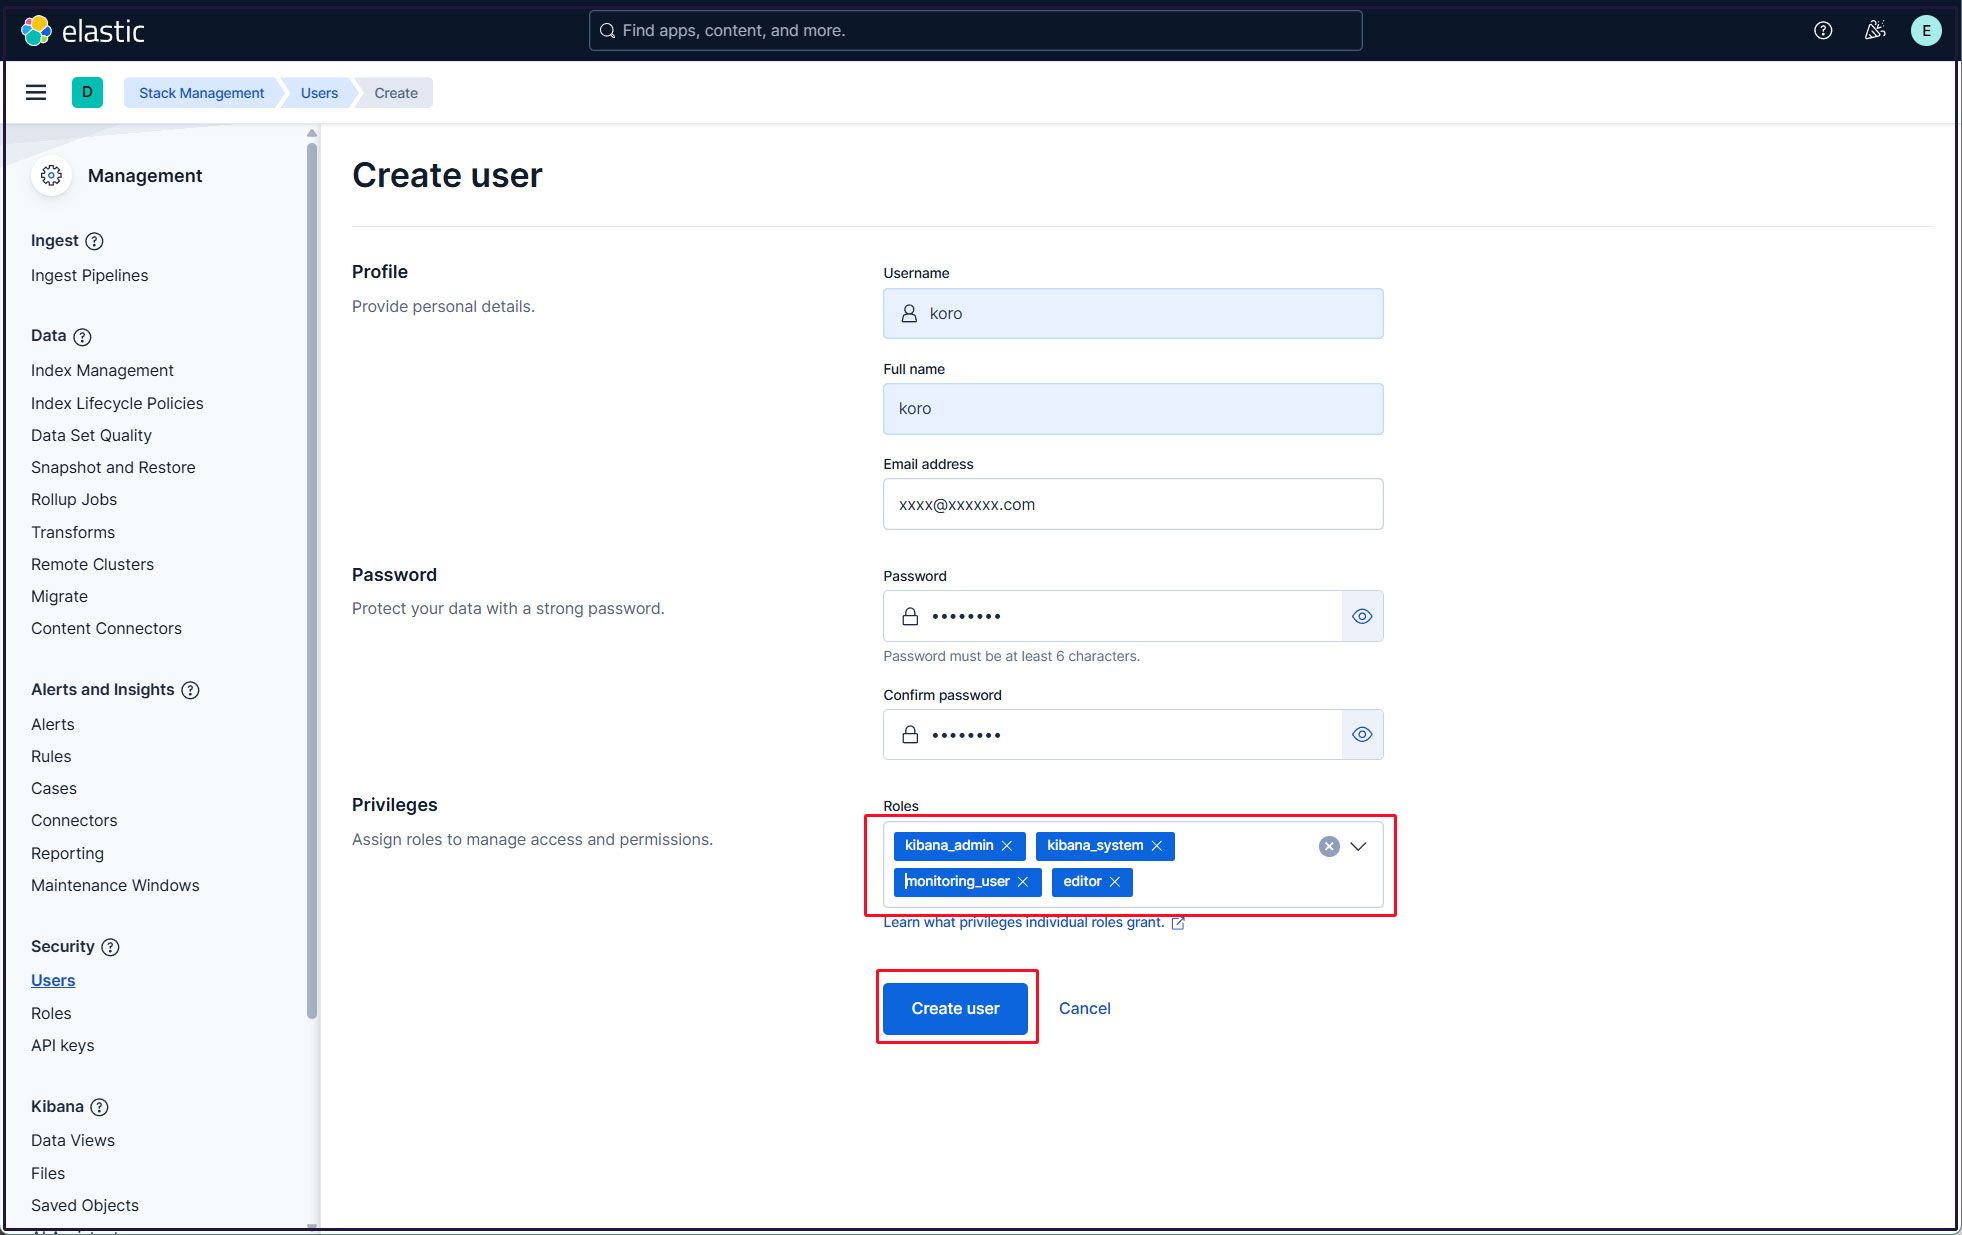
Enter new user information, assign the roles kibana_admin, kibana_system, monitoring_user, and editor in Privileges, and finally click Create user
Log out of the current profile and confirm that you can log in with the newly created user account.