Prerequisites
This time, we will install Suricata IDS and ElasticStack on the following server.
・First Server Suricata IDS & Filebeat : Fedora45 IP address(192.168.11.83)
・Second server Elasticsearch & kibana : Fedora45 IP address(192.168.11.85)
Suricata
SURICATA IDS/IPS is an open source IDS that monitors communications on the network and detects suspicious traffic.
The basic mechanism is signature-based, so it can detect predefined unauthorized communications. Suricata is also characterized by its ability to provide protection as well as detection.
1.Suricata Installation and Configuration
①Suricata Install
# dnf -y install suricata

Version Check
# suricata -V
This is Suricata version 8.0.7 RELEASE
②Determine interface and IP address where Suricata will inspect network packets
# ip --brief add
lo               UNKNOWN        127.0.0.1/8
ens160           UP             192.168.11.83/24
③Edit configuration file
# vi /etc/suricata/suricata.yaml

# Line 15: In the vars section, define the network.
HOME_NET: "[192.168.11.0/24]"

# Per Line 661 : Set the interface name for the af-packet section
af-packet:
    - interface: ens160
# vi /etc/sysconfig/suricata

# Line 8: Specify the interface
# Add options to be passed to the daemon
OPTIONS="-i ens160 --user suricata "
④Suricata rules update
# suricata-update

-----------------------------------------------------------------------------------------
9/11/2026 -- 16:59:15 - <Info> -- Loaded 69364 rules.
9/11/2026 -- 16:59:16 - <Info> -- Disabled 16 rules.
9/11/2026 -- 16:59:16 - <Info> -- Enabled 0 rules.
9/11/2026 -- 16:59:16 - <Info> -- Modified 0 rules.
9/11/2026 -- 16:59:16 - <Info> -- Dropped 0 rules.
9/11/2026 -- 16:59:16 - <Info> -- Enabled 136 rules for flowbit dependencies.
9/11/2026 -- 16:59:16 - <Info> -- Creating directory /var/lib/suricata/rules.
9/11/2026 -- 16:59:16 - <Info> -- Backing up current rules.
9/11/2026 -- 16:59:16 - <Info> -- Writing rules to /var/lib/suricata/rules/suricata.rules: total: 69364; enabled: 53391; added: 69364; removed 0; modified: 0
9/11/2026 -- 16:59:16 - <Info> -- Writing /var/lib/suricata/rules/classification.config
9/11/2026 -- 16:59:16 - <Info> -- Testing with suricata -T.
9/11/2026 -- 16:59:33 - <Info> -- Done.
⑤Activate Suricata
# systemctl enable --now suricata
# systemctl start suricata
Check Log
# tail /var/log/suricata/suricata.log
[8807 - Suricata-Main] 2026-11-09 17:00:45 Info: logopenfile: fast output device (regular) initialized: fast.log
[8807 - Suricata-Main] 2026-11-09 17:00:45 Info: logopenfile: eve-log output device (regular) initialized: eve.json
[8807 - Suricata-Main] 2026-11-09 17:00:45 Info: logopenfile: stats output device (regular) initialized: stats.log
[8807 - Suricata-Main] 2026-11-09 17:00:55 Info: detect: 1 rule files processed. 53391 rules successfully loaded, 0 rules failed, 0 rules skipped
[8807 - Suricata-Main] 2026-11-09 17:00:55 Info: threshold-config: Threshold config parsed: 0 rule(s) found
[8807 - Suricata-Main] 2026-11-09 17:00:55 Info: detect: 53396 signatures processed. 1257 are IP-only rules, 4532 are inspecting packet payload, 47371 inspect application layer, 110 are decoder event only
[8807 - Suricata-Main] 2026-11-09 17:00:56 Info: unix-manager: unix socket '/var/run/suricata/suricata-command.socket'
[8807 - Suricata-Main] 2026-11-09 17:00:56 Info: runmodes: ens160: creating 4 threads
[8815 - W#01-ens160] 2026-11-09 17:00:56 Info: ioctl: ens160: MTU 1500
[8807 - Suricata-Main] 2026-11-09 17:00:56 Notice: threads: Threads created -> W: 4 FM: 1 FR: 1   Engine started.
Check the stats.log file for statistics (updated every 8 seconds by default)
# tail -f /var/log/suricata/stats.log
A more advanced output, EVE JSON, can be generated with the following command
# tail -f /var/log/suricata/eve.json
2. Setting Suricata Rules
①Display of rule sets packaged in Suricata
# ls -al /var/lib/suricata/rules/
total 45008
drwxr-s--- 2 root     suricata       57 Nov  9 16:59 .
drwxrws--- 5 suricata suricata       46 Nov  9 16:59 ..
-rw-r--r-- 1 root     suricata     3228 Nov  9 16:59 classification.config
-rw-r--r-- 1 root     suricata 46084020 Nov  9 16:59 suricata.rules
②Index list of sources providing rule sets
# suricata-update list-sources

Name: abuse.ch/feodotracker
  Vendor: Abuse.ch
  Summary: Abuse.ch Feodo Tracker Botnet C2 IP ruleset
  License: CC0-1.0
Name: abuse.ch/sslbl-blacklist
  Vendor: Abuse.ch
  Summary: Abuse.ch SSL Blacklist
  License: CC0-1.0
  Replaces: sslbl/ssl-fp-blacklist
Name: abuse.ch/sslbl-ja3
  Vendor: Abuse.ch
  Summary: Abuse.ch Suricata JA3 Fingerprint Ruleset
  License: CC0-1.0
  Replaces: sslbl/ja3-fingerprints
Name: abuse.ch/urlhaus
  Vendor: abuse.ch
  Summary: Abuse.ch URLhaus Suricata Rules
  License: CC0-1.0
Name: aleksibovellan/nmap
  Vendor: aleksibovellan
  Summary: Suricata IDS/IPS Detection Rules Against NMAP Scans
  License: MIT
Name: et/open
  Vendor: Proofpoint
  Summary: Emerging Threats Open Ruleset
  License: MIT
Name: et/pro
  Vendor: Proofpoint
  Summary: Emerging Threats Pro Ruleset
  License: Commercial
  Replaces: et/open
  Parameters: secret-code
  Subscription: https://www.proofpoint.com/us/threat-insight/et-pro-ruleset
Name: etnetera/aggressive
  Vendor: Etnetera a.s.
  Summary: Etnetera aggressive IP blacklist
  License: MIT
Name: ipfire/dbl
  Vendor: IPFire
  Summary: IPFire DBL
  License: CC-BY-SA-4.0
Name: julioliraup/antiphishing
  Vendor: julioliraup
  Summary: Antiphishing for protection against phishing attacks
  License: GPL-3.0
Name: oisf/trafficid
  Vendor: OISF
  Summary: Suricata Traffic ID ruleset
  License: MIT
Name: pawpatrules
  Vendor: pawpatrules
  Summary: PAW Patrules is a collection of rules for IDPS / NSM Suricata engine
  License: CC-BY-SA-4.0
Name: ptrules/open
  Vendor: Positive Technologies
  Summary: Positive Technologies Open Ruleset
  License: Custom
Name: scwx/enhanced
  Vendor: Secureworks
  Summary: Secureworks suricata-enhanced ruleset
  License: Commercial
  Parameters: secret-code
  Subscription: https://www.secureworks.com/contact/ (Please reference CTU Countermeasures)
Name: scwx/malware
  Vendor: Secureworks
  Summary: Secureworks suricata-malware ruleset
  License: Commercial
  Parameters: secret-code
  Subscription: https://www.secureworks.com/contact/ (Please reference CTU Countermeasures)
Name: scwx/security
  Vendor: Secureworks
  Summary: Secureworks suricata-security ruleset
  License: Commercial
  Parameters: secret-code
  Subscription: https://www.secureworks.com/contact/ (Please reference CTU Countermeasures)
Name: stamus/lateral
  Vendor: Stamus Networks
  Summary: Lateral movement rules
  License: GPL-3.0-only
Name: stamus/nrd-14-open
  Vendor: Stamus Networks
  Summary: Newly Registered Domains Open only - 14 day list, complete
  License: Commercial
  Parameters: secret-code
  Subscription: https://www.stamus-networks.com/stamus-labs/subscribe-to-threat-intel-feed
Name: stamus/nrd-30-open
  Vendor: Stamus Networks
  Summary: Newly Registered Domains Open only - 30 day list, complete
  License: Commercial
  Parameters: secret-code
  Subscription: https://www.stamus-networks.com/stamus-labs/subscribe-to-threat-intel-feed
Name: stamus/nrd-entropy-14-open
  Vendor: Stamus Networks
  Summary: Newly Registered Domains Open only - 14 day list, high entropy
  License: Commercial
  Parameters: secret-code
  Subscription: https://www.stamus-networks.com/stamus-labs/subscribe-to-threat-intel-feed
Name: stamus/nrd-entropy-30-open
  Vendor: Stamus Networks
  Summary: Newly Registered Domains Open only - 30 day list, high entropy
  License: Commercial
  Parameters: secret-code
  Subscription: https://www.stamus-networks.com/stamus-labs/subscribe-to-threat-intel-feed
Name: stamus/nrd-phishing-14-open
  Vendor: Stamus Networks
  Summary: Newly Registered Domains Open only - 14 day list, phishing
  License: Commercial
  Parameters: secret-code
  Subscription: https://www.stamus-networks.com/stamus-labs/subscribe-to-threat-intel-feed
Name: stamus/nrd-phishing-30-open
  Vendor: Stamus Networks
  Summary: Newly Registered Domains Open only - 30 day list, phishing
  License: Commercial
  Parameters: secret-code
  Subscription: https://www.stamus-networks.com/stamus-labs/subscribe-to-threat-intel-feed
Name: tgreen/hunting
  Vendor: tgreen
  Summary: Threat hunting rules
  License: GPLv3
③Enable source (if tgreen/hunting is enabled)
# suricata-update enable-source tgreen/hunting
10/11/2026 -- 09:55:56 - <Info> -- Using data-directory /var/lib/suricata.
10/11/2026 -- 09:55:56 - <Info> -- Using Suricata configuration /etc/suricata/suricata.yaml
10/11/2026 -- 09:55:56 - <Info> -- Using /usr/share/suricata/rules for Suricata provided rules.
10/11/2026 -- 09:55:56 - <Info> -- Found Suricata version 8.0.7 at /usr/sbin/suricata.
10/11/2026 -- 09:55:56 - <Warning> -- Source index does not exist, will use bundled one.
10/11/2026 -- 09:55:56 - <Warning> -- Please run suricata-update update-sources.
10/11/2026 -- 09:55:56 - <Info> -- Creating directory /var/lib/suricata/update/sources
10/11/2026 -- 09:55:56 - <Info> -- Enabling default source et/open
10/11/2026 -- 09:55:56 - <Info> -- Source tgreen/hunting enabled
Perform update
# suricata-update update-sources
10/11/2026 -- 09:56:31 - <Info> -- Using data-directory /var/lib/suricata.
10/11/2026 -- 09:56:31 - <Info> -- Using Suricata configuration /etc/suricata/suricata.yaml
10/11/2026 -- 09:56:31 - <Info> -- Using /usr/share/suricata/rules for Suricata provided rules.
10/11/2026 -- 09:56:31 - <Info> -- Found Suricata version 8.0.7 at /usr/sbin/suricata.
10/11/2026 -- 09:56:31 - <Info> -- Downloading https://www.openinfosecfoundation.org/rules/index.yaml
10/11/2026 -- 09:56:32 - <Info> -- Adding all sources
10/11/2026 -- 09:56:32 - <Info> -- Saved /var/lib/suricata/update/cache/index.yaml
Restart Suricata service
# systemctl restart suricata
3. Creating Suricata Custom Rules
①Create files containing customer rules
# vi /var/lib/suricata/rules/local.rules
Please include the following information:
alert icmp any any -> any any (msg:"ICMP Ping"; sid:100001; rev:1;)
②Edit configuration file (define new rule paths)
# vi /etc/suricata/suricata.yaml

# Add around line 2342
default-rule-path: /var/lib/suricata/rules

rule-files:
  - suricata.rules
  - local.rules
③Testing the configuration file
# suricata -T -c /etc/suricata/suricata.yaml -v
Notice: suricata: This is Suricata version 8.0.7 RELEASE running in SYSTEM mode
Info: cpu: CPUs/cores online: 4
Info: suricata: Running suricata under test mode
Info: suricata: Setting engine mode to IDS mode by default
Info: exception-policy: master exception-policy set to: auto
Info: suricata: Preparing unexpected signal handling
Info: logopenfile: fast output device (regular) initialized: fast.log
Info: logopenfile: eve-log output device (regular) initialized: eve.json
Info: logopenfile: stats output device (regular) initialized: stats.log
Info: detect: 2 rule files processed. 53392 rules successfully loaded, 0 rules failed, 0 rules skipped
Info: threshold-config: Threshold config parsed: 0 rule(s) found
Info: detect: 53397 signatures processed. 1258 are IP-only rules, 4532 are inspecting packet payload, 47371 inspect application layer, 110 are decoder event only
Notice: suricata: Configuration provided was successfully loaded. Exiting.
Restart Suricat service
# systemctl restart suricata
④Testing the application of Custom Rules
Ping another device on the same local network to see if it was logged
# cat /var/log/suricata/fast.log

11/10/2026-10:26:06.693717  [**] [1:100000:1] ICMP Ping [**] [Classification: (null)] [Priority: 3] {ICMP} 192.168.11.36:8 -> 192.168.11.83:0
11/10/2026-10:26:06.693863  [**] [1:100000:1] ICMP Ping [**] [Classification: (null)] [Priority: 3] {ICMP} 192.168.11.83:0 -> 192.168.11.36:0
To get logs in JSON format, install jq on your system
# dnf install jq
Execute the following command to ping another device on the same local network
# tail -f /var/log/suricata/eve.json | jq 'select(.event_type=="alert")'
When you run ping, the console displays the following:
{
  "timestamp": "2026-11-10T10:46:50.966795+0900",
  "flow_id": 774460759706172,
  "in_iface": "ens160",
  "event_type": "alert",
  "src_ip": "192.168.11.83",
  "dest_ip": "192.168.11.36",
  "proto": "ICMP",
  "ip_v": 4,
  "icmp_type": 0,
  "icmp_code": 0,
  "pkt_src": "wire/pcap",
  "alert": {
    "action": "allowed",
    "gid": 1,
    "signature_id": 100001,
    "rev": 1,
    "signature": "ICMP Ping",
    "category": "",
    "severity": 3
  },
4. Configuring Suricata as an IPS
Configure Suricata to start in IPS mode to drop malicious network traffic.
①Edit the SURICATA configuration file located at /etc/sysconfig/suricata
# vi /etc/sysconfig/suricata

Line 8 : Comment
#OPTIONS="-i ens160 --user suricata "

Add the following to line 9 to tell SURICATA to run in IPS mode
OPTIONS="-q 0 -vvv --user suricata"
➁Restart Suricata
# systemctl restart suricata.service
➂Direct incoming network traffic to Suricata's NFQUEUE
Firewalld is installed and enabled, so add the necessary rules for Suricata to Firewalld.
# firewall-cmd --permanent --direct --add-rule ipv4 filter INPUT 0 -p tcp --dport 2244 -j NFQUEUE --queue-bypass
# firewall-cmd --permanent --direct --add-rule ipv4 filter OUTPUT 0 -p tcp --sport 2244 -j NFQUEUE --queue-bypass

Add a FORWARD rule so that when the server acts as a gateway for other systems, all that traffic is also sent to SURICATA for processing.
# firewall-cmd --permanent --direct --add-rule ipv4 filter FORWARD 0 -j NFQUEUE
# firewall-cmd --permanent --direct --add-rule ipv6 filter FORWARD 0 -j NFQUEUE

The last two INPUT and OUTPUT rules send all remaining traffic that is not SSH traffic to Suricata for processing.
# firewall-cmd --permanent --direct --add-rule ipv4 filter INPUT 1 -j NFQUEUE
# firewall-cmd --permanent --direct --add-rule ipv4 filter OUTPUT 1 -j NFQUEUE

Do the same for IPv6.
# firewall-cmd --permanent --direct --add-rule ipv6 filter INPUT 1 -j NFQUEUE
# firewall-cmd --permanent --direct --add-rule ipv6 filter OUTPUT 1 -j NFQUEUE

Reload Firewalld
# firewall-cmd --reload
④Test this rule
Change/var/lib/suricata/rules/local.rules to drop
# vi /var/lib/suricata/rules/local.rules

drop icmp any any -> any any (msg:"ICMP Ping"; sid:100001; rev:1;)
⑤Restart Suricata service
# systemctl restart suricata
⑥When I ping from another device on my local local network and check eve.json
"action": "blocked"
# jq 'select(.alert .signature_id==100001)' /var/log/suricata/eve.json

{
  "timestamp": "2026-11-10T11:18:27.377640+0900",
  "flow_id": 1059005664450479,
  "event_type": "alert",
  "src_ip": "192.168.11.36",
  "dest_ip": "192.168.11.83",
  "proto": "ICMP",
  "ip_v": 4,
  "icmp_type": 8,
  "icmp_code": 0,
  "pkt_src": "wire/pcap",
  "alert": {
    "action": "blocked",
    "gid": 1,
    "signature_id": 100001,
    "rev": 1,
    "signature": "ICMP Ping",
    "category": "",
    "severity": 3
  },
Integration of the ELK Stack and Suricata
Install and configure the Elastic Stack to visualize and search SURICATA logs
This section is primarily performed on a second Fedora45 Server(IP:192.168.11.85)
1. Elasticsearch Install
1.1 Install the Elastic Stack 9.x repository signing key
# rpm --import https://artifacts.elastic.co/GPG-KEY-elasticsearch
1.2 Create a repository definition in the /etc/yum/yum.repos.d directory
Key changes to Fedora45 repository settings
- Change the destination of the official repository
Standard.repo files managed by packages (such as fedora.repo and fedora-updates.repo) are located in /usr/share/dnf5/repos.d/. - The following repositions are initially placed:
fedora-cisco-openh264.repo
fedora.repo
fedora-updates.repo
fedora-updates-testing.repo - Change the destination of the GPG public key
The key file for package signature verification has also been migrated to/usr/share/pki/rpm-gpg/. - Separating additional user settings
/etc/yum.repos.d/ defaults to empty and serves as the location for third-party repositories that users add manually. - How to override settings
If you want to change the settings in the standard repository, use the dnf config-manager command without editing the files directly. When run, it will generate an overwrite configuration under/etc/dnf/repos.override.d/
Therefore, create an Elasticsearch repository in /etc/yum.repos.d/
# vi /etc/yum.repos.d/elasticsearch.repo

The following content is recorded
[elasticsearch]
name=Elasticsearch repository for 9.x packages
baseurl=https://artifacts.elastic.co/packages/9.x/yum
gpgcheck=1
gpgkey=https://artifacts.elastic.co/GPG-KEY-elasticsearch
enabled=0
autorefresh=1
type=rpm-md
1.3 Elasticsearch Install
# dnf -y install --enablerepo=elasticsearch elasticsearch
2. Elasticsearch Configuration
Elasticsearch is configured by default to accept only local connections.
Additionally, tools such as Filebeat cannot send logs because authentication is not enabled.
This time, we will configure Elasticsearch's network settings and enable the xpack security module built into Elasticsearch.
2.1 Elasticsearch Network Configuration
Since the Elasticsearch and SURICATA servers are separate, Elasticsearch must be configured to listen for connections on the private network interface.
# vi /etc/elasticsearch/elasticsearch.yml

Line 57 : Add the local address of the Elasticsearch server
#network.host: 192.168.0.1
network.host: 192.168.11.85

Line 62 : Uncomments
http.port: 9200
2.2 Start Elasticsearch
# systemctl daemon-reload
# systemctl enable elasticsearch.service
# systemctl start elasticsearch.service
2.3 Create passwords for elastic and kibana_system
Be sure to copy the passwords for the elastic user and kibana_system user, as they will be needed later.
The kibana_system user is used for configuring Kibana.
The elastic user is used for configuring Filebeat and Auditbeat, and for logging into Kibana.
If you forget your password, you can use the command again to reset it.
[elastic] User password creation
# cd /usr/share/elasticsearch/bin

# ./elasticsearch-reset-password -u elastic
This tool will reset the password of the [elastic] user to an autogenerated value.
The password will be printed in the console.
Please confirm that you would like to continue [y/N]y


Password for the [elastic] user successfully reset.
New value: K6J-ZXn80rVFpshOD6Tj
※Resetting Elasticsearch Passwords
The automatically generated Elastic user password is too complex, so you can reset it using the /usr/share/elasticsearch/bin/elasticsearch-reset-password command.
To reset your password, execute the command.
# /usr/share/elasticsearch/bin/elasticsearch-reset-password -u elastic -i

This tool will reset the password of the [elastic] user.
You will be prompted to enter the password.
Please confirm that you would like to continue [y/N]y


Enter password for [elastic]:
Re-enter password for [elastic]:
Password for the [elastic] user successfully reset.
[kibana_system] User Password Creation
# cd /usr/share/elasticsearch/bin

# ./elasticsearch-reset-password -u kibana_system
This tool will reset the password of the [kibana_system] user to an autogenerated value.
The password will be printed in the console.
Please confirm that you would like to continue [y/N]y


Password for the [kibana_system] user successfully reset.
New value: xpAZ+EF4--kkYeChNSWU
3. Installing and Configuring Kibana
This section is primarily performed on the second Fedora45 Server(IP:192.168.11.85)
3.1 Kibana Installation
# dnf -y install --enablerepo=elasticsearch kibana
3.2 xpack Security Module Configuration
Enable Kibana's xpack security features to generate several encryption keys that Kibana uses to store data in Elasticsearch.
Encryption keys are created using the kibana-encryption-keys utility located in the /usr/share/kibana/bin directory.
Store the three keys you created in a secure location.
# cd /usr/share/kibana/bin/
# ./kibana-encryption-keys generate -q --force
xpack.encryptedSavedObjects.encryptionKey: 4a1bb45bc652c68f54d22907616350006f89fab5810fd8067d71a8dbb0db599c
xpack.reporting.encryptionKey: c2c101eb2a2c89dd177c5e661e5be48a8d9041bb2aa56290453bdc75c424775b
xpack.security.encryptionKey: 68e0afa9e7b054a5e7ab7b9bbb516f6cd6c4b4b275c812953a1e7fb24d1fb412
Add these keys to Kibana's /etc/kibana/kibana.yml configuration file.
# vi /etc/kibana/kibana.yml

Described in the last line
xpack.encryptedSavedObjects.encryptionKey: 4a1bb45bc652c68f54d22907616350006f89fab5810fd8067d71a8dbb0db599c
xpack.reporting.encryptionKey: c2c101eb2a2c89dd177c5e661e5be48a8d9041bb2aa56290453bdc75c424775b
xpack.security.encryptionKey: 68e0afa9e7b054a5e7ab7b9bbb516f6cd6c4b4b275c812953a1e7fb24d1fb412
3.2 Kibana Network Configuration
# vi /etc/kibana/kibana.yml

Line 6 : Uncomments
server.port: 5601

Line 12 : Add the server's private IP address (192.168.11.85)
#server.host: "localhost"
server.host: "192.168.11.85"
3.3 Generating a Kibana-Elasticsearch Enrollment Token
To configure a Kibana instance to communicate with an existing Elasticsearch cluster with security enabled, an enrollment token is required. An enrollment token for Kibana can be generated using the following command:
# /usr/share/elasticsearch/bin/elasticsearch-create-enrollment-token -s kibana

eyJ2ZXIiOiI4LjE0LjAiLCJhZHIiOlsiMTkyLjE2OC4xMS44NTo5MjAwIl0sImZnciI6IjdlZmY0Yjk2YWJmMDRiM2ZkYzhlYmNjMzU4NGExZGI3MDZkZmU5NTc3NDI5MjYxY2YxN2QwZjcyOGQ0NjZmMWUiLCJrZXkiOiJabHlheEtFQmpCTVhMYkNmMENfdzpIeHljZ19GeWJVcUVwek9fbVpNeHFRIn0=
3.4 Starting Kibana
Launch Kibana 9 and configure it to run at system startup.
# systemctl enable --now kibana
# systemctl start kibana
Status Check
# systemctl status kibana

● kibana.service - Kibana
     Loaded: loaded (/usr/lib/systemd/system/kibana.service; enabled; preset: disabled)
    Drop-In: /usr/lib/systemd/system/service.d
             └─10-timeout-abort.conf
     Active: active (running) since Tue 2026-11-10 17:38:21 JST; 33s ago
 Invocation: 196b833b45cf428da288e6f623088a75
       Docs: https://www.elastic.co
   Main PID: 3201 (MainThread)
      Tasks: 11 (limit: 4558)
     Memory: 868.2M (peak: 868.2M)
        CPU: 10.727s
     CGroup: /system.slice/kibana.service
             └─3201 /usr/share/kibana/bin/../node/default/bin/node /usr/share/kibana/bin/../node_modules/@kbn/cli/kibana/dist

Nov 10 17:38:23 Lion kibana[3201]: Native global console methods have been overridden in production environment.
Nov 10 17:38:25 Lion kibana[3201]: [2026-11-10T17:38:25.232+09:00][INFO ][root] Kibana is starting
Nov 10 17:38:25 Lion kibana[3201]: [2026-11-10T17:38:25.268+09:00][INFO ][node] Kibana process configured with roles: [backgr>
Nov 10 17:38:32 Lion kibana[3201]: [2026-11-10T17:38:32.551+09:00][INFO ][plugins-service] The following plugins are disabled>
Nov 10 17:38:32 Lion kibana[3201]: [2026-11-10T17:38:32.605+09:00][INFO ][http.server.Preboot] http server running at http://>
Nov 10 17:38:32 Lion kibana[3201]: [2026-11-10T17:38:32.778+09:00][INFO ][plugins-system.preboot] Setting up [1] plugins: [in>
Nov 10 17:38:32 Lion kibana[3201]: [2026-11-10T17:38:32.793+09:00][INFO ][preboot] "interactiveSetup" plugin is holding setup>
Nov 10 17:38:32 Lion kibana[3201]: [2026-11-10T17:38:32.817+09:00][INFO ][root] Holding setup until preboot stage is complete>
Nov 10 17:38:42 Lion kibana[3201]: i Kibana has not been configured.
Nov 10 17:38:42 Lion kibana[3201]: Go to http://192.168.11.85:5601/?code=080262 to get started.
The following appears toward the end of the output:
Go to http://192.168.11.85:5601/?code=080262 to get started.
Copy the provided Kibana URL (including the code) and use it in your browser to access Kibana and complete the setup.
4. Accessing the Kibana 9 Dashboard
Accsess http://192.168.11.85:5601/?code=080262
(Copy each person's appropriate address)
If the firewall is running, open the Kibana port.
# firewall-cmd --add-port=5601/tcp --permanent
# firewall-cmd --reload
When you access Kibana 9, the welcome page prompts you to configure Elastic.
First, enter the generated registration token.
Copy the Kibana token generated using the command /usr/share/elasticsearch/bin/elasticsearch-create-enrollment-token -s kibana and paste it into the box
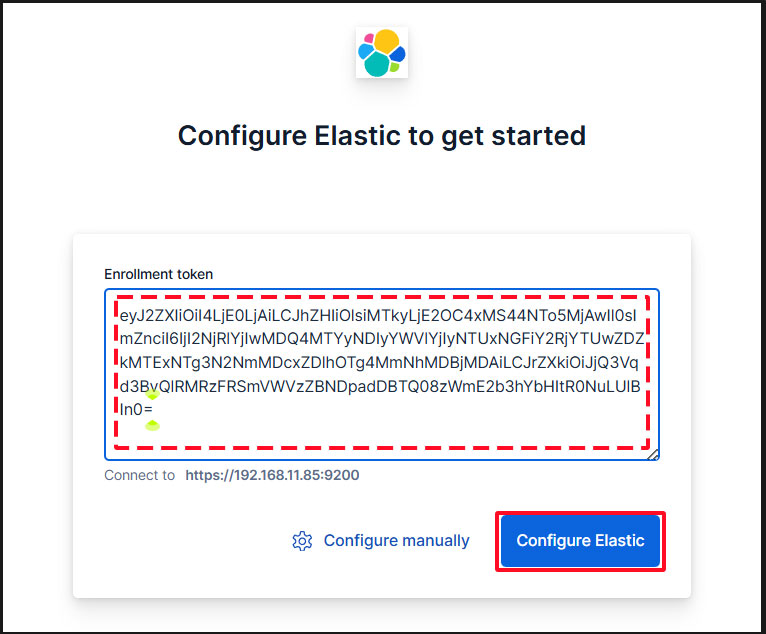
Paste the token, and Kibana will automatically connect to Elasticsearch.
Click Configure Elastic. The settings will be saved, and Elasticsearch will be configured and restarted.
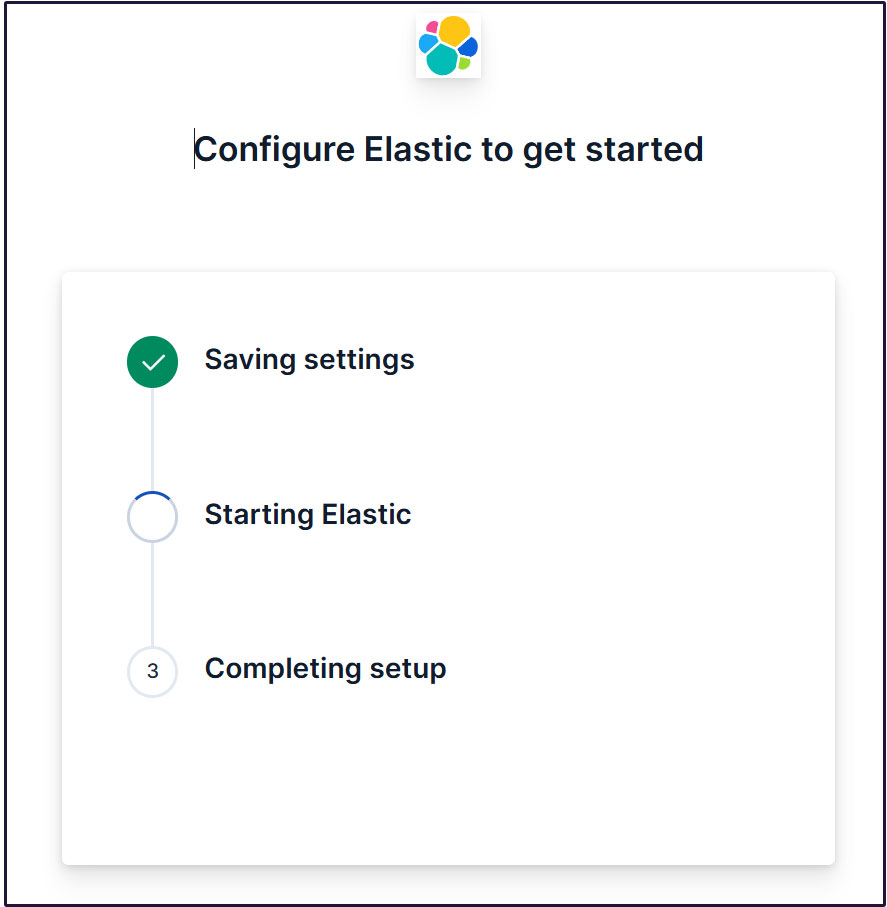
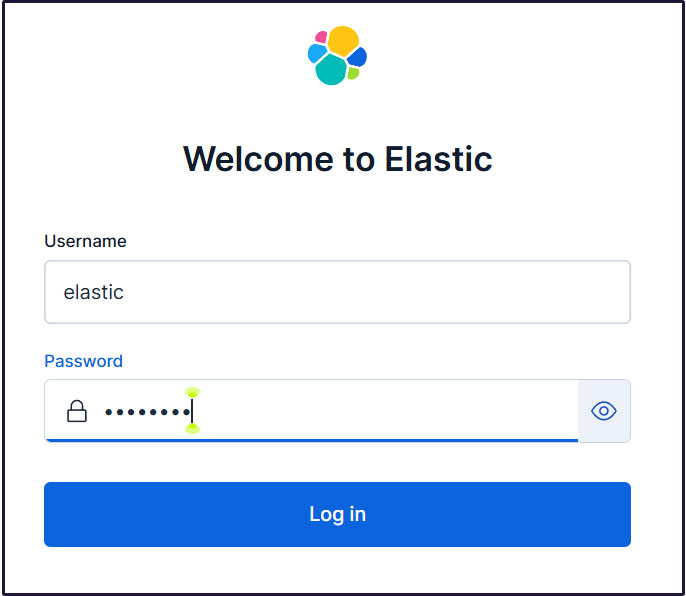
Proceed to the login page. Log in using the generated Elastic user credentials.
Username : elastic
Password : Password regenerated for clarity
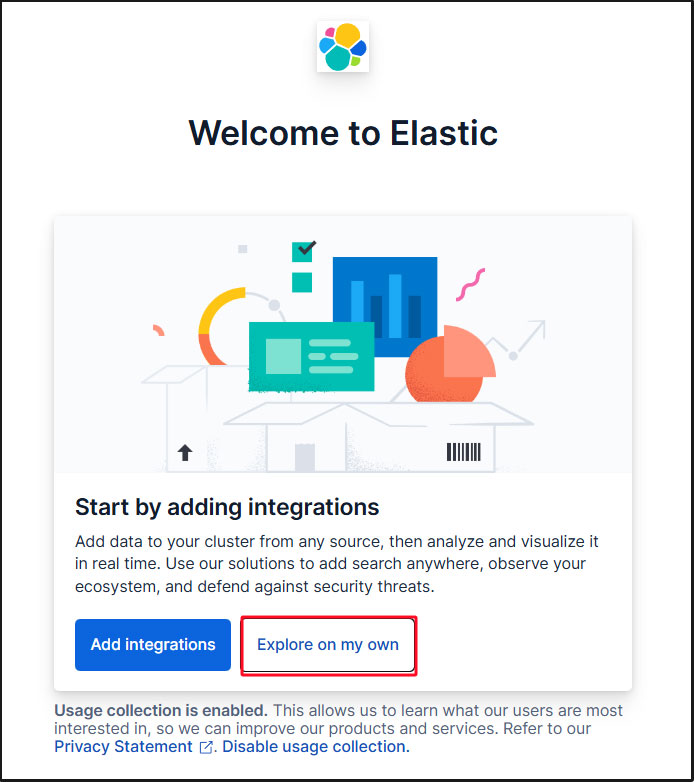
On the welcome page, click "Explore on my own" to proceed to the Kibana 9.x dashboard.
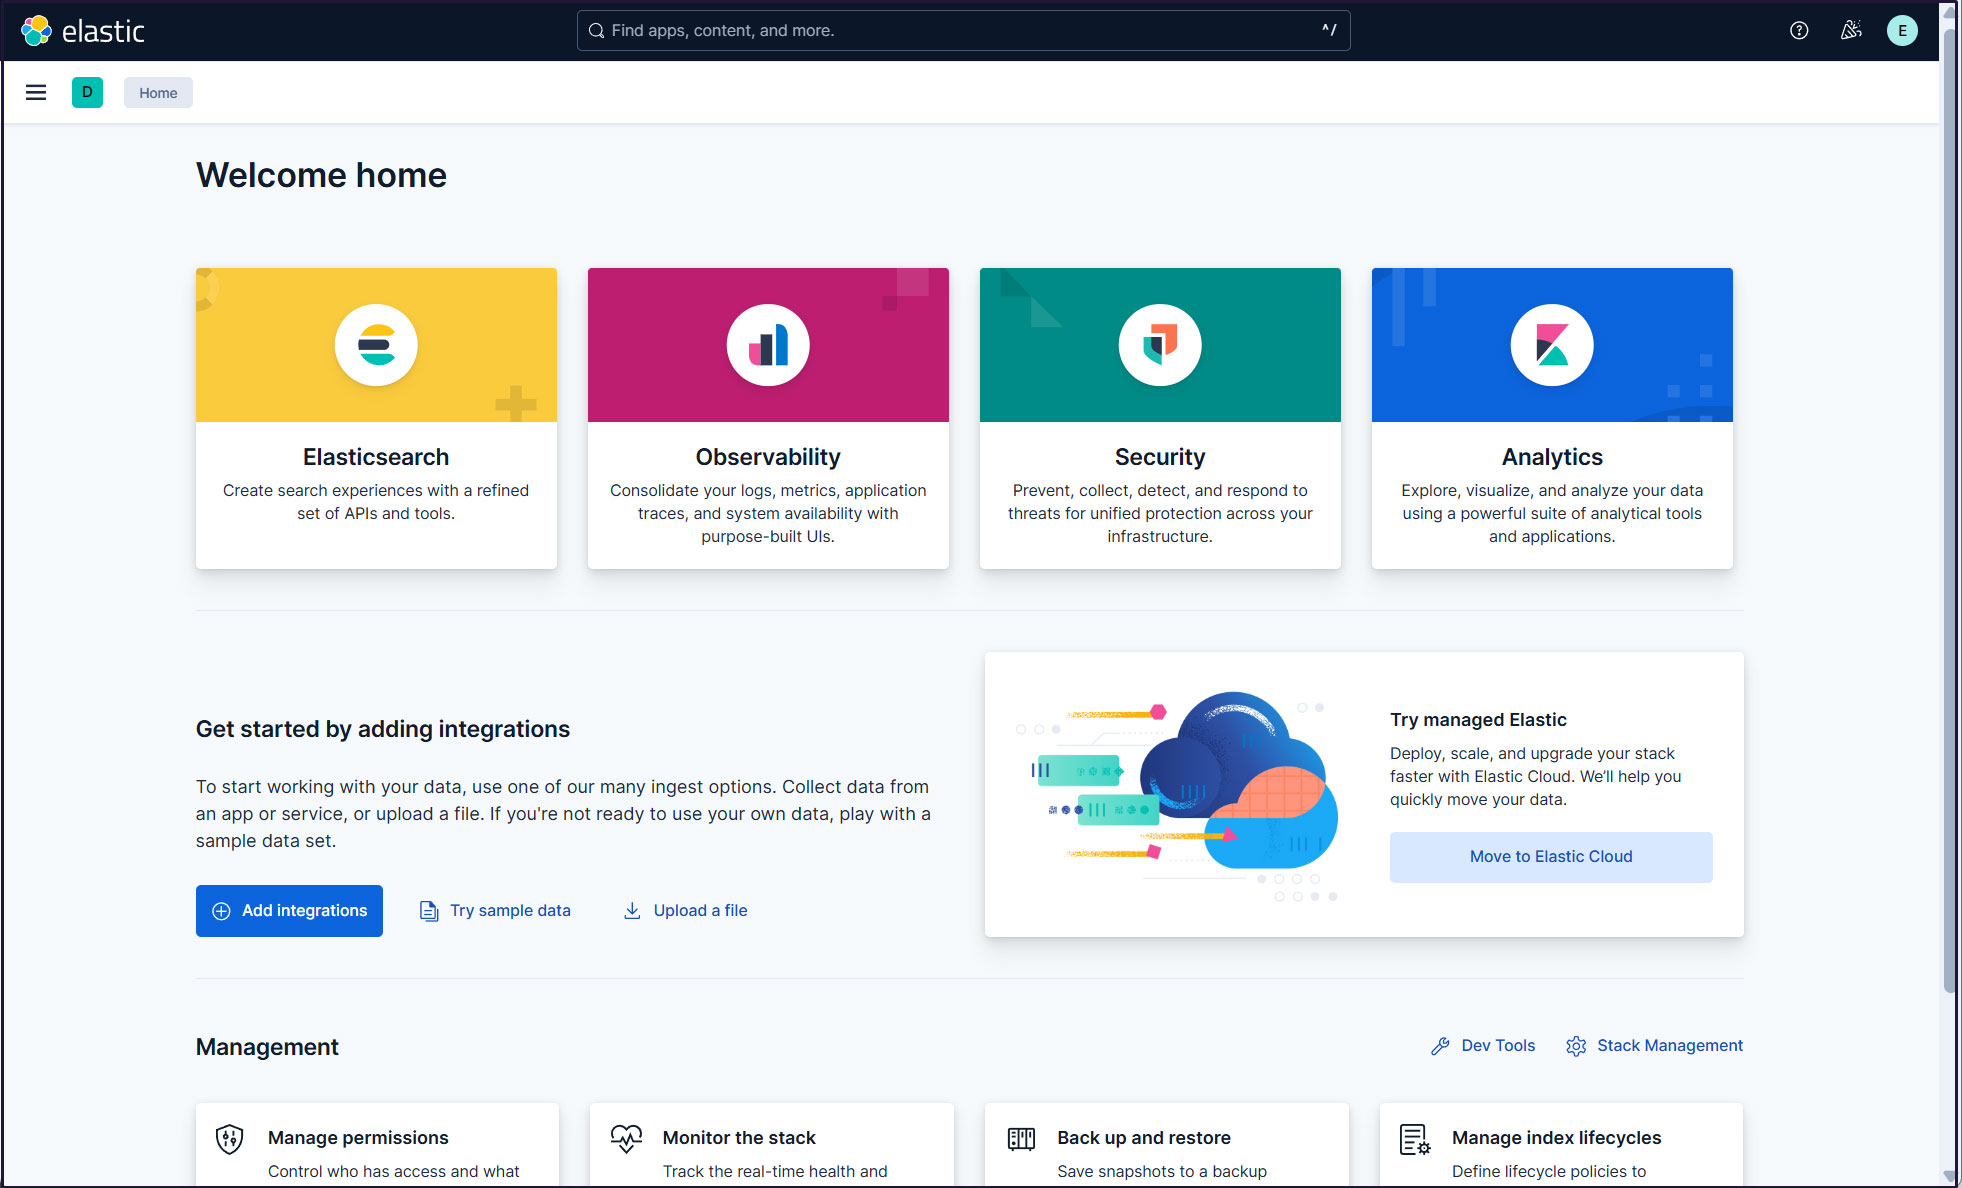
Create a new user account so that you do not need to use the elastic superuser account.
Open the main menu, then navigate to Stack Management > Security > Users
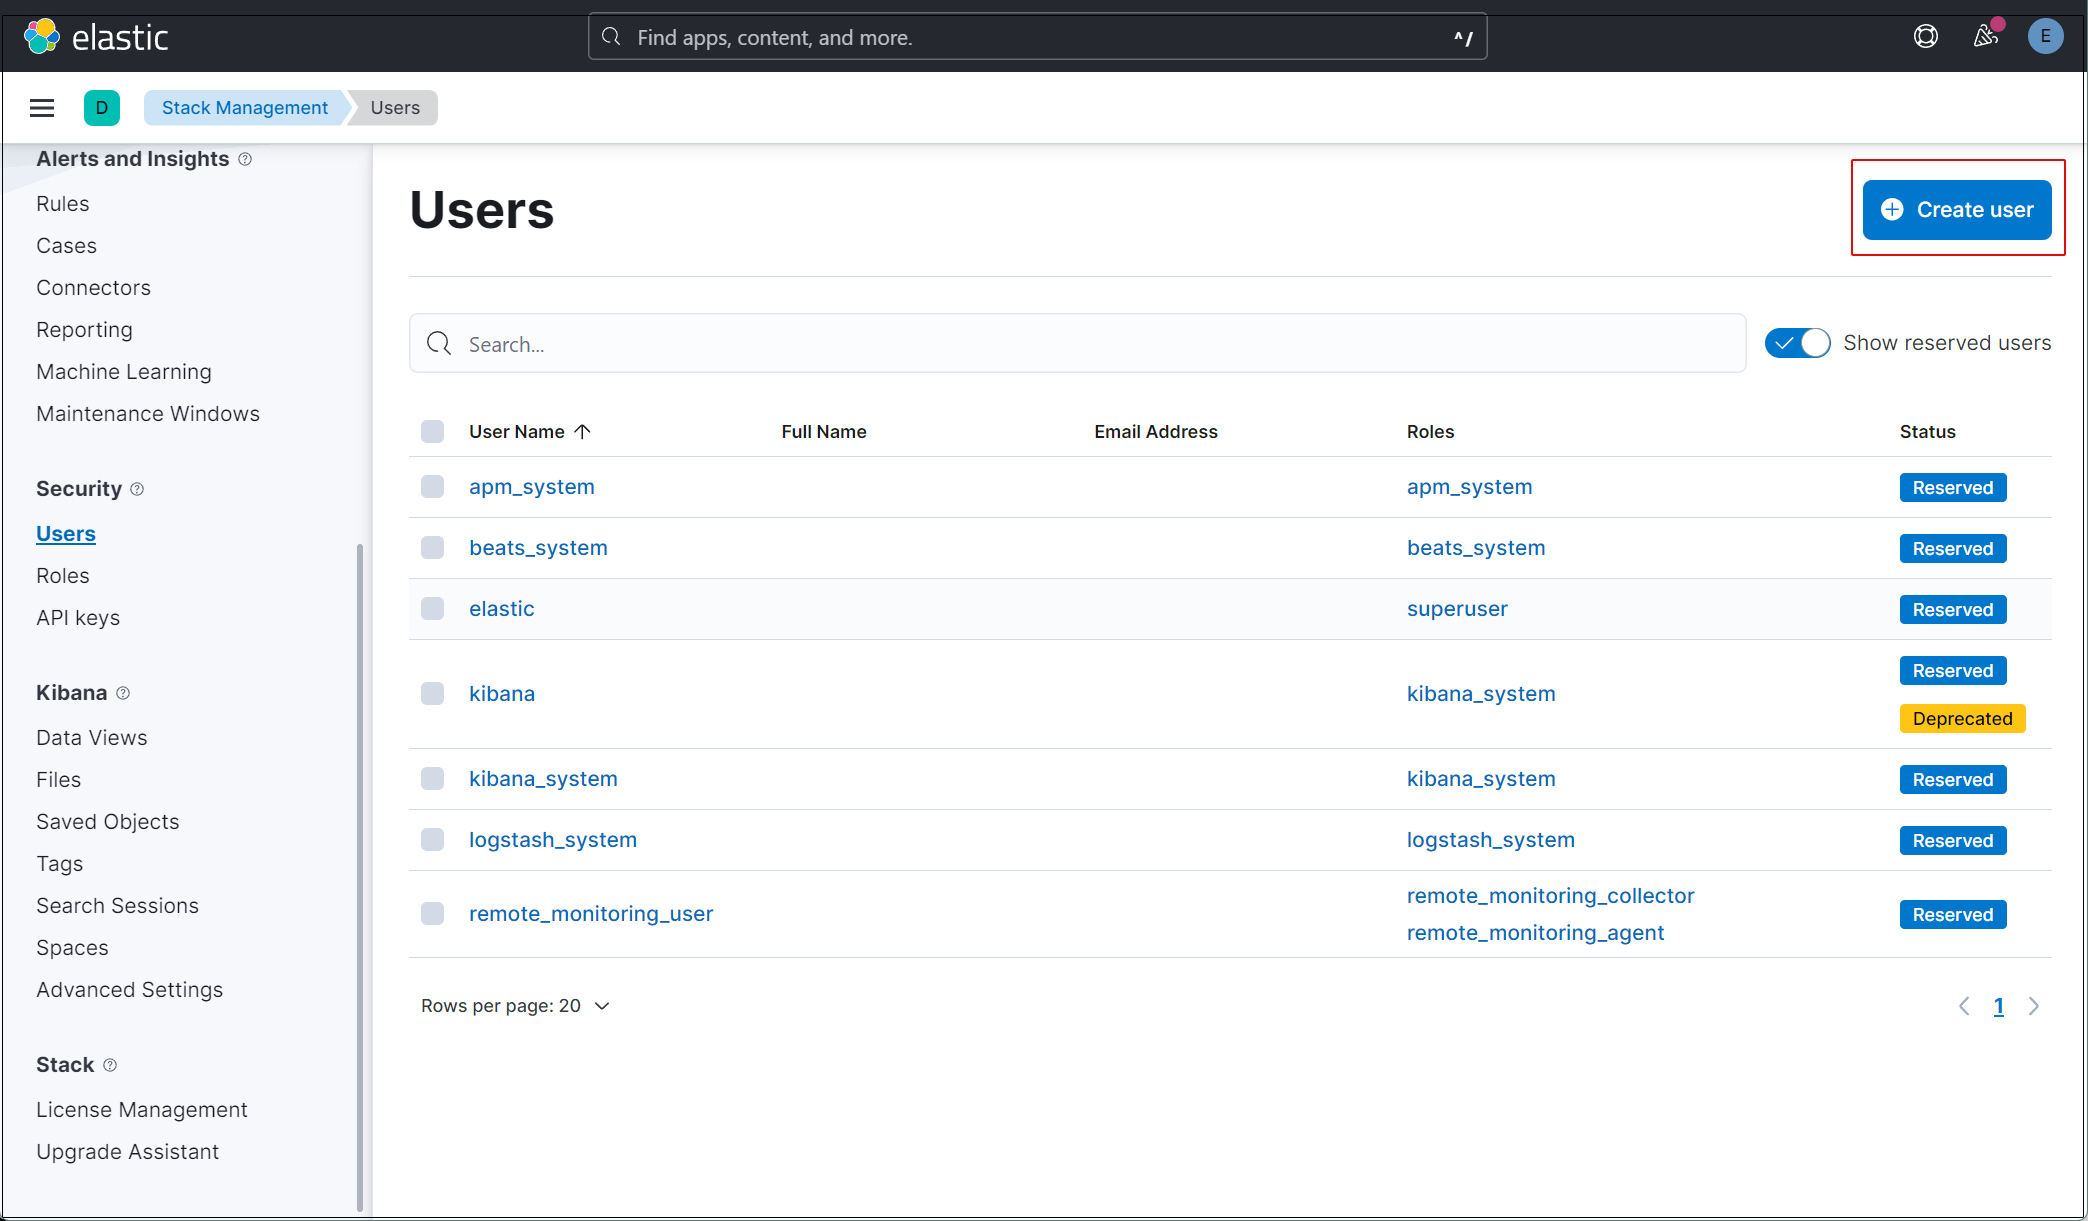
Click the "Create user" button in the upper right corner.
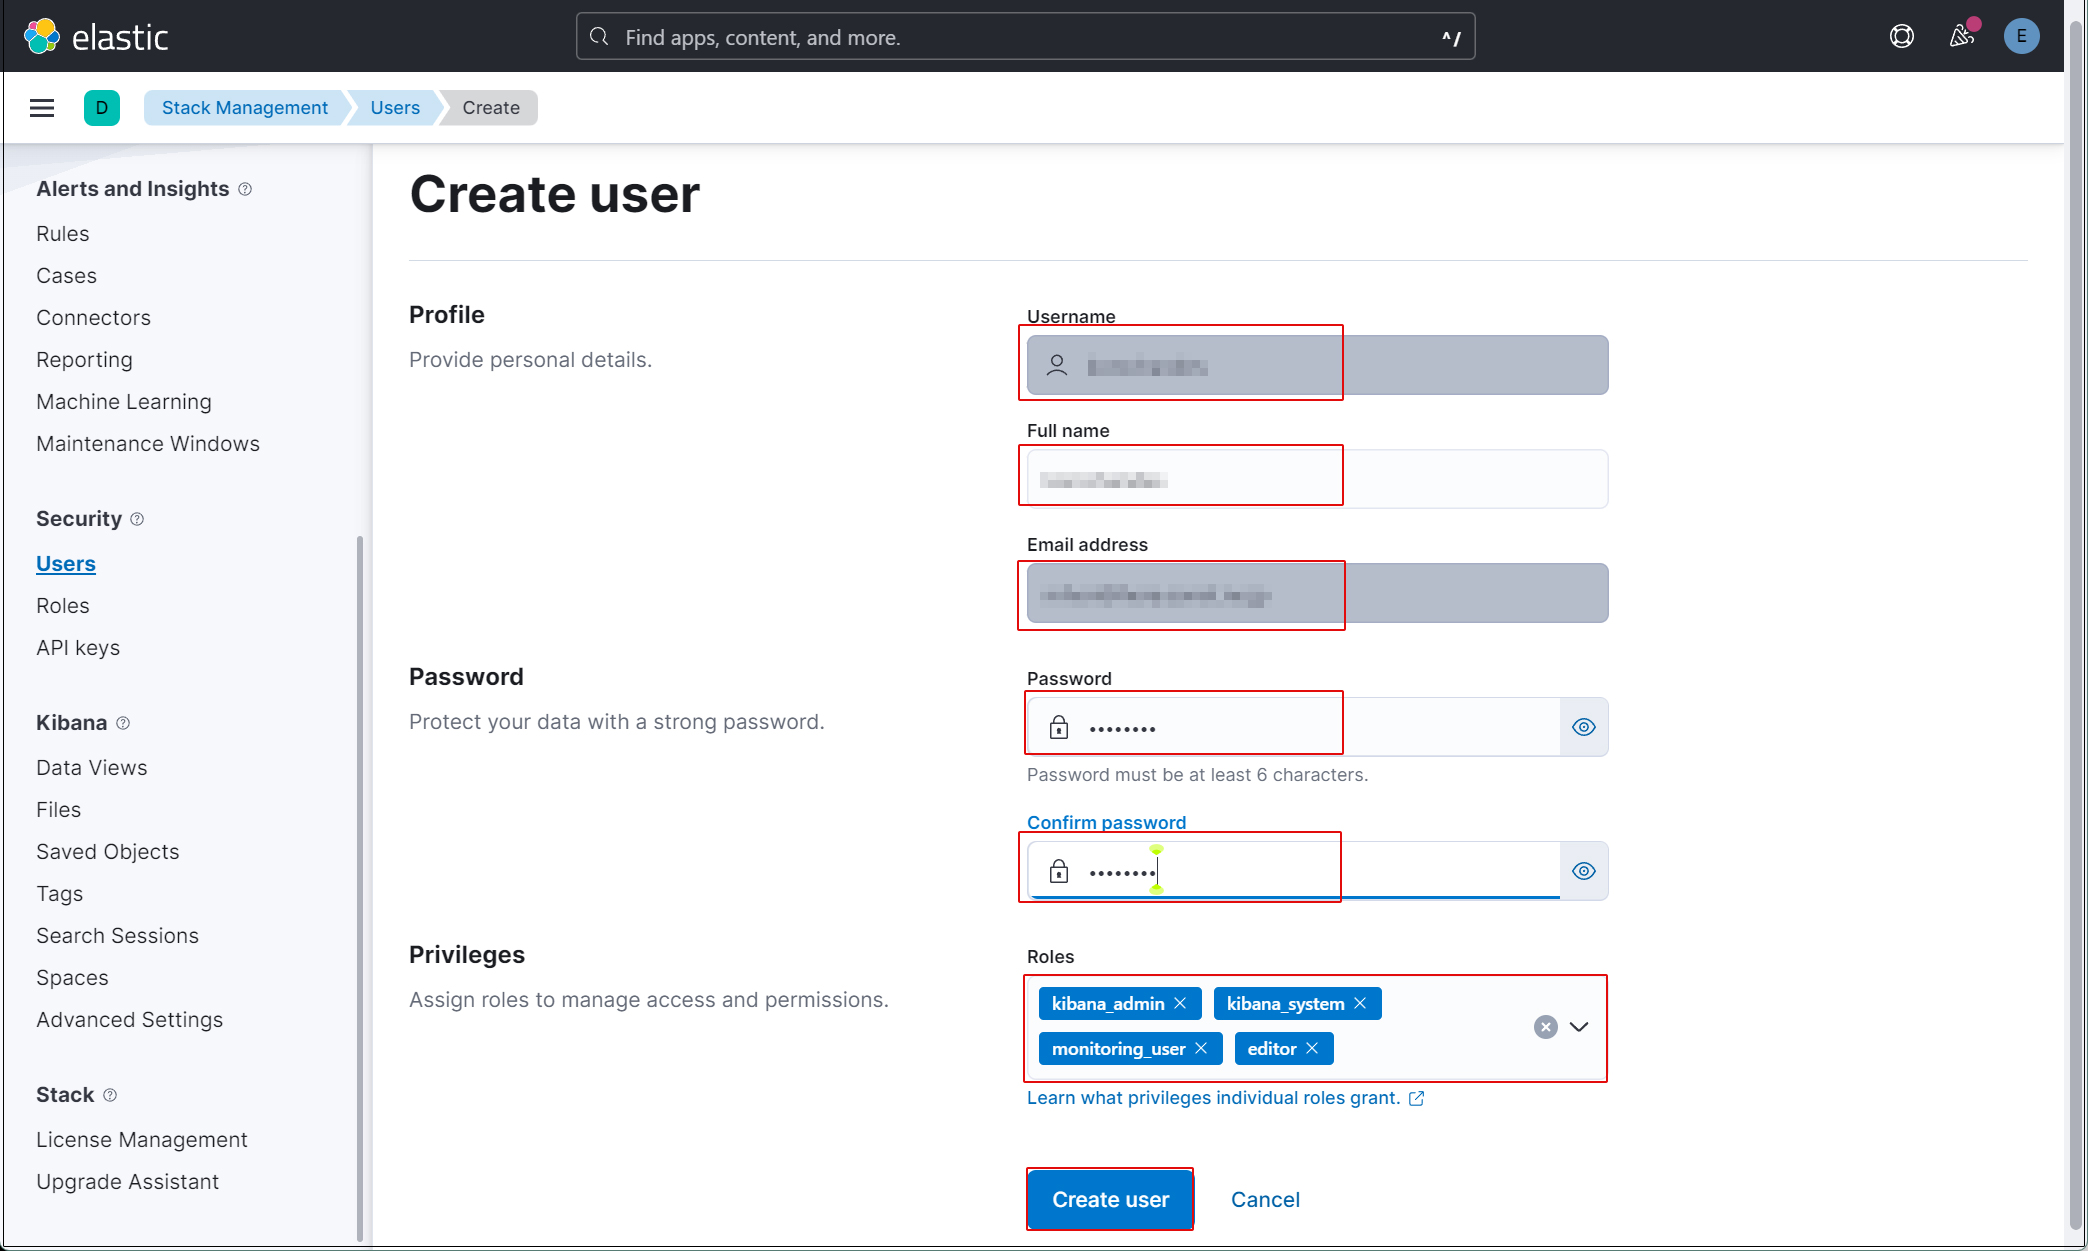
Enter new user information and assign the kibana_admin, kibana_system, monitoring_user, and editor roles under Privileges.
Finally, click [Create user].
Log out of the current profile and verify that you can log in with the newly created user account.
Currently, there is no data available to display in Kibana because Filebeat and Auditbeat are not configured on the SURICATA host.
Install Filebeat on the SURICATA server
This task will be performed on the first Fedora45 Server(IP:192.168.11.83) where Suricata has been installed.
1. Filebeat Install
1.1 Download Elastic GPG Key
# rpm --import https://artifacts.elastic.co/GPG-KEY-elasticsearch
1.2 Create an elasticsearch.repo file in the /etc/yum/yum.repos.d directory with the following content:
# vi /etc/yum.repos.d/elasticsearch.repo

The following content is described
[elasticsearch]
name=Elasticsearch repository for 9.x packages
baseurl=https://artifacts.elastic.co/packages/9.x/yum
gpgcheck=1
gpgkey=https://artifacts.elastic.co/GPG-KEY-elasticsearch
enabled=0
autorefresh=1
type=rpm-md
1.3 Filebeat Install
# dnf -y install --enablerepo=elasticsearch filebeat
1.4 Creating an Elasticsearch CA Certificate
Download the Elasticsearch CA certificate and save it to any directory (in this case, save it as /etc/filebeat/elastic-ca.crt).
※Keep port 9200 open on the second server (the server running Fedora45 with Elasticsearch installed).
# openssl s_client -connect 192.168.11.85:9200 \
-showcerts </dev/null 2>/dev/null | \
openssl x509 -outform PEM > /etc/filebeat/elastic-ca.crt
1.5 Configure Filebeat to connect to Elasticsearch and Kibana
# vi /etc/filebeat/filebeat.yml

Below the commented-out line `#host: "localhost:5601"` on line 137, add a line pointing to the private IP address and port of your Kibana instance.
host: "192.168.11.85:5601"

Line 164 : comment out
#hosts: ["localhost:9200"]

Line 165 : Enter the Elastic Stack IP address and Elasticsearch port number.
hosts: ["https://192.168.11.85:9200"]

Line 171 : Uncomments
protocol: "https"

Line 172 : Elasticsearch CA Certificate Specification
ssl.certificate_authorities: ["/etc/filebeat/elastic-ca.crt"]

Line 175,176 : Uncomment the line, leave [username] as the default, and enter the password for the [elastic] user in [password].
username: "elastic"
password: “xxxxxxxxx"
1.6 Configuration File Test
# filebeat test config
Config OK
1.7 Enable the built-in Suricata module in Filebeats
# filebeat modules enable suricata
The above command will change /etc/filebeat/modules.d/suricata.yml.disabled to /etc/filebeat/modules.d/suricata.yml, but the contents remain unchanged. Therefore, edit it as follows:
# vi /etc/filebeat/modules.d/suricata.yml

# Module: suricata
# Docs: https://www.elastic.co/guide/en/beats/filebeat/main/filebeat-module-suricata.html

- module: suricata
  # All logs
  eve:
    enabled: true
    var.paths: ["/var/log/suricata/eve.json"]

    # Set custom paths for the log files. If left empty,
    # Filebeat will choose the paths depending on your OS.
    #var.paths:
1.8 Set up the initial environment
Load the pipeline into the Suricata service
Load the SIEM dashboard into Elasticsearch
# filebeat setup -e

--------------------------------------------------------------------------------
{"log.level":"info","@timestamp":"2026-11-11T19:31:38.495+0900","log.logger":"modules","log.origin":{"function":"github.com/elastic/beats/v7/filebeat/fileset.LoadPipeline","file.name":"fileset/pipelines.go","file.line":134},"message":"Elasticsearch pipeline loaded.","service.name":"filebeat","pipeline":"filebeat-9.5.6-suricata-eve-pipeline","ecs.version":"1.6.0"}
{"log.level":"info","@timestamp":"2026-11-11T19:31:38.540+0900","log.logger":"modules","log.origin":{"function":"github.com/elastic/beats/v7/filebeat/fileset.LoadPipeline","file.name":"fileset/pipelines.go","file.line":134},"message":"Elasticsearch pipeline loaded.","service.name":"filebeat","pipeline":"filebeat-9.5.6-suricata-eve-dns","ecs.version":"1.6.0"}
{"log.level":"info","@timestamp":"2026-11-11T19:31:38.570+0900","log.logger":"modules","log.origin":{"function":"github.com/elastic/beats/v7/filebeat/fileset.LoadPipeline","file.name":"fileset/pipelines.go","file.line":134},"message":"Elasticsearch pipeline loaded.","service.name":"filebeat","pipeline":"filebeat-9.5.6-suricata-eve-dns-answer-v1","ecs.version":"1.6.0"}
{"log.level":"info","@timestamp":"2026-11-11T19:31:38.599+0900","log.logger":"modules","log.origin":{"function":"github.com/elastic/beats/v7/filebeat/fileset.LoadPipeline","file.name":"fileset/pipelines.go","file.line":134},"message":"Elasticsearch pipeline loaded.","service.name":"filebeat","pipeline":"filebeat-9.5.6-suricata-eve-dns-answer-v2","ecs.version":"1.6.0"}
{"log.level":"info","@timestamp":"2026-11-11T19:31:38.632+0900","log.logger":"modules","log.origin":{"function":"github.com/elastic/beats/v7/filebeat/fileset.LoadPipeline","file.name":"fileset/pipelines.go","file.line":134},"message":"Elasticsearch pipeline loaded.","service.name":"filebeat","pipeline":"filebeat-9.5.6-suricata-eve-tls","ecs.version":"1.6.0"}
{"log.level":"info","@timestamp":"2026-11-11T19:31:38.664+0900","log.logger":"modules","log.origin":{"function":"github.com/elastic/beats/v7/filebeat/fileset.LoadPipeline","file.name":"fileset/pipelines.go","file.line":134},"message":"Elasticsearch pipeline loaded.","service.name":"filebeat","pipeline":"filebeat-9.5.6-suricata-eve-http","ecs.version":"1.6.0"}
1.9 Start the Filebeat service
# systemctl start filebeat.service
2. Check in Kibana
Log back into Kibana using the user you created. Accsses http://192.168.11.85:5601
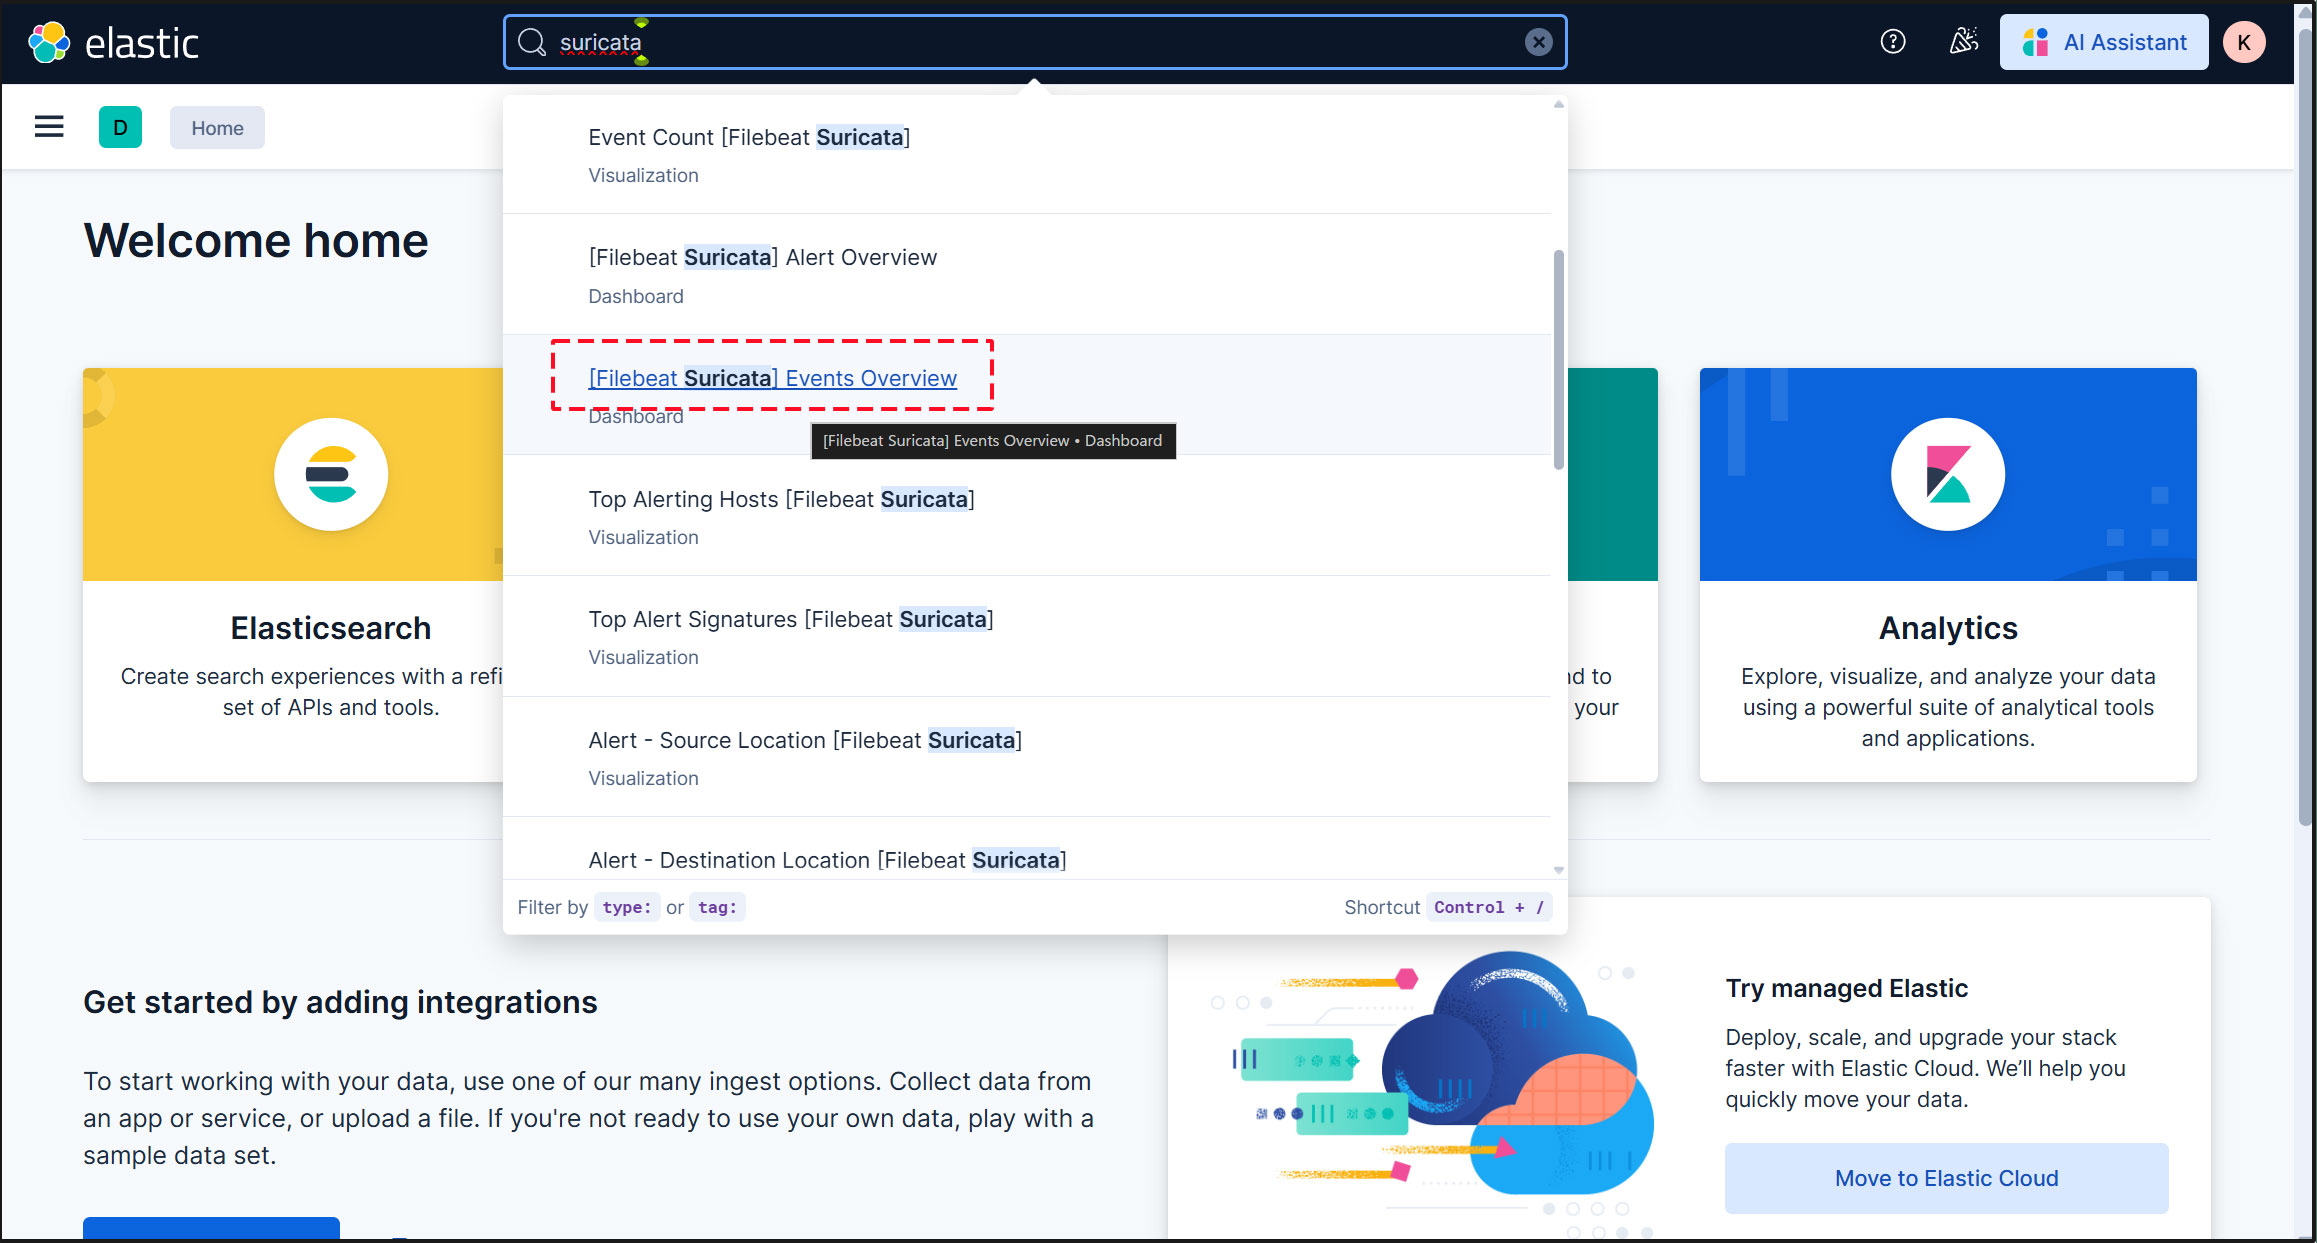
Type "Suricata Events Overview" into the top search field, then click [Filebeat Suricata] Events Overview
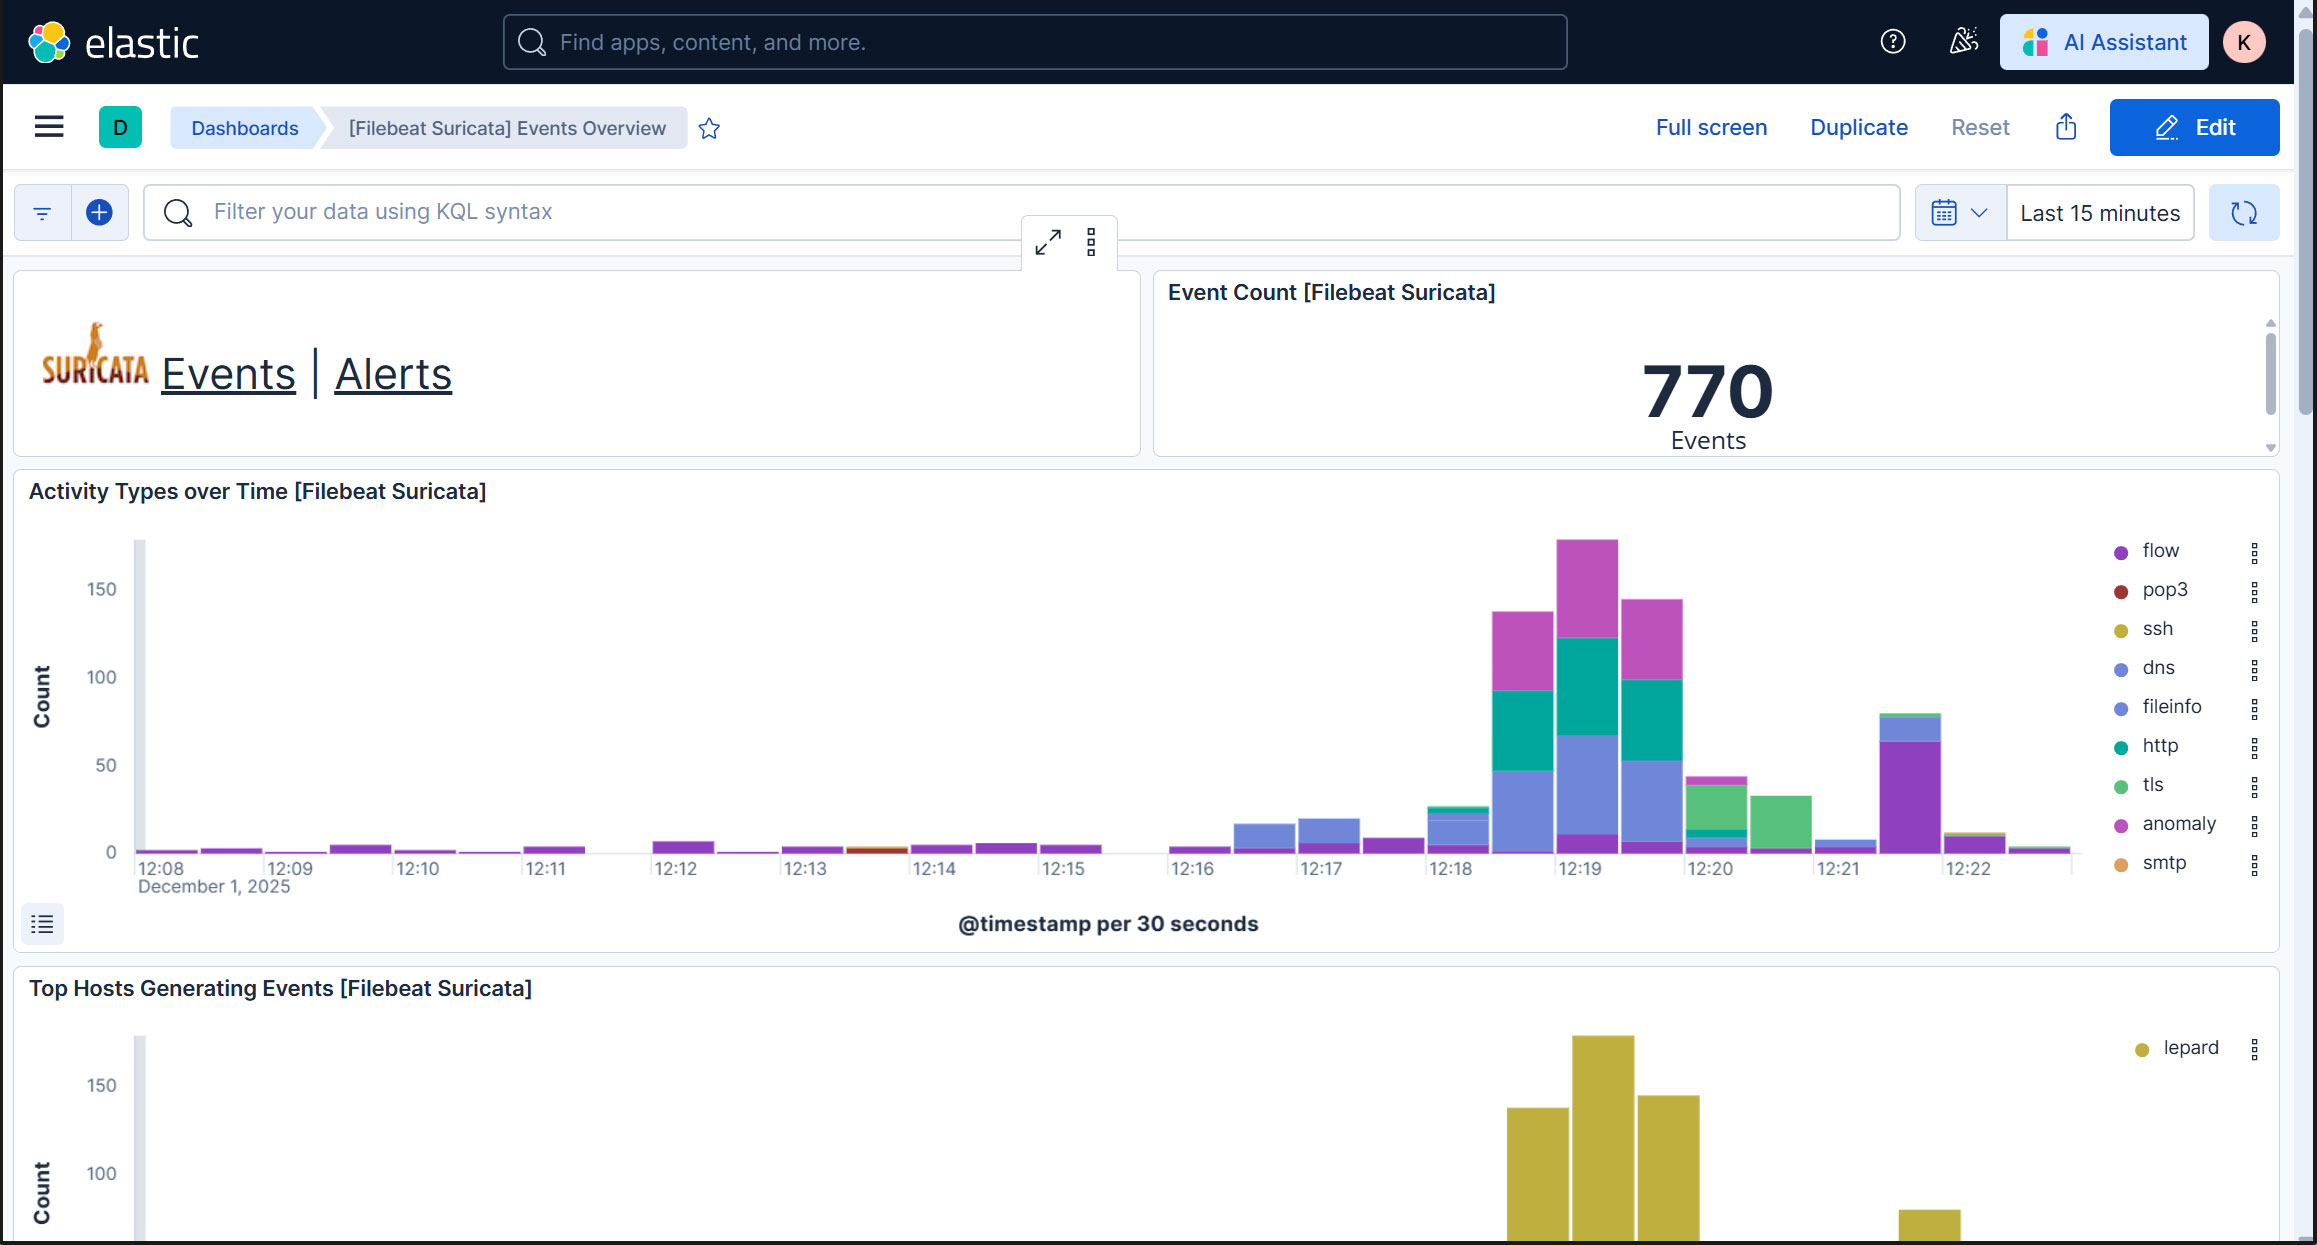
All Suricata events from the past 15 minutes are displayed.
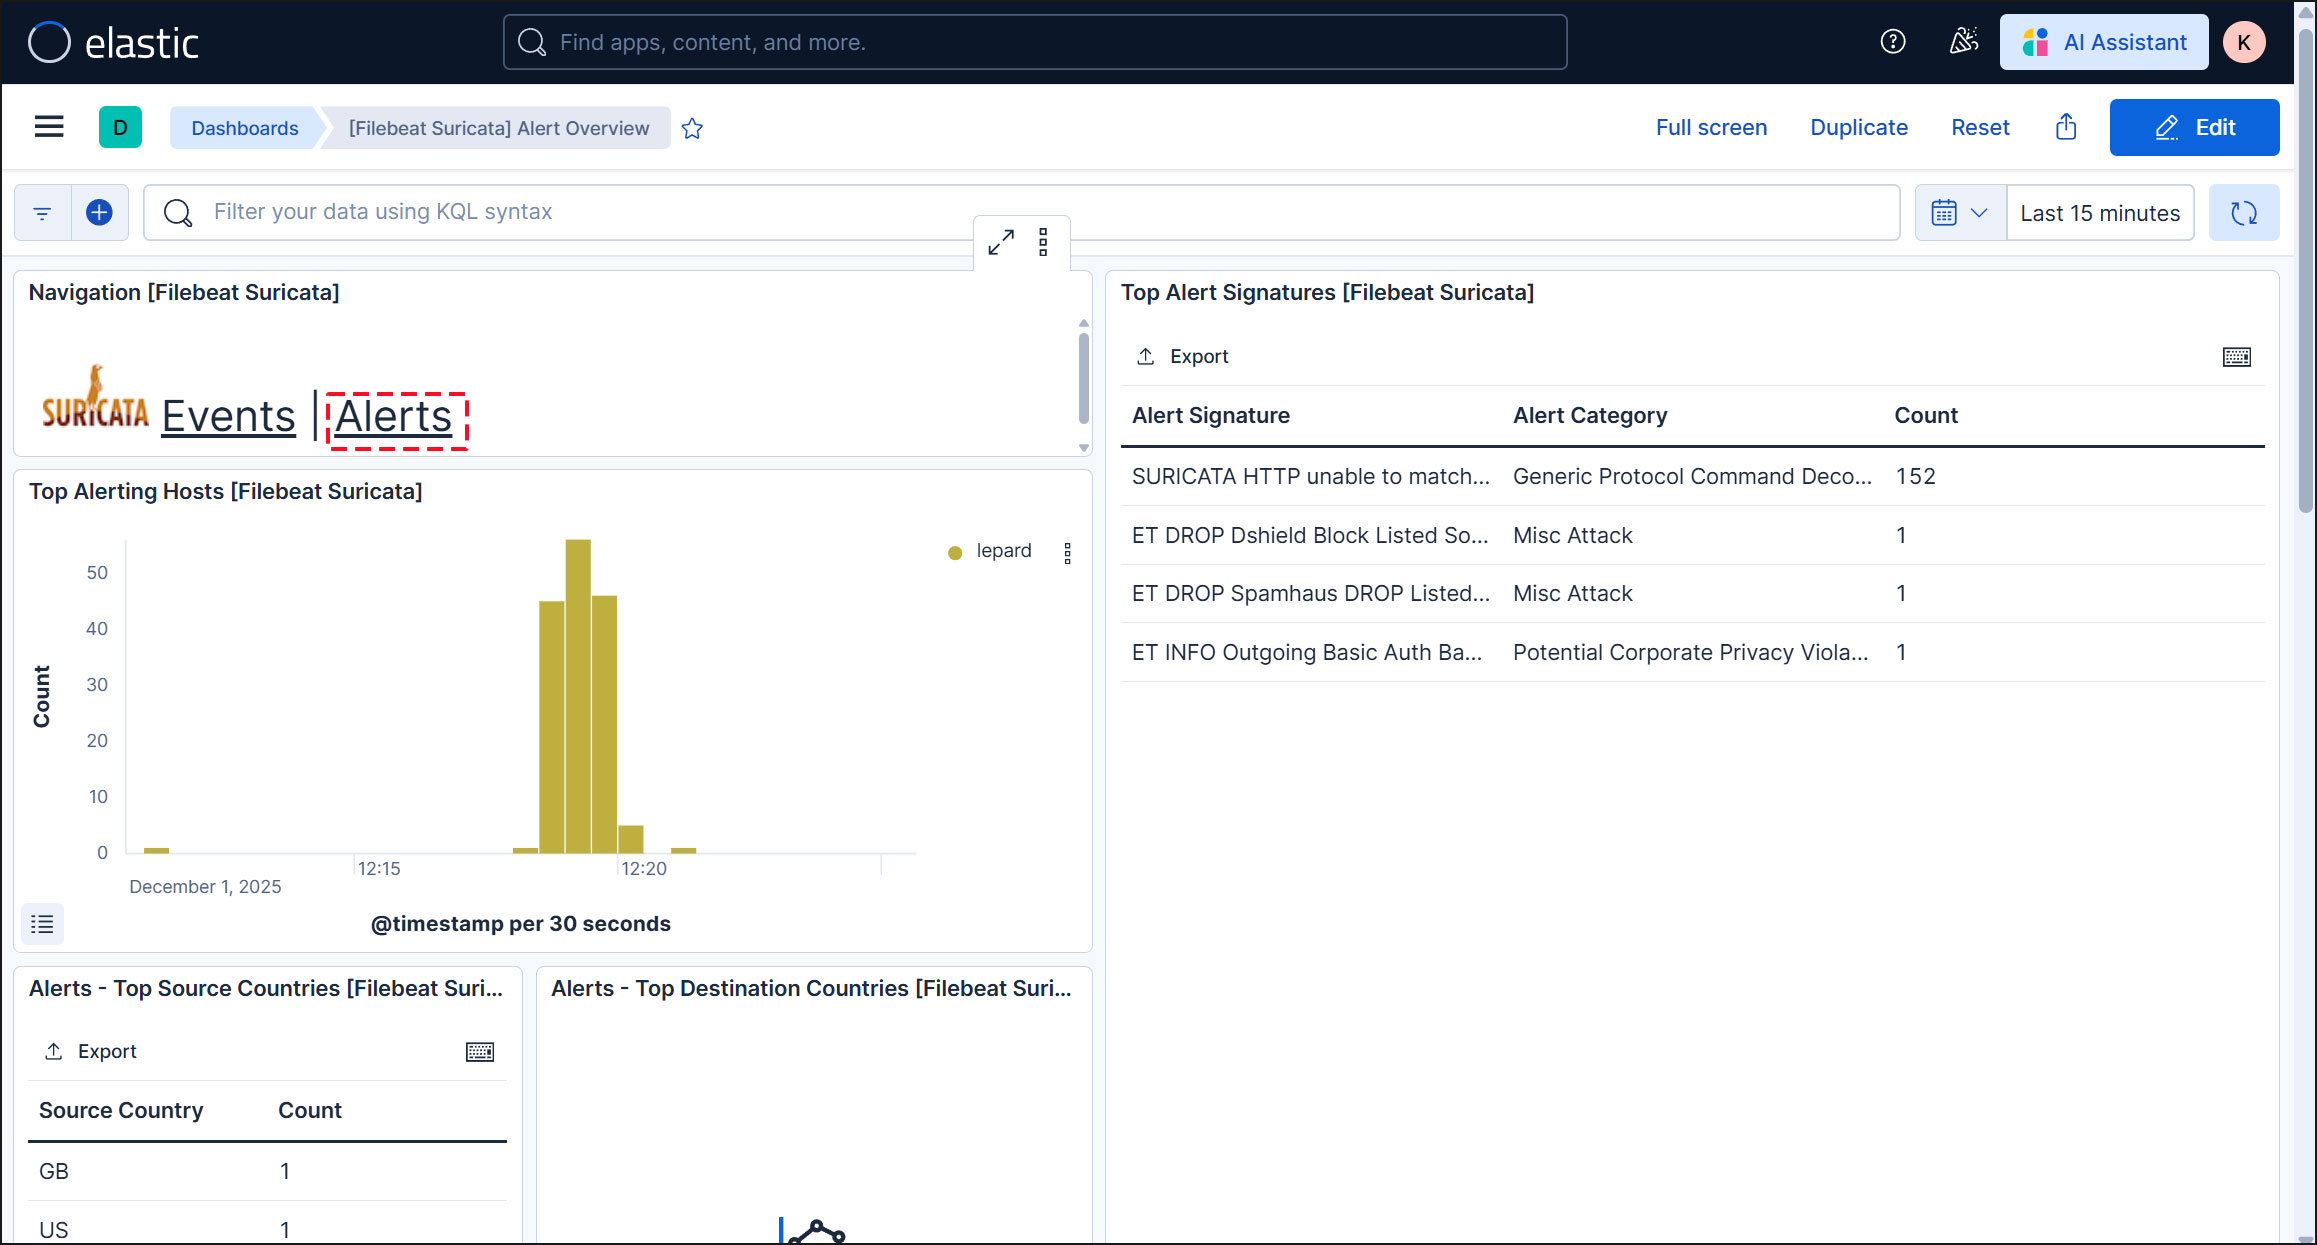
To display alerts for malicious traffic, click the "Alerts" text next to the Suricata logo.
Kibana offers a variety of features and tools for visualizing logs, so feel free to experiment with them.