SSH connection using authentication with public-key cryptography
Creation of public and private key pairs
Create a public/private key pair for a user connecting to the Linux server using OpenSSH.
Use ssh-keygen to create key pairs.
This time, we will create a key set using the RSA cipher used in the SSH protocol Version 2.
Creation of public/private key pairs is performed with remote login user privileges (huong).
If you do not specify the destination and file name, id_ed25519,id_ed25519.pub will be created in /home/huong/.ssh/. On the way, enter the password for the key.
# su - huong
huong@Lepard:~$ ssh-keygen -t ed25519
Generating public/private ed25519 key pair.
Enter file in which to save the key (/home/huong/.ssh/id_ed25519):
Enter passphrase for "/home/huong/.ssh/id_ed25519" (empty for no passphrase):
Enter same passphrase again:
Your identification has been saved in /home/huong/.ssh/id_ed25519
Your public key has been saved in /home/huong/.ssh/id_ed25519.pub
The key fingerprint is:
SHA256:8i8rQxvDTi5SgSgkk95T5V4NKNZL16T/7KhCzVOGGvg huong@Lepard
The key's randomart image is:
+--[ED25519 256]--+
| .    o...o.     |
|+.   +.+ .+.     |
|+o..o +.oo..     |
|o..o...o...o     |
|.   .oo.S o.     |
|    . *E +  o    |
|   . =.+. .  o   |
|  . . *...  o    |
|   . . oo+o. .   |
+----[SHA256]-----+
$ cat ~/.ssh/id_ed25519.pub >> ~/.ssh/authorized_keys
$ chmod 600 ~/.ssh/authorized_keys
$ chmod 700 ~/.ssh/
Save the generated private key id_ed25519 to the Windows directory c:\USERS\user\.ssh\ using winSCP
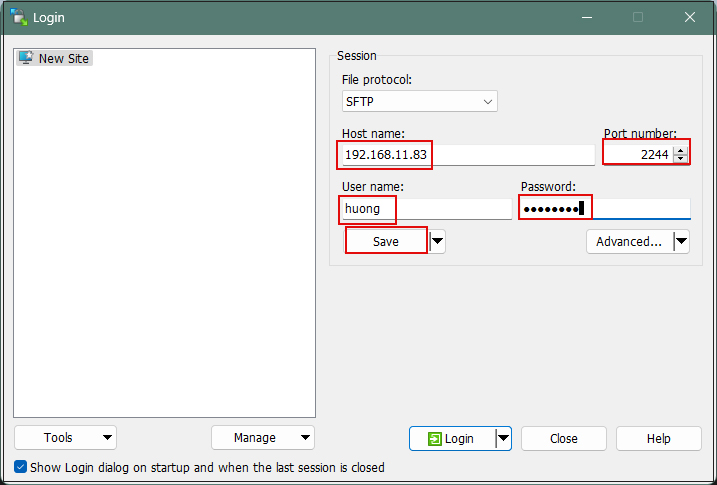
Start Winscp
Host name : Server IP Address
Port number : SSH Port
User name : Server Login User
Password : Password for the same user
and then "Save".
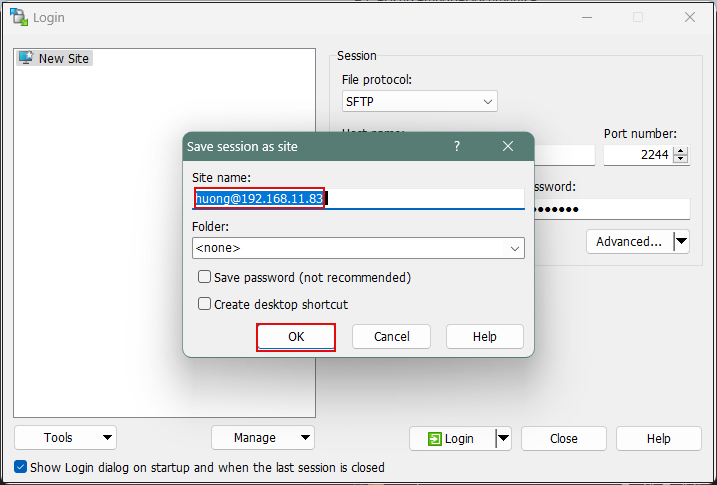
Site name : Any name
Click "OK"
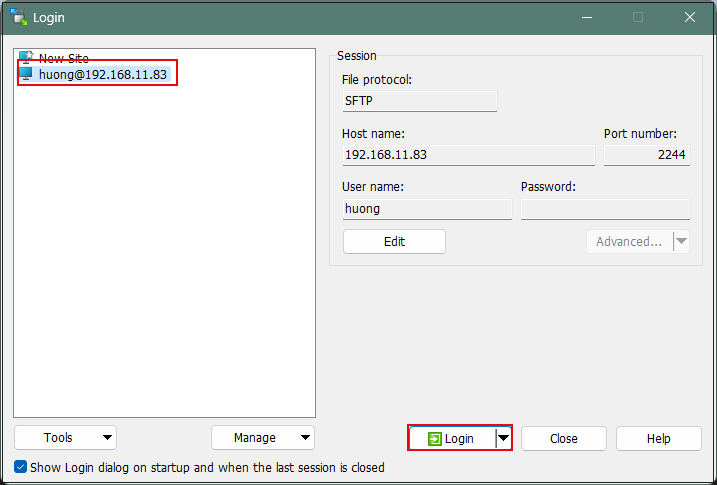
After confirming the server, click "Login".
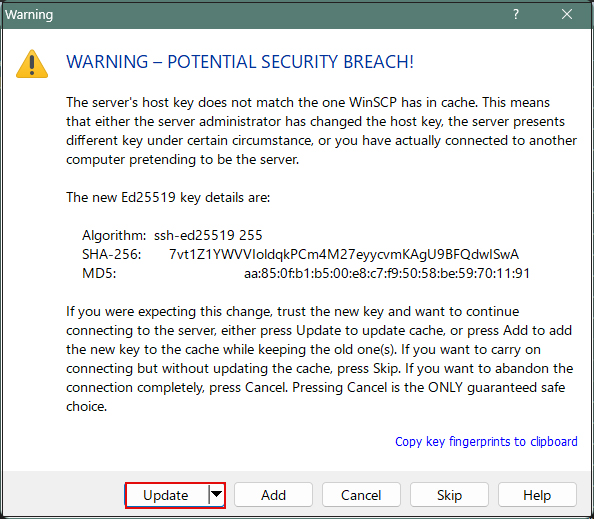
Click "Update" when the following screen appears
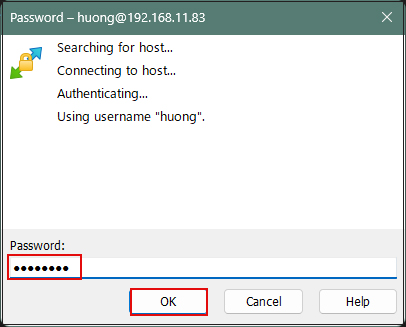
Password of the logged-in user in the Password field
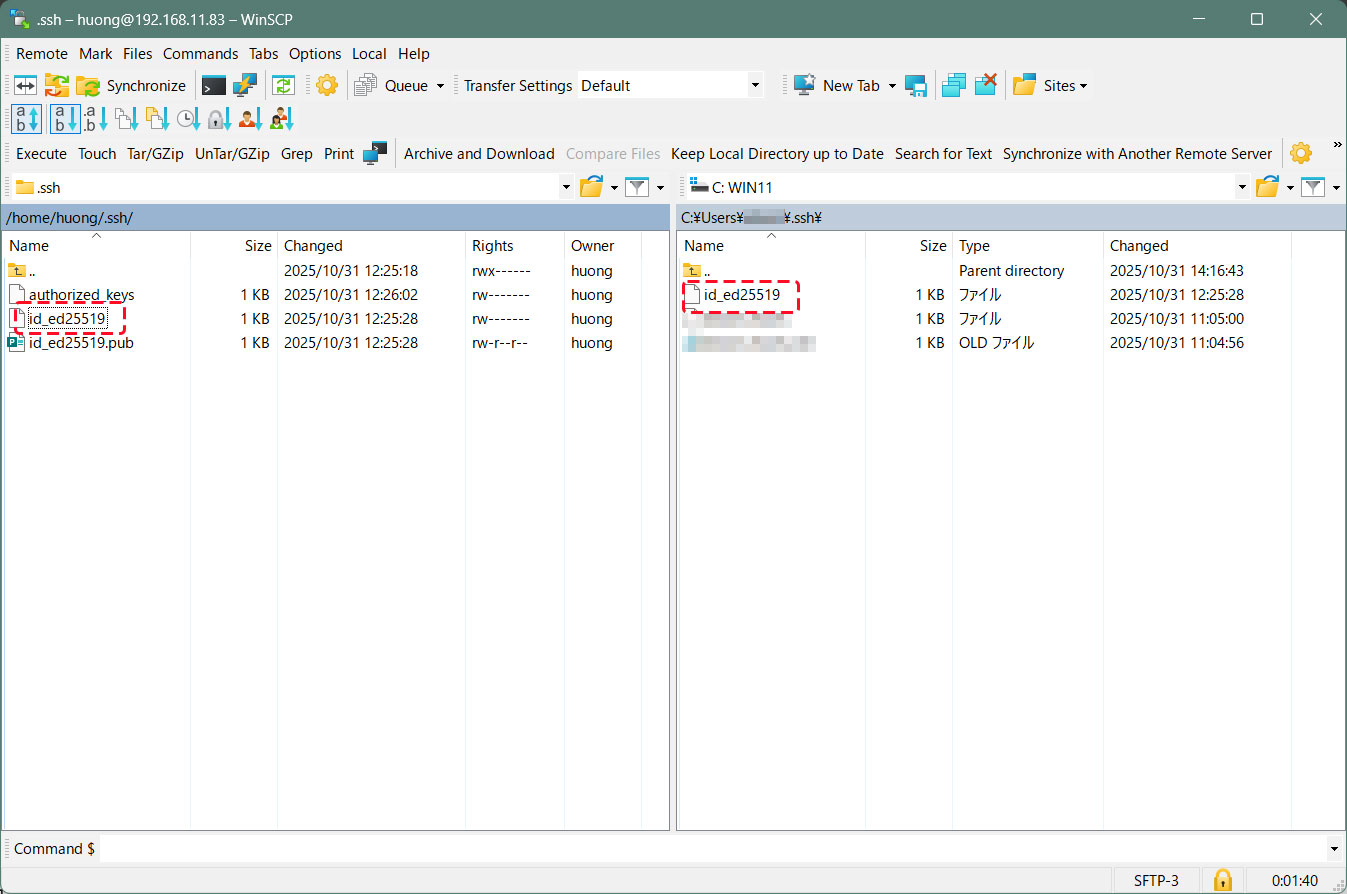
Once connected, the left pane shows the server side, and the right pane shows the PC (Windows) side.
Copy the "id_ed25519" file located in the .ssh directory to the Windows directory[c:\USERS\user\.ssh] on the right side.
Editing SSH Configuration File
Edit the SSH configuration file to disable password authentication.
This time, instead of being an ordinary user, su - to become root.
$ su -
Password:

# vi /etc/ssh/sshd_config
# Around the 80th line: Uncommented and changed password authentication to non-authenticated
PasswordAuthentication no

# systemctl restart ssh
How to connect using Tabby Terminal
Specify the key using the option [-i c:\USERS\xxxxx\.ssh\id_ed25519]
C:\Users\xxxxx>ssh huong@192.168.11.83 -p 2244 -i c:\USERS\xxxxx\.ssh\id_ed25519
Enter passphrase for key 'c:\USERS\xxxxx\.ssh\id_ed25519':[The password created when generating the public key]
Welcome to Ubuntu 26.10 (GNU/Linux 7.3.0-9-generic x86_64)
* Documentation: https://docs.ubuntu.com
* Management: https://landscape.canonical.com
* Support: https://ubuntu.com/pro System information as of Fri Oct 16 10:54:55 AM JST 2026
System load: 0.0 Processes: 235
Usage of /: 38.1% of 18.01GB Users logged in: 0
Memory usage: 16% IPv4 address for ens33: 192.168.11.83
Swap usage: 0%
0 updates can be applied immediately.
Creating a private key using PuTTYgen
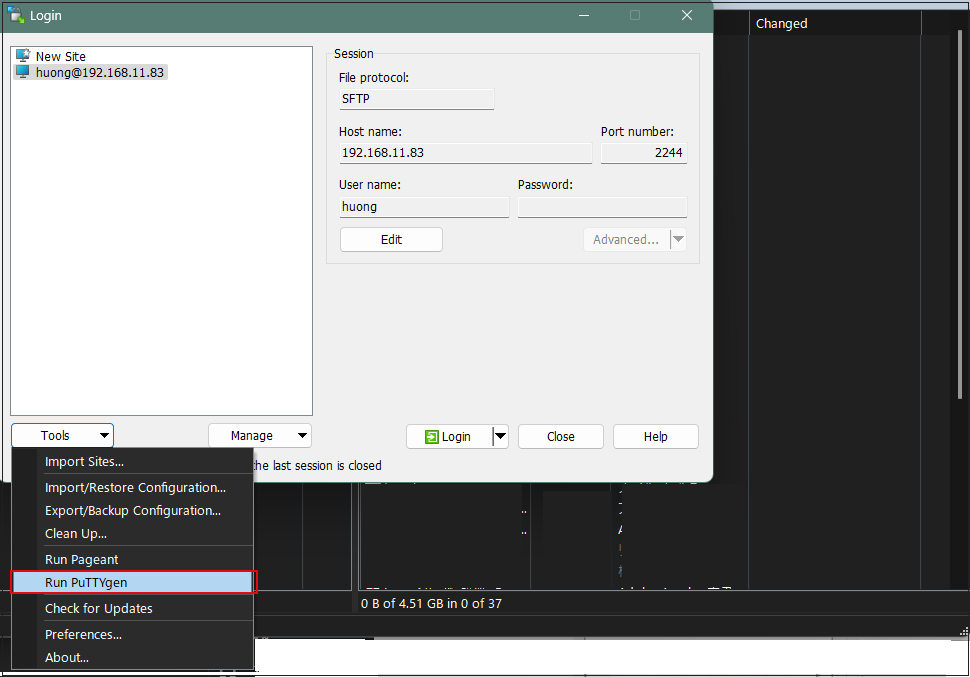
Launch WinSCP, select the relevant server, and then click [Run PuTTYgen] under "Tools."
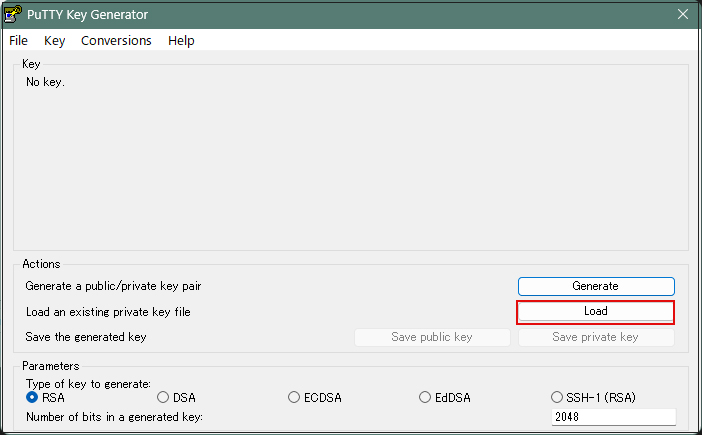
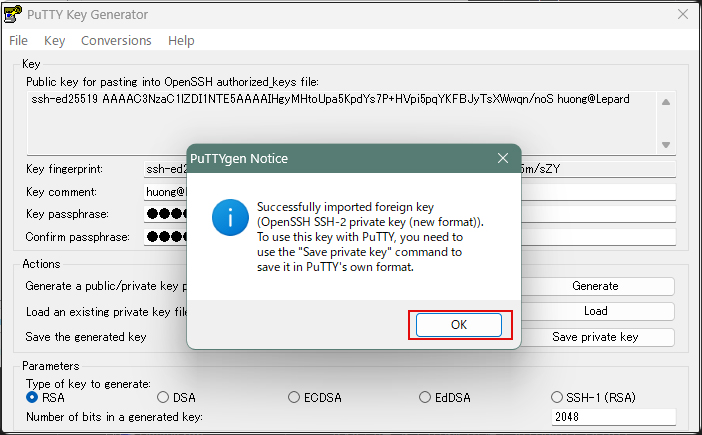
Click Load
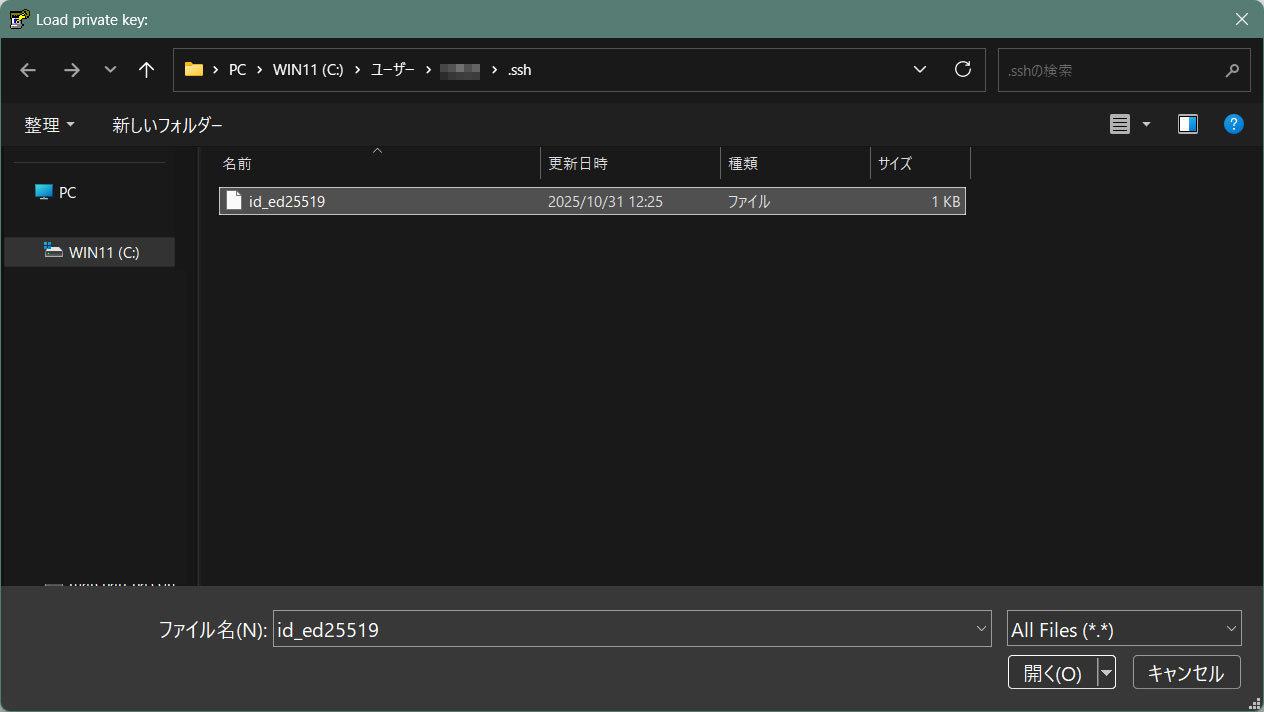
The [ Open File Dialog ] will open, change the file type to [ All Files (. Change the file type to [ All Files (. *) ] and load the private key id_ed25519 that was transferred from the Linux server.
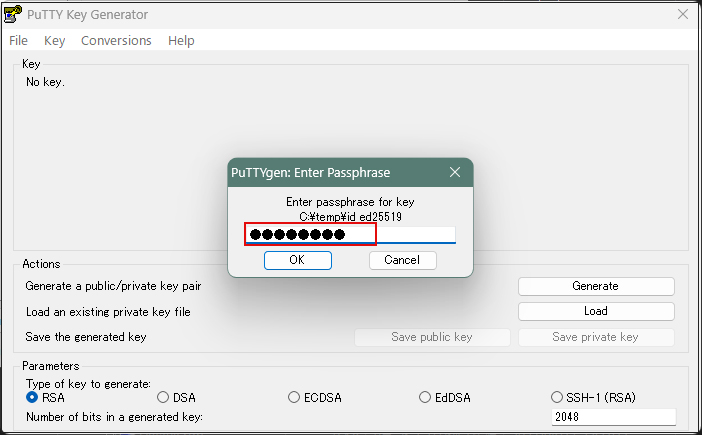
The password is the password set in "Creating a public and private key pair" above
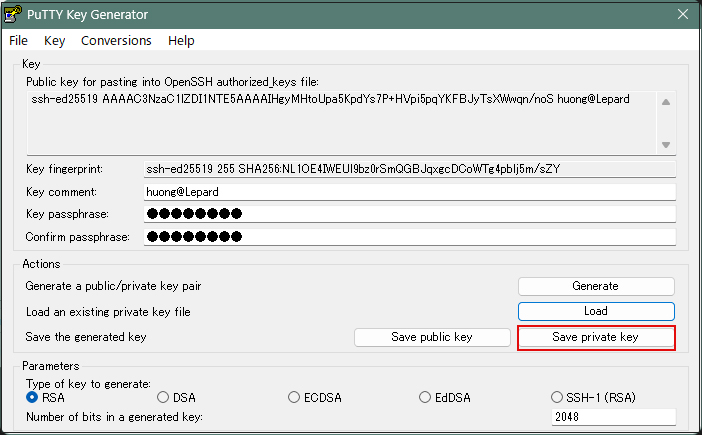
Click on "Save private key"
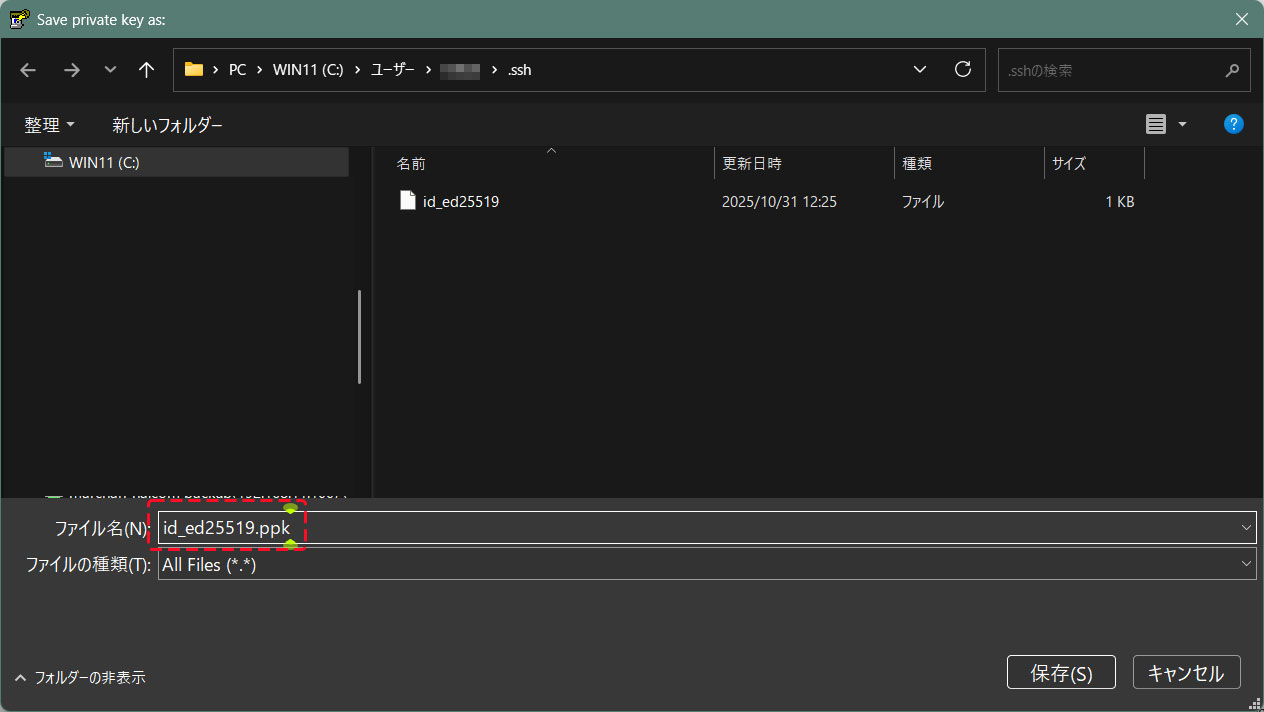
Save the file with the extension ".ppk" in the same place as "id_ed25519" saved earlier on the Windows side under the name "id_ed25519.ppk".
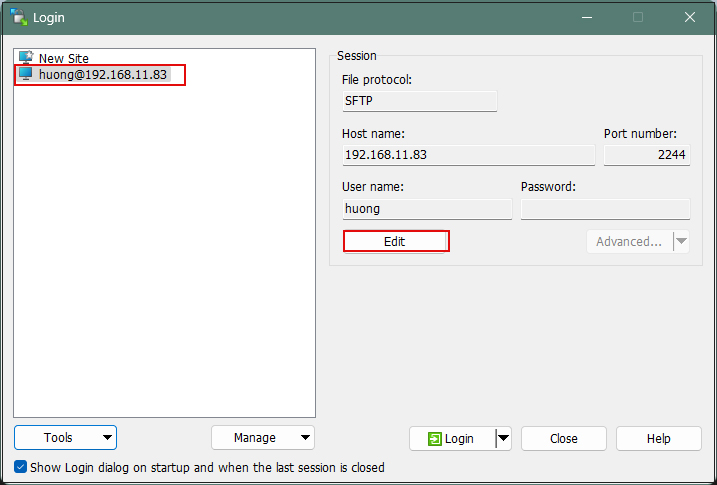
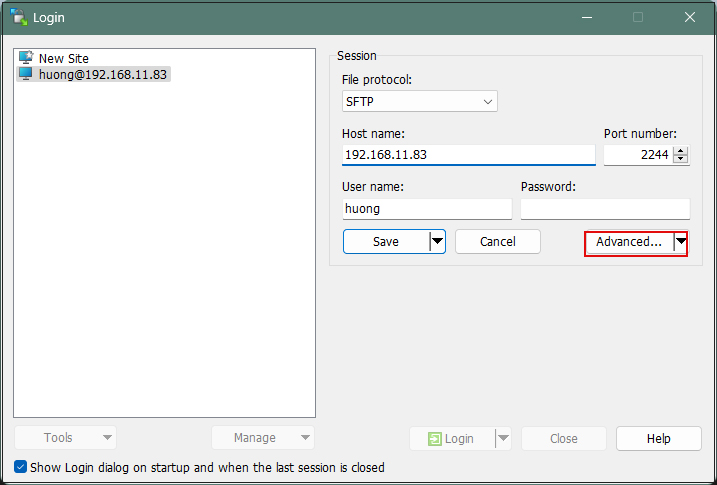
Select the target server and click "Edit".
Click on "Advanced"
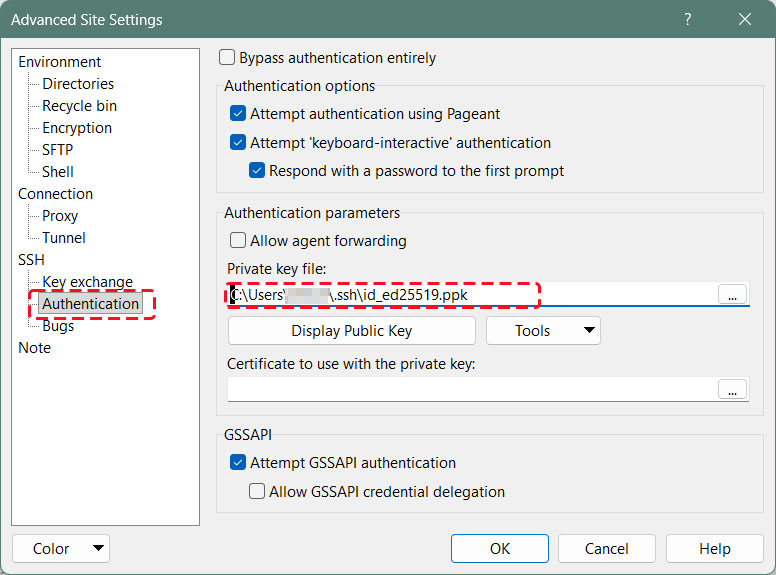
Open the "Authentication" menu and specify "id_ed25519.ppk" saved in Windows for "Private key file
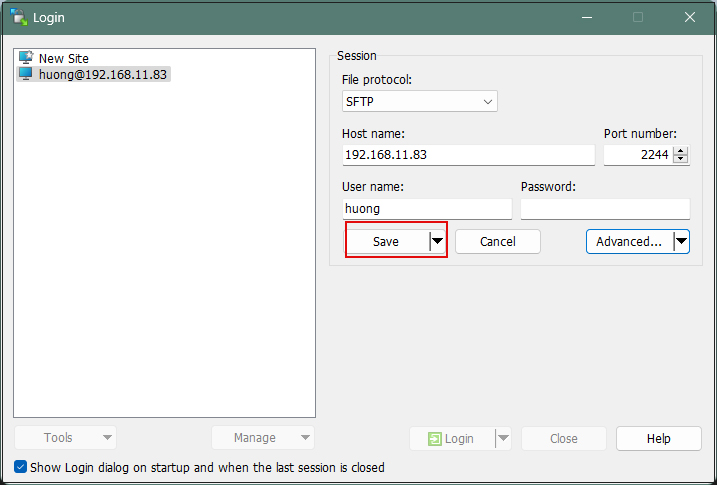
Click "Save"
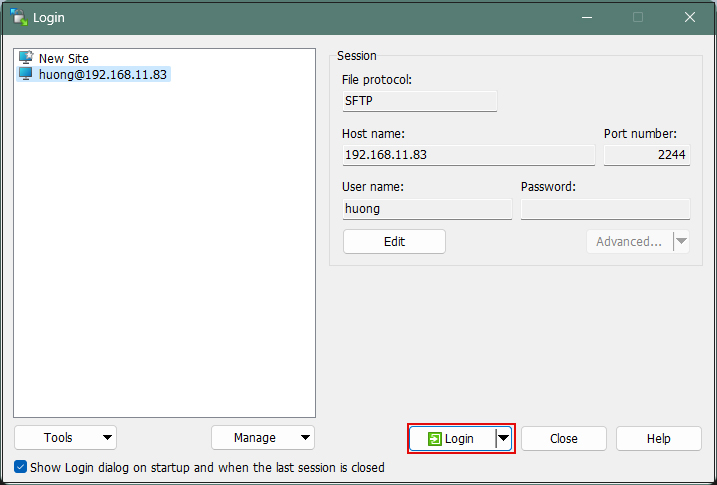
Click on "Login"
The password is the password set in "Creating a public and private key pair" above
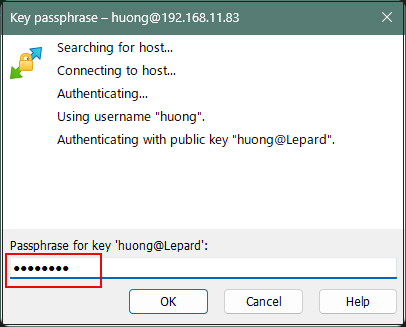
When connecting via Tabby Terminal, do the following:
C:\Users\xxxxx>ssh huong@192.168.11.83 -p 2244 -i c:\USERS\xxxxx\.ssh\id_ed25519.ppk
Enter passphrase for key 'c:\USERS\xxxxx\.ssh\id_ed25519.ppk': ←The password specified when creating the public key
If you encounter an error like the one below, convert your private key to OpenSSH format.
C:\Users\xxxxx>ssh huong@192.168.11.83 -p 2244 -i c:\USERS\xxxxx\.ssh\id_ed25519.ppk
Load key "c:\USERS\xxxxx\.ssh\id_ed25519.ppk": invalid format
huong@192.168.11.83: Permission denied (publickey,gssapi-keyex,gssapi-with-mic).
Launch [WinSCP] > [Run PuTTygen], then import the private key under [Import key] in the [Conversions] tab.
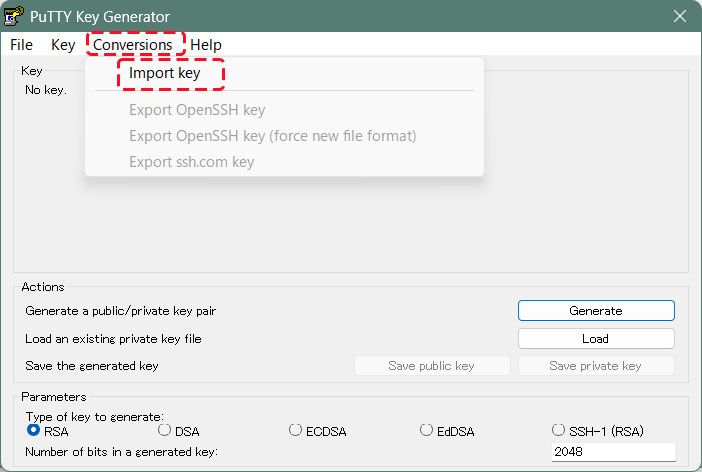
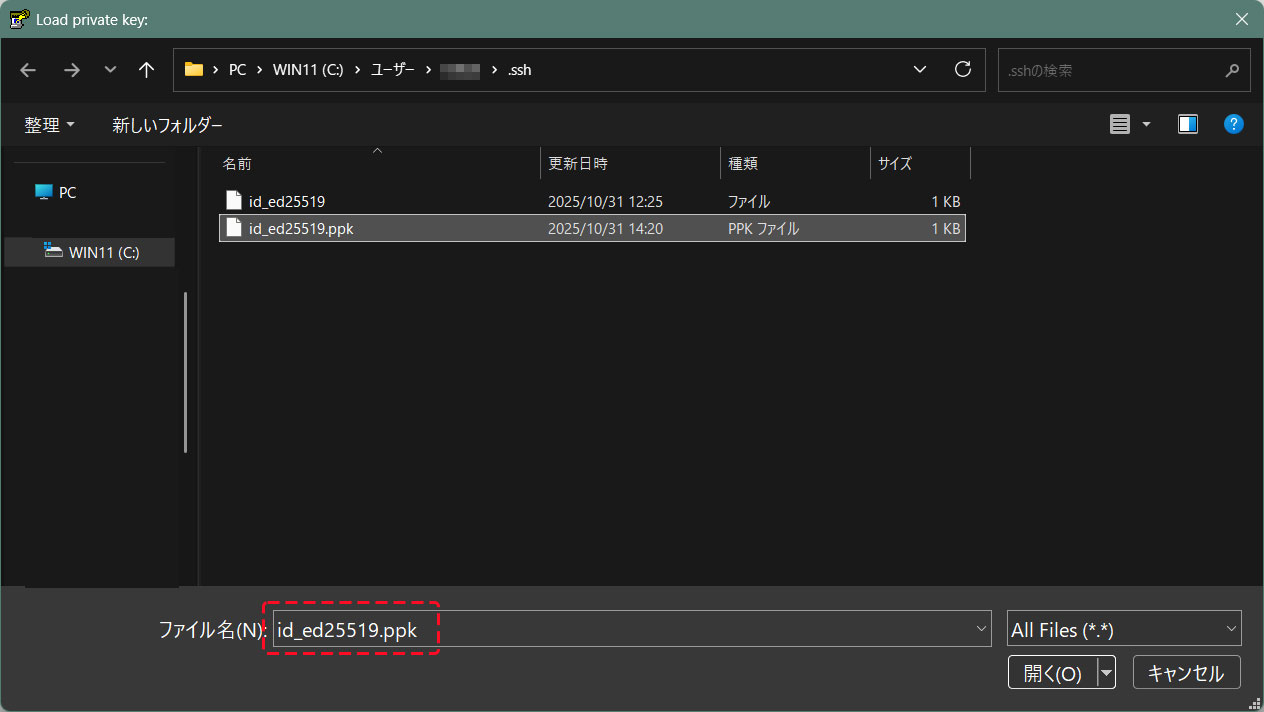
Convert the imported private key to OpenSSH format and save it under a different name
The password specified when creating the public key
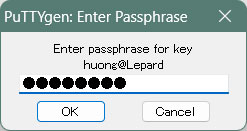
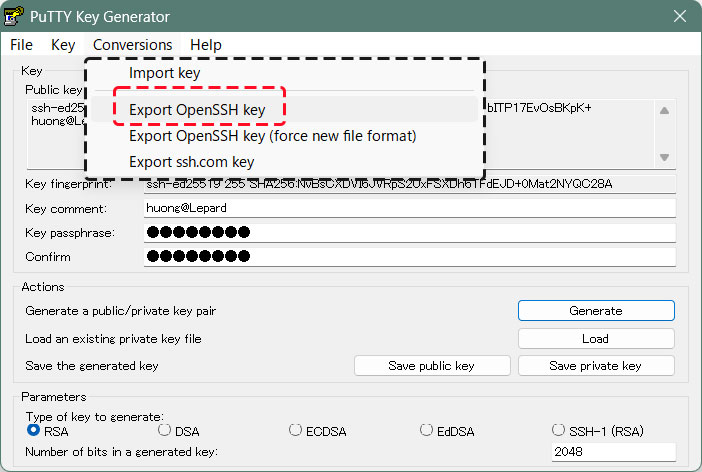
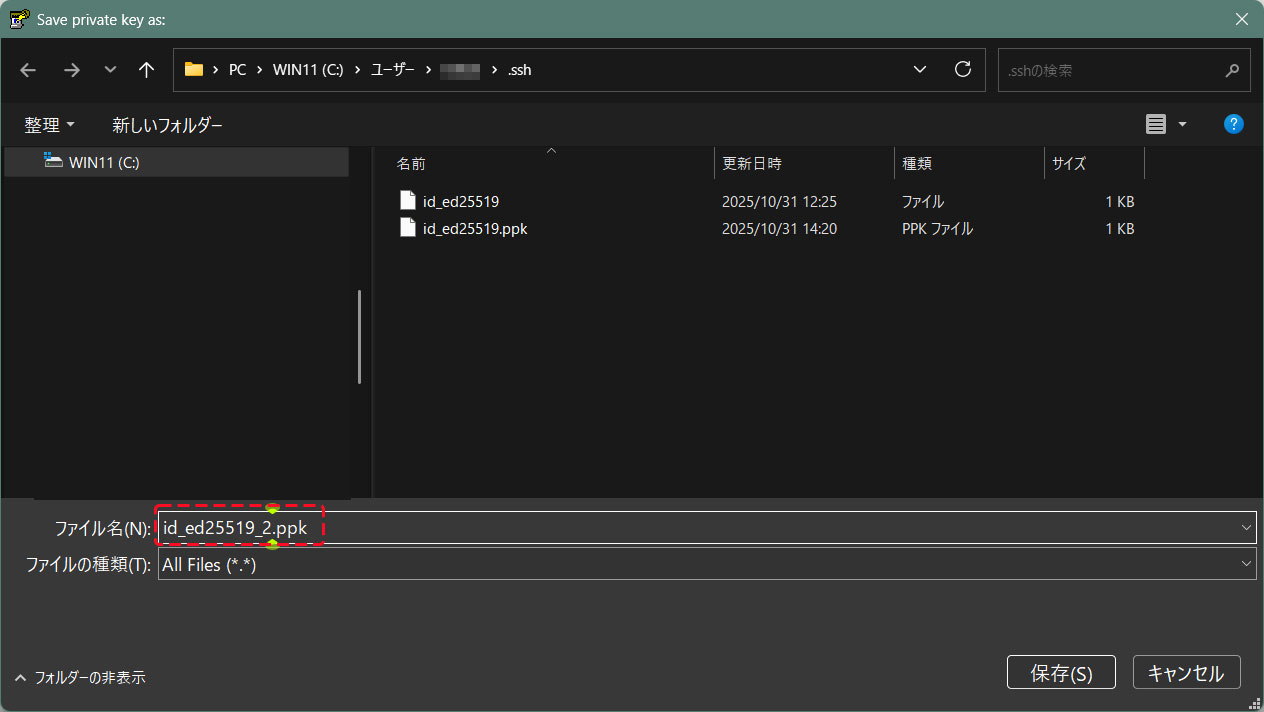
Using the [id_ed25519_2.ppk] file converted to OpenSSH format, you can connect as follows:
C:\Users\xxxxx>ssh huong@192.168.11.83 -p 2244 -i c:\USERS\xxxxx\.ssh\id_ed25519_2.ppk
Enter passphrase for key 'c:\USERS\xxxxx\.ssh\id_ed25519_2.ppk': ←The password specified when creating the public key
Welcome to Ubuntu 26.10 (GNU/Linux 7.3.0-9-generic x86_64)
* Documentation: https://docs.ubuntu.com
* Management: https://landscape.canonical.com
* Support: https://ubuntu.com/pro
System information as of Fri Oct 16 11:09:37 AM JST 2026
System load: 0.0 Processes: 241
Usage of /: 38.1% of 18.01GB Users logged in: 0
Memory usage: 17% IPv4 address for ens33: 192.168.11.83
Swap usage: 0%
0 updates can be applied immediately.