1.SSL証明書を取得する ( Let's Encrypt )
最新のopen sslをインストールしておく
# dnf -y install openssl-devel
1.1 事前準備
1.パッケージ管理システムSnappyインストール
Let’s EncryptのSSL証明書発行ツール「certbot」は2021年以降は「snap」を利用したインストールが推奨されていますので、まずSnapdをインストールします。(dnfまたはyumでの従来の方法でもインストールできます)
# dnf upgrade
# dnf -y install snapd
メインのスナップ通信ソケットを管理するsystemdユニットを有効化する
# systemctl enable --now snapd.socket
クラシックスナップのサポートを有効にする
# ln -s /var/lib/snapd/snap /snap
バージョン確認
# snap --version
snap          2.77.1-0.fc45
snapd         2.77.1-0.fc45
series        16
fedora        45
kernel        7.2.11-300.fc45.x86_64
architecture  amd6
ログアウトして再度ログインするか、システムを再起動して、snapのパスが正しく更新されていることを確認
2.certbot パッケージインストール
# snap install --classic certbot
certbot 5.9.0 from Certbot Project (certbot-eff✓) installed
/snap/bin/certbotへのシンボリックリンクを作成
# ln -s /snap/bin/certbot /usr/bin/certbot
確認する
# ls -la /usr/bin/certbot
lrwxrwxrwx 1 root root 17 Nov  3 13:17 /usr/bin/certbot -> /snap/bin/certbot

# ls -la /snap/bin/certbot
lrwxrwxrwx 1 root root 13 Nov  3 13:17 /snap/bin/certbot -> /usr/bin/snap
1.2 証明書の取得
# certbot certonly --webroot -w /var/www/html/[FQDN] -d [FQDN]
初回のみメールアドレスの登録と利用条件への同意が必要
受信可能なメールアドレスを指定
Saving debug log to /var/log/letsencrypt/letsencrypt.log
Enter email address or hit Enter to skip.
 (Enter 'c' to cancel): [mail address]

- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
Please read the Terms of Service at:
https://letsencrypt.org/documents/LE-SA-v1.8-July-06-2026.pdf
You must agree in order to register with the ACME server. Do you agree?
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
(Y)es/(N)o: y

- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
Would you be willing, once your first certificate is successfully issued, to
share your email address with the Electronic Frontier Foundation, a founding
partner of the Let's Encrypt project and the non-profit organization that
develops Certbot? We'd like to send you email about our work encrypting the web,
EFF news, campaigns, and ways to support digital freedom.
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
(Y)es/(N)o: y
Account registered.
Requesting a certificate for [FQDN]

Successfully received certificate.
Certificate is saved at: /etc/letsencrypt/live/[FQDN]/fullchain.pem
Key is saved at:         /etc/letsencrypt/live/[FQDN]/privkey.pem
This certificate expires on 2027-02-07.
These files will be updated when the certificate renews.
Certbot has set up a scheduled task to automatically renew this certificate in the background.

- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
If you like Certbot, please consider supporting our work by:
 * Donating to ISRG / Let's Encrypt:   https://letsencrypt.org/donate
 * Donating to EFF:                    https://eff.org/donate-le
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
「Successfully received certificate.」と表示されれば成功
メッセージ中に記載の通り [/etc/letsencrypt/live/[FQDN]/] 配下に次の証明書が取得されている
cert.pem ⇒ SSLサーバー証明書(公開鍵含む)
chain.pem ⇒ 中間証明書
fullchain.pem ⇒ cert.pem と chain.pem が結合されたファイル
privkey.pem ⇒ 公開鍵に対する秘密鍵
インターネット側から当作業を実施するサーバーの 80 ポート宛てにアクセス可能であることは前提となります
FQDN (Fully Qualified Domain Name) : ホスト名.ドメイン名を省略なしで表記
証明書を取得したいFQDNが複数ある場合は、-d [証明書を取得したいFQDN] を複数指定
取得済みの証明書を更新する
# 有効期限が 30日未満の証明書を全て更新
# 有効期限の残り日数に関わらず更新したい場合は [--force-renewal] を合わせて指定
# certbot [--force-renewal] renew
Saving debug log to /var/log/letsencrypt/letsencrypt.log

- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
Processing /etc/letsencrypt/renewal/[FQDN].conf
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
Renewing an existing certificate for [FQDN]

- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
Congratulations, all renewals succeeded:
  /etc/letsencrypt/live/[FQDN]/fullchain.pem (success)
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
1.2 証明書を自動更新 (Let's Encrypt)
①登録前のテスト
まず以下の--dry-runオプションを使って自動更新をテストしてみる。このオプションでは、証明書は更新されずに動作確認のみ実施されるため、証明書の取得回数制限に引っかかる心配もない
# certbot renew --dry-run

Saving debug log to /var/log/letsencrypt/letsencrypt.log

- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
Processing /etc/letsencrypt/renewal/[FQDN].conf
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
Account registered.
Simulating renewal of an existing certificate for[FQDN]

- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
Congratulations, all simulated renewals succeeded:
  /etc/letsencrypt/live/fedora.korodes.com/fullchain.pem (success)
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
②Snap版certbotをインストールすると、証明書自動更新機能も合わせてインストールされます
# systemctl list-timers | less
NEXT                            LEFT LAST                              PASSED UNIT                         ACTIVATES
Mon 2026-11-09 15:07:39 JST    28min Mon 2026-11-09 14:10:10 JST    29min ago fwupd-refresh.timer          fwupd-refresh.service
Mon 2026-11-09 17:01:38 JST 2h 22min Mon 2026-11-09 13:35:12 JST  1h 4min ago dnf-makecache.timer          dnf-makecache.service
Tue 2026-11-10 00:00:00 JST       9h -                                      - sa-update.timer              sa-update.service
Tue 2026-11-10 00:05:34 JST       9h Mon 2026-11-09 13:22:22 JST 1h 17min ago logrotate.timer              logrotate.service
Tue 2026-11-10 00:05:42 JST       9h Mon 2026-11-09 13:35:02 JST  1h 4min ago plocate-updatedb.timer       plocate-updatedb.service
Tue 2026-11-10 02:59:00 JST      12h -                                      - snap.certbot.renew.timer     snap.certbot.renew.service
Tue 2026-11-10 13:12:22 JST      22h Mon 2026-11-09 13:12:22 JST 1h 27min ago systemd-tmpfiles-clean.timer systemd-tmpfiles-clean.service
Sun 2026-11-15 01:00:00 JST   5 days Sun 2026-11-08 10:03:54 JST            - raid-check.timer             raid-check.service
Mon 2026-11-16 00:29:20 JST   6 days Mon 2026-11-09 13:35:12 JST  1h 4min ago fstrim.timer                 fstrim.service

9 timers listed.
Pass --all to see loaded but inactive timers, too.
snap.certbot.renew.timer が登録されています
snap.certbot.renew.timer のユニットファイルを確認
# vi /etc/systemd/system/snap.certbot.renew.timer

[Unit]
# Auto-generated, DO NOT EDIT
Description=Timer renew for snap application certbot.renew
Requires=var-lib-snapd-snap-certbot-5911.mount
After=var-lib-snapd-snap-certbot-5911.mount
X-Snappy=yes

[Timer]
Unit=snap.certbot.renew.service
OnCalendar=*-*-* 02:59
OnCalendar=*-*-* 13:03

[Install]
WantedBy=timers.target
上記設定によるとOnCalenderパラメータで指定されている毎日2時59分と13時03分に更新を試みます(ただし、更新ごとにランダムに設定時刻が変更します)
snap.certbot.renew.serviceのユニットファイルを確認
# vi /etc/systemd/system/snap.certbot.renew.service

[Unit]
# Auto-generated, DO NOT EDIT
Description=Service for snap application certbot.renew
Requires=var-lib-snapd-snap-certbot-5911.mount
Wants=network.target
After=var-lib-snapd-snap-certbot-5911.mount network.target snapd.apparmor.service
X-Snappy=yes

[Service]
EnvironmentFile=-/etc/environment
ExecStart=/usr/bin/snap run --timer="00:00~24:00/2" certbot.renew
SyslogIdentifier=certbot.renew
Restart=no
WorkingDirectory=/var/snap/certbot/5911
TimeoutStopSec=30s
Type=oneshot
ただし、証明書を使用するWebサーバーの再起動は行われませんので、更新後に自動的に実行されるスクリプトを設定します
# vi /etc/letsencrypt/renewal-hooks/post/web_restart.sh
下記内容を記述
#!/bin/bash
systemctl reload httpd
# chmod 755 /etc/letsencrypt/renewal-hooks/post/web_restart.sh
2. Apache のhttps 化
下記をインストールする
# dnf -y install mod_ssl
2.1 ssl.conf ファイルの編集
# vi /etc/httpd/conf.d/ssl.conf

59 行目 コメント解除して変更
DocumentRoot "/var/www/html/[FQDN]"

60 行目 コメント解除して変更
ServerName [FQDN]:443

101行目 コメントにしてその下に追加
# SSLCertificateFile /etc/pki/tls/certs/localhost.crt
SSLCertificateFile /etc/letsencrypt/live/[FQDN]/cert.pem

109行目 コメントにしてその下に追加
# SSLCertificateKeyFile /etc/pki/tls/private/localhost.key
SSLCertificateKeyFile /etc/letsencrypt/live/[FQDN]/privkey.pem

119行目 追加
SSLCertificateChainFile /etc/letsencrypt/live/[FQDN]/chain.pem
Apache を再起動
# systemctl restart httpd
Firewallでhttpsを許可する
# firewall-cmd --add-service=https --permanent
success
# firewall-cmd --reload
success
2.2 HTTP 通信を HTTPS へリダイレクト
バーチャルホスト設定ファイルに下記を追記する
# vi /etc/httpd/conf.d/vhost.conf

<VirtualHost *:80>
RewriteEngine On  ←追加
RewriteCond %{HTTPS} off  ←追加
RewriteRule ^(.*)$ https://%{HTTP_HOST}%{REQUEST_URI} [R=301,L]  ←追加

DocumentRoot /var/www/html/[FQDN].com
ServerName [FQDN]
ServerAdmin [mail address]
ErrorLog logs/[FQDN].com.error_log
CustomLog logs/[FQDN].access_log combined
</VirtualHost>

<Directory "/var/www/html/[FQDN]">
Options FollowSymLinks
AllowOverride All
</Directory>
Apache再起動
# systemctl restart httpd
3. Mail サーバーにSSL/TLS(Let's Encrypt) の設定
3.1 メールサーバー用証明書の取得
一度web サーバーを止めてから行う
# systemctl stop httpd.service
# certbot certonly --standalone -d mail.[domain]
Saving debug log to /var/log/letsencrypt/letsencrypt.log
Requesting a certificate for mail.[domain]

Successfully received certificate.
Certificate is saved at: /etc/letsencrypt/live/mail.[domain]/fullchain.pem
Key is saved at:         /etc/letsencrypt/live/mail.[domain]/privkey.pem
This certificate expires on 2027-02-07.
These files will be updated when the certificate renews.
Certbot has set up a scheduled task to automatically renew this certificate in the background.

- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
If you like Certbot, please consider supporting our work by:
 * Donating to ISRG / Let's Encrypt:   https://letsencrypt.org/donate
 * Donating to EFF:                    https://eff.org/donate-le
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
3.2 Postfixの設定
# vi /etc/postfix/main.cf

726, 732行目 あたり: コメント化
#smtpd_tls_cert_file = /etc/pki/tls/certs/postfix.pem
#smtpd_tls_key_file = /etc/pki/tls/private/postfix.key

最終行に追記
smtpd_use_tls = yes
smtp_tls_mandatory_protocols = !SSLv2, !SSLv3
smtpd_tls_mandatory_protocols = !SSLv2, !SSLv3
smtpd_tls_cert_file = /etc/letsencrypt/live/mail.[domain]/fullchain.pem
smtpd_tls_key_file = /etc/letsencrypt/live/mail.[domain]/privkey.pem
smtpd_tls_session_cache_database = btree:${data_directory}/smtpd_scache
# vi /etc/postfix/master.cf

19,20,22,23行目 : コメント解除
submission inet n       -       n       -       -       smtpd
   -o syslog_name=postfix/submission
#  -o smtpd_forbid_unauth_pipelining=n
   -o smtpd_tls_security_level=encrypt
   -o smtpd_sasl_auth_enable=yes

40,41,43,44行目 : コメント解除
submissions     inet  n       -       n       -       -       smtpd
   -o syslog_name=postfix/smtps
#  -o smtpd_forbid_unauth_pipelining=no
   -o smtpd_tls_wrappermode=yes
   -o smtpd_sasl_auth_enable=yes
3.3 Dovecotの設定
# vi /etc/dovecot/dovecot.conf

48行目当たり:変更
ssl = yes

52,53行目当たり:コメントにして下に証明書/鍵ファイル指定追加
#cert_file = /etc/pki/dovecot/certs/dovecot.pem
#key_file = /etc/pki/dovecot/private/dovecot.pem
ssl_server_cert_file = /etc/letsencrypt/live/mail.[domain]/fullchain.pem
ssl_server_key_file = /etc/letsencrypt/live/mail.[domain]/privkey.pem
firewallでPort 587を許可する
# firewall-cmd --add-port=587/tcp --permanent
# firewall-cmd --reload
再起動
# systemctl restart postfix dovecot
3.4 Thunderbirdの設定
受信サーバー
Port : 143
Connection security : STARTTLS
Authentication method : Normal password
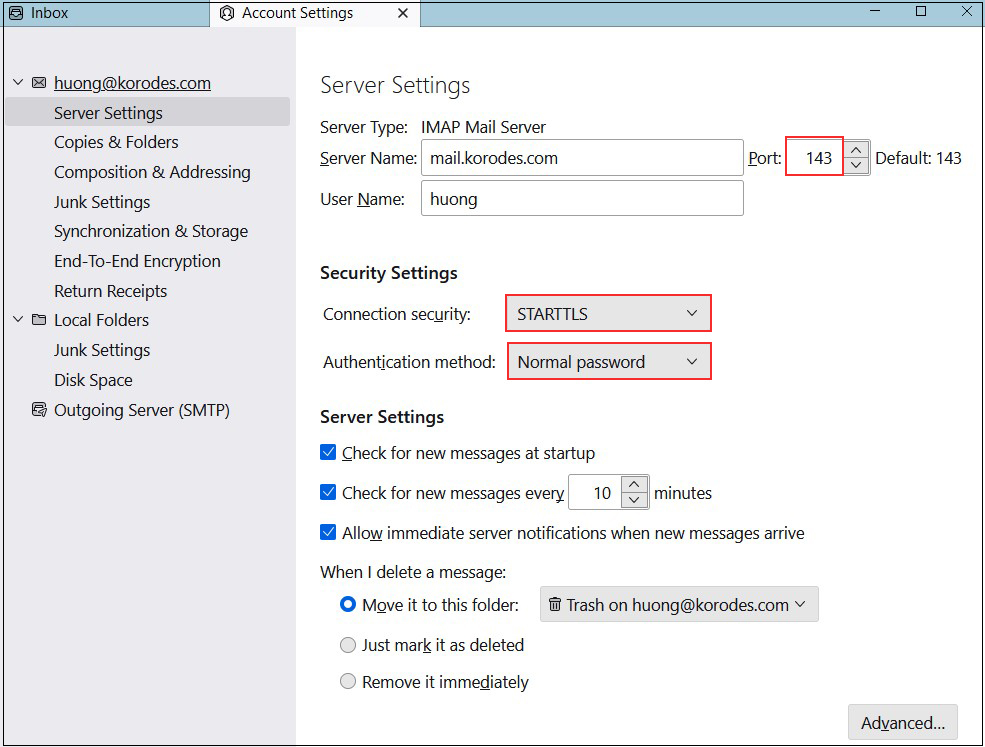
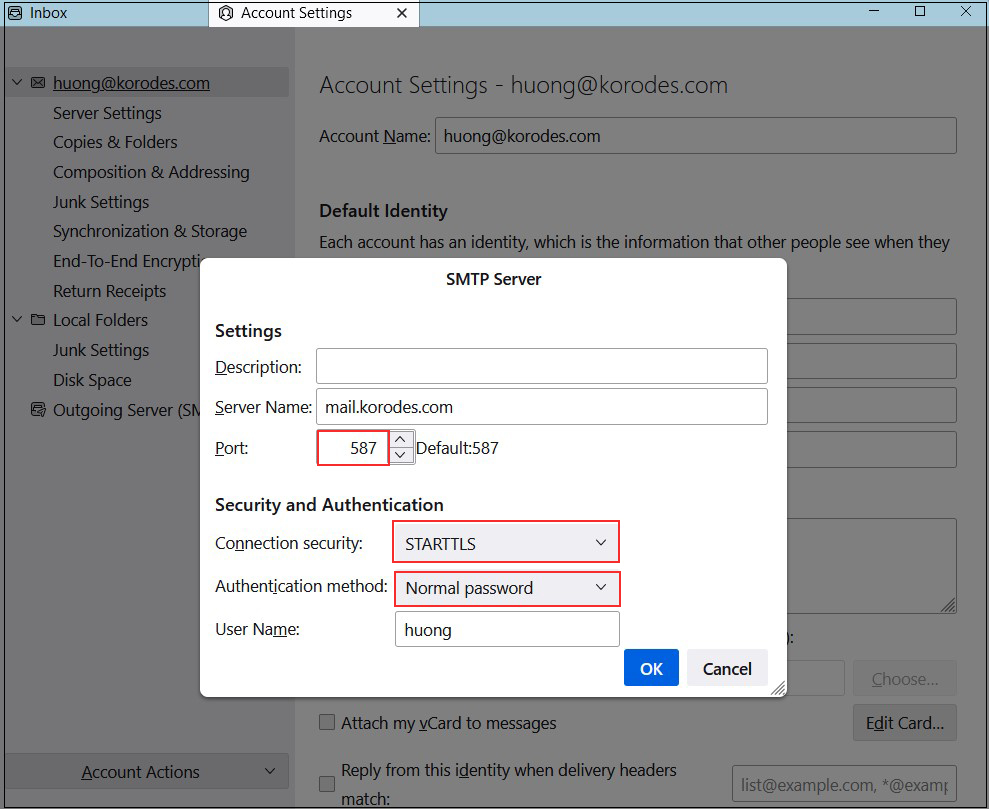
送信サーバー
Port : 587
Connection security : STARTTLS
Authentication method : Normal password